
最新整理思科交换机怎么查看任意接口的配置信息
思科交换机怎么查看任意接口的配置信息
像网桥那样,交换机将局域网分为多个冲突域,每个冲突域都是有独立的宽带,因此大大提高了局域网的带宽。
思科交换机怎么查看某个接口的配置?很多人对交换机不是很熟悉,下面由小编介绍下具体操作,需要的朋友可以参考下
具体步骤
1、首先思科交换机开机,电脑连接后,进入用户模式
2、输入e n a b l e或e n,进入特权模式
3、在特权模式下,输入s h o w i n t e r f a c e f0/1或s h o w
i n t f0/1,就可以查看f0/1接口的信息了
4、在接口信息中相关信息较多,包括接口是否启用(u p o r d o w n),该接口的M A C地址,该接口是全双工还是半双工(F u l l-d u p l e x o r H a l f-d u p l e x ),这里的f0/1的接口是处于启用状态(u p),并处于全双工
(F u l l-d u p l e x)。
5、我们再查看f0/2的接口信息,输入s h o w i n t
f0/2,这里的f0/2的接口是处于关闭状态(d o w n),并处于半双工(H a l f-d u p l e x)。
相关阅读:交换机工作原理过程
交换机工作于O S I参考模型的第二层,即数据链路层。
交换机内部的C P U会在每个端口成功连接时,通过将M A C地址和端口对应,形成一张M A C表。
在今后的通讯中,发往该M A C地址的数据包将仅送往其对应的端口,而不是所有的端口。
因此,交换机可用于划分数据链路层广播,即冲突域;但它不能划分网络层广播,即广播域。
交换机拥有一条很高带宽的背部总线和内部交换矩阵。
交换机的所有的端口都挂接在这条背部总线上,控制电路收到数据包以后,处理端口会查找内存中的地址对照表以确定目的M A C(网卡的硬件地址)的N I C(网卡)挂接在哪个端口上,通过内部交换矩阵迅速将数据包传送到目的端口,目的M A C若不存在,广播到所有的端口,接收端口回应后交换机会学习新的M A C地址,并把它添加入内部M A C地址表中。
使用交换机也可以把网络分段,通过对照I P地址表,交换机只允许必要的网络流量通
过交换机。
通过交换机的过滤和转发,可以有效的减少冲突域,但它不能划分网络层广播,即广播域。
CISCO根据IP或MAC查端口的教程
CISCO根据IP或MAC查端口的教程我们作为网络管理员,我们在日常工作中经常要在交换机上确定端口、IP地址与MAC地址的对应关系,不论是当我们通过网管软件或是日志服务器了解到某个IP地址的主机出现了问题,还是我们要重新整理网络拓扑结构,都需要确切的知道某个IP地址或者某个MAC的主机位于交换机的哪个端口上,接下来是小编为大家收集的CISCO根据IP或MAC查端口的教程方法,希望能帮到大家。
CISCO根据IP或MAC查端口的教程的方法一、网络管理员与系统管理员两种不同的工作模式这就涉及到两种不同的工作模式:网管员的做法是手里拿着一份IP地址分配表(虽然这张表的内容可能已经过时了),登录到交换机上查看IP地址与主机的对应关系。
这种方法对网络设备不做任何“硬”操作,安全系数高,但是获取到的信息不是百分之百的准确。
比如某台服务器的IP地址曾经做过改动,我们就有能因为在交换机上找不到原IP地址的信息从而认为这台服务器没有连接到网络上。
系统管理员则是先到服务器上查看IP地址信息,然后再想办法搞清楚这个IP地址是位于交换机的哪个端口上。
这种方法得到的信息很准备,但是比较耗时间。
通常情况下我们会先采用第一种方法来快速整理出IP、MAC和端口的对应关系,对于拿不准的信息则采用第二种方法逐一落实。
二、CISCO(思科)交换机查看三者对应关系的方法我单位了思科交换机进行组网,下面以该类型的交换机为例说明一下操作方法。
比如我们掌握了一个IP地址:10.230.0.67,需要了解这个IP地址所对应的MAC地址以及位于交换机上的哪个端口上,依次执行如下命令:(一)在交换机上执行ping操作Switch#pi ng 10.230.0.67Type escape seque nee to abort.Sending 5, 100-byte ICMP Echos to 10.230.0.67, timeout is 2 sec on ds:!!!!!Success rate is 100 perce nt (5/5), roun d-trip mi n/avg/max = 1/2/4 ms无论Ping通与否,我们都可以得到所需的信息。
思科交换机配置命令
思科交换机配置命令思科交换机配置命令大全美国思科公司,凭借它的IOS,Cisco公司在多协议路由器市场上处于绝对领先的地位。
目前,在Internet中,有近80%的路由器来自Cisco。
下面给大家介绍思科交换机配置命令大全,一起来了解一下吧! 思科交换机配置命令大全一、基本配置命令switch> 用户模式1:进入特权模式 enableswitch> enableswitch#2:进入全局配置模式 configure terminalswitch> enableswitch#c onfigure terminalswitch(conf)#3:交换机命名 hostname aptech2950 以 aptech2950 为例switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch-2950aptech2950(conf)#4:配置使能口令 enable password cisco 以 cisco 为例switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# enable password cisco5:配置使能密码 enable secret ciscolab 以 cicsolab 为例switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# enable secret ciscolab6:设置虚拟局域网 vlan 1 interface vlan 1switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# interface vlan 1aptech2950(conf-if)#ip address 192.168.1.1 255.255.255.0 配置交换机端口 ip 和子网掩码aptech2950(conf-if)#no shut 是配置处于运行中aptech2950(conf-if)#exitaptech2950(conf)#ip default-gateway 192.168.254 设置网关地址7:进入交换机某一端口 interface fastehernet 0/17 以 17 端口为例switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# interface fastehernet 0/17aptech2950(conf-if)#8:查看命令 showswitch> enableswitch# show version 察看系统中的所有版本信息show interface vlan 1 查看交换机有关 ip 协议的配置信息show running-configure 查看交换机当前起作用的配置信息show interface fastethernet 0/1 察看交换机 1 接口具体配置和统计信息show mac-address-table 查看 mac 地址表show mac-address-table aging-time 查看 mac 地址表自动老化时间9:交换机恢复出厂默认恢复命令switch> enableswitch# erase startup-configureswitch# reload10:双工模式设置switch> enableswitch#c onfigure terminalswitch2950(conf)#hostname aptch-2950aptech2950(conf)# interface fastehernet 0/17 以 17 端口为例aptech2950(conf-if)#duplex full/half/auto 有 full , half, auto 三个可选项11:cdp 相关命令switch> enableswitch# show cdp 查看设备的 cdp 全局配置信息show cdp interface fastethernet 0/17 查看 17 端口的 cdp 配置信息show cdp traffic 查看有关 cdp 包的统计信息show cdp nerghbors 列出与设备相连的 cisco 设备12:csico2950 的密码恢复拔下交换机电源线。
思科路由器交换机配置命令
思科路由器交换机配置命令1思科路由器常用配置命令一览表:1、Exec commands:<1-99> 恢复一个会话bfe 手工应急模式设置clear 复位功能clock 管理系统时钟configure 进入设置模式connect 打开一个终端copy 从tftp服务器拷贝设置文件或把设置文件拷贝到tftp服务器上debug 调试功能disable 退出优先命令状态disconnect 断开一个网络连接enable 进入优先命令状态erase 擦除快闪内存exit 退出exce模式help 交互帮助系统的描述lat 打开一个本地传输连接lock 锁定终端login 以一个用户名登录logout 退出终端mbranch 向树形下端分支跟踪多路由广播mrbranch 向树形上端分支跟踪反向多路由广播name-connection 给一个存在的网络连接命名no 关闭调试功能pad 打开X.29 PAD连接ping 发送回显信息ppp 开始点到点的连接协议reload 停机并执行冷启动resume 恢复一个活动的网络连接rlogin 打开远程注册连接rsh 执行一个远端命令send 发送信息到另外的终端行setup 运行setup命令show 显示正在运行系统信息slip 开始SLIP协议start-chat 在命令行上执行对话描述systat 显示终端行的信息telnet 远程登录terminal 终端行参数test 测试子系统内存和端口tn3270 打开一个tin3270连接trace 跟踪路由到目的地undebug 退出调试功能verify 验证检查闪烁文件的总数where 显示活动的连接which-route 执行OSI路由表查找并显示结果write 把正在运行的设置写入内存、网络、或终端x3 在PAD上设置X.3参数xremote 进入xremote模式2、#show ?access-expression 显示访问控制表达式access-lists 显示访问控制表apollo Apollo 网络信息appletalk Apple Talk 信息arap 显示Appletalk 远端通道统计arp 地址解析协议表async 访问路由接口的终端行上的信息bridge 前向网络数据库buffers 缓冲池统计clns CLNS网络信息clock 显示系统时钟cmns 连接模式网络服务信息compress 显示压缩状态configuration 非易失性内存的内容controllers 端口控制状态debugging 调试选项状态decnet DEC网络信息dialer 拨号参数和统计dnsix 显示Dnsix/DMPP信息entry 排队终端入口extended 扩展端口信息flash 系统闪烁信息flh-log 闪烁装载帮助日志缓冲区frame-relay 帧中继信息history 显示对话层历史命令hosts IP域名,查找方式,名字服务,主机表interfaces 端口状态和设置ip IP信息ipx Novell IPX信息isis IS-IS路由信息keymap 终端键盘映射lat DEC LAT信息line 终端行信息llc2 IBM LLC2 环路信息lnm IBM 局网管理local-ack 本地认知虚环路memory 内存统计netbios-cache NetBios命名缓冲存贮器内存node 显示已知LAT 节点ntp 网络时间协议processes 活动进程统计protocols 活动网络路由协议queue 显示队列内容queueing 显示队列设置registry 功能注册信息rhosts 远程主机文件rif RIF存贮器入口route-map 路由器信息sdlle 显示sdlc-llc2转换信息services 已知LAT服务sessions 远程连接信息smds SMDS信息source-bridge 源网桥参数和统计spanning-tree 跨越树形拓朴stacks 进程堆栈应用standby 热支持协议信息stun STUN状态和设置subsystem 显示子系统tcp TCP连接状态terminal 显示终端设置tn3270 TN3270 设置translate 协议转换信息ttycap 终端容易表users 显示终端行的信息version 系统硬、软件状态vines VINES信息whoami 当前终端行信息x25 X.25信息xns XNS信息xermote Xremote统计3、#config ?Memory 从非易失性内存设置Network 从TFTP网络主机设置Overwrite-network 从TFTP网络主机设置覆盖非易失性内存Terminal 从终端设置4、Configure commads:Access-list 增加一个访问控制域Apollo Apollo全局设置命令appletalk Appletalk 全局设置命令arap Appletalk远程进出协议arp 设置一个静态ARP入口async-bootp 修改系统启动参数autonomous-system 本地所拥有的特殊自治系统成员banner 定义注册显示信息boot 修改系统启动时参数bridge 透明网桥buffers 调整系统缓冲池参数busy-message 定义当连接主机失败时显示信息chat-script 定义一个调制解调器对话文本clns 全局CLNS设置子命令clock 设置时间时钟config-register 定义设置寄存器decnet 全局DEC网络设置子命令default-value 缺省字符位值dialer-list 创建一个拨号清单入口dnsix-nat 为审计提供DMDM服务enable 修改优先命令口令end 从设置模式退出exit 从设置模式退出frame-relay 全局帧中继设置命令help 交互帮助系统的描述hostname 设置系统网络名iterface 选择设置的端口ip 全局地址设置子命令ipx Novell/IPX全局设置命令keymap 定义一个新的键盘映射lat DEC本地传输协议line 设置终端行lnm IBM局网管理locaddr-priority-list 在LU地址上建立优先队列logging 修改注册(设备)信息login-string 定义主机指定的注册字符串map-class 设置静态表类map-list 设置静态表清单menu 定义用户接口菜单mop 设置DEC MOP服务器netbios NETBIOS通道控制过滤no 否定一个命令或改为缺省设置ntp 设置NTPpriority-list 建立特权列表prompt 设置系统提示符queue-list 建立常规队列列表rcmd 远程命令设置命令rcp-enable 打开Rep服务rif 源路由进程router-map 建立路由表或进入路由表命令模式router 打开一个路由进程rsh-enable 打开一个RSH服务sap-priority-list 在SAP或MAC地址上建立一个优先队列service 修改网络基本服务snmp-server 修改SNMP参数state-machine 定义一个TCP分配状态的机器stun STUN全局设置命令tacacs-server 修改TACACS队列参数terminal-queue 终端队列命令tftp-server 为网络装载请求提供TFTP服务tn3270 tn3270设置命令translate 解释全局设置命令username 建立一个用户名及其权限vines VINES全局设置命令x25 X.25 的第三级x29 X.29 命令xns XNS 全局设置命令xremote 设置Xremote5、(config)#ipGlobal IP configuration subcommands:Accounting-list 选择保存IP记帐信息的主机Accounting-threshold 设置记帐入口的最大数accounting-transits 设置通过入口的最大数alias TCP端口的IP地址取别名as-path BGP自治系统路径过滤cache-invalidate-delay 延迟IP路由存贮池的无效classless 跟随无类前向路由规则default-network 标志网络作为缺省网关候选default-gateway 指定缺省网(如果没有路由IP)domain-list 完成无资格主机的域名domain-lookup 打开IP域名服务系统主机转换domain-name 定义缺省域名forward-protocol 控制前向的、物理的、直接的IP广播host 为IP主机表增加一个入口host-routing 打开基于主机的路由(代理ARP和再定向)hp-host 打开HP代理探测服务mobile-host 移动主机数据库multicast-routing 打开前向IPname-server 指定所用名字服务器的地址ospf-name-lookup 把OSPF路由作为DNS名显示pim PIM 全局命令route 建立静态路由routing 打开IP路由security 指定系统安全信息source-route 根据源路由头的选择处理包subnet-zero 允许子网0子网tcp 全局TCP参数2思科交换机常用配置命令switch> 用户模式1:进入特权模式 enableswitch> enableswitch#2:进入全局配置模式 configure terminalswitch> enableswitch#c onfigure terminalswitch(conf)#3:交换机命名hostname aptech2950 以aptech2950为例switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch-2950aptech2950(conf)#4:配置使能口令 enable password cisco 以cisco为例switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# enable password cisco5:配置使能密码 enable secret ciscolab 以cicsolab为例switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# enable secret ciscolab6:设置虚拟局域网vlan 1 interface vlan 1switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# interface vlan 1aptech2950(conf-if)#ip address 192.168.1.1 255.255.255.0 配置交换机端口ip和子网掩码aptech2950(conf-if)#no shut 是配置处于运行中aptech2950(conf-if)#exitaptech2950(conf)#ip default-gateway 192.168.254 设置网关地址7:进入交换机某一端口interface fastehernet 0/17 以17端口为例switch> enableswitch#c onfigure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# interface fastehernet 0/17aptech2950(conf-if)#8:查看命令 showswitch> enableswitch# show version 察看系统中的所有版本信息show interface vlan 1 查看交换机有关ip 协议的配置信息show running-configure 查看交换机当前起作用的配置信息show interface fastethernet 0/1 察看交换机1接口具体配置和统计信息show mac-address-table 查看mac地址表show mac-address-table aging-time 查看mac地址表自动老化时间9:交换机恢复出厂默认恢复命令switch> enableswitch# erase startup-configureswitch# reload10:双工模式设置switch> enableswitch#c onfigure terminalswitch2950(conf)#hostname aptch-2950aptech2950(conf)# interface fastehernet 0/17 以17端口为例aptech2950(conf-if)#duplex full/half/auto 有full , half, auto 三个可选项11:cdp相关命令switch> enableswitch# show cdp 查看设备的cdp全局配置信息show cdp interface fastethernet 0/17 查看17端口的cdp配置信息show cdp traffic 查看有关cdp包的统计信息show cdp nerghbors 列出与设备相连的cisco设备12:csico2950的密码恢复拔下交换机电源线。
思科路由器交换机常用配置命令
1、进入SETUP模式Router#setup2、时间设置router#clock set hh:mm:ss date moth year3、router>show historyRouter>terminal history size lines4、router#show version5、router#show running-config6、router#show starup-config7、router(config)#hostname name主机命名8、router(config)#banner motd # message #开机时的固定显示信息9、router(config)#enable password password 特权模式明文密码10、router(config)#no enable password11、router(config)#enable secret password 特权模式加密密码12、router(config)#no enable secret13、router(config)#service password-encryption特权模式把明文密码加密密码,但没enable secret安全可以反解14、router(config)#line console控制台密码15、router(config-line)#login16、router(config-line)#password password17、router(config-line)#exec-timeout mm ss 禁止控制台会话自动退出18、router(config-line)#logging synchronous重显被打乱的控制台输入router(config)#no ip domain-lookup 禁止域名解析19、router(config)#line vty 0 4虚拟终端密码20、router(config-line)#login21、router(config-line)#password password22、router(config)#interface type number(slot/port)端口设置23、router(config-if)#ip address ip summast24、router(config-if)#clock rate 64000(时钟频率单位为bps,只在DCE端设置)25、router(config-if)#bandwith 64(带宽设置,单位为KB)26、router(config-if)#no shutdown(shutdown)27、router(config-if )#media-type type(10base) 为以太网端口选择适当的介质类型28、router(config-if )#ctrl+z保存退出到特权模式29、router#30、router>用户模式enable进入router#特权模式config terminal进入router(config)#全局配置模式31、Interface Router(config-if)#端口设置Subinterface Router(config-subif)# 子端口设置Controller Router(config-controller)# 控制口设置Line Router(config-line)# 虚拟口设置Router Router(config-router)# 路由设置IPX router Router(config-ipx-router)#IPX路由设置32、router#show interface33、router#show interface Ethernet 034、router#show interface serial 035、router#show running-config36、router#show starup-config37、router#show flash38、router#show controller39、router#show controller interface type40、router#show running-configrouter#copy running-config starup-configrouter#copy running-config tftprouter#copy starup-config tftprouter#copy flash tftprouter#copy tftp star-configrouter#copy tftp flash端口状态Serial1 is up, line protocol is up正常工作Serial1 is up, line protocol is down连接问题Serial1 is down, line protocol is down端口问题Serial1 is administratively down, line protocol is down人为关闭配置寄存器的值1、关闭路由器的电源重新启动按住ctrl+break键入进2、>3、>o/r 0x2142(跳过nvarm启动恢复密码)4、>I5、当系统提示是否进入setup模式时,按N6、router>7、router>enable8、router#9、进入修改后(包括密码、寄存器的值:0x2100为rom monitor启动、0x2101为setup 模式启动、0x2102为10、router#copy running-config starup-config11、router#reload12、也可以在router#setup进入setup模式静态路由协议设置router(config)#ip route network submask(要到达的网络号掩码)ip address(下一跳或出口ip地址)router(config)#ip route 0.0.0.0 s0(出口端口或下一跳IP地址)rip设置router(config)#router riprouter(config-router)#network network-numberrouter#show ip protocol查看RIP信息router#show ip route 查看路由表router#debug ip rip查看RIP更新信息router(config-router)#passive-interface e0(阻止发出作息)router(config-router)#ip rip receive version 1 2接收1、2RIP版本信息igrp设置router(config)#router igrp as numberrouter(config-router)#network network numberrouter#show ip route查看路由表router#debug ip igrp events查看IGRP路由更新大概信息router#debug ip igrp transaction查看IGRP路由更新详细信息Router(config-router)#variance multiplier 控制IGRP load balancingRouter(config-router)#traffic-share {balanced | min}控制load-balanced traffic 的分布eigrp设置router(config)#router eigrp as numberrouter(config-router)#network network numberrouter(config)#no auto-summry 关闭自动汇总router(config)# auto-summry 打开自动汇总(默认是打开的)router#show ip route eigrp 显示当前的路由表里的EIGRP条目router#show ip protocol 显示活动的路由协议进程的参数和当前的状态router#show ip eigrp neighbors 显示被EIGRP发现的邻居router#show ip eigrp traffic 显示发出和收到的IP EIGRP 包的数量router#show ip eigrp topology 显示IP EIGRP的拓扑表Router#debug ip eigrpospf设置1. Router(config)#router ospf process-idRouter(config-router)#network address(可以是网络号也可以是Ip地址mask(通配掩码)area area-idRouter(config-if)# ip ospf priority numbe 配置OSPF的优先级Router#show ip protocols 验证OSPF的配置Router#show ip route 显示路由器学到的所有路由Router#show ip ospf interface type number 显示area-ID 和邻接信息Router#show ip ospf neighbor 基于每接口显示OSPF邻居信息Router#debug ip ospf eventsRouter#debug ip ospf packet2. Router(config)# interface loopback number(lookback回路配置)Router(config-if)# ip address ip-address subnet-maskRouter(config-if)# ip ospf cost cost-numbe 修改OSPF 的Cost数值Router(config-if)# ip ospf authentication-key key 配置明文口令Router(config-if)# ip ospf messge-digest-key keyid md5 key 配置MD5口令(keyid和key必须配对一致,两邻居才可以通信)Router(config-route)# area area-id authentication [message-digest] message-digest为可选项,使用后路由器只传送口令消息的摘要(或散列)配置OSPF 区域的验证:3. Router(config-if)# ip ospf hello-interval seconds 配置hello间隔:Router(config-if)# ip ospf dead-interval seconds配置down机判断间隔访问列表1.标准访问列表(standard access lists):只使用源IP地址来做过滤决定Router(config)#access-list 10 deny 172.16.40.0 0.0.0.255Router(config)#access-list 10 permit anyRouter(config)#int e1Router(config-if)#ip access-group 10 out使用IP标准ACL来控制VTY线路的访问.Router(config)#access-list 50 permit 172.16.10.3Router(config)#line vty 0 4Router(config-line)#access-class 50 in删除IP标准ACLRouter(config-line)#no ip access-class 50 inRouter(config)#no access-list 502.扩展访问列表(extended access lists):它比较源IP地址和目标IP地址,层3的协议字段,层4端口号来做过滤决定Router(config)#access-list 110 deny tcp any host 172.16.30.5 eq 21Router(config)#access-list 110 deny tcp any host 172.16.30.5 eq 23Router(config)#access-list 110 permit ip any anyRouter(config)#int e1Router(config-if)#ip access-group 110 out3.虚拟通道访问router(config)#access-list 12 permit 192.89.55.0 0.0.0.255router(config)#line vty 0 4outer(config-line)#access-class 12 in3.show ip interface:只显示IP访问列表信息4.show ip interface:显示所有接口的信息和配置的ACL信息5.show ip interface [接口号]:显示具体某个接口的信息和配置的ACL信息6.show running-config:显示DRAM信息和ACL信息,以及接口对ACL的应用信息.交换机配置交换机上设置登陆口令Switch(config)# enable password level level passwordSwitch(config)# no enable password level level passwordhostname1900/2900(config)#hostname hostnameIP Address1900(config)#ip address {ip address} {mask}1900(config)#ip address 10.5.5.11 255.255.255.02950(config#interface vlan 12950(config-if)#ip address {ip_address} {mask}2950(config)#interface vlan 12950(config-if)#ip address 10.5.5.11 255.255.255.0 default gateway1900/2950(config)#ip default-gateway {ip address}1900/2950(config)#ip default-gateway 172.20.137.1查看交换机的IP地址1900#show ipIP address: 10.5.5.11Subnet mask: 255.255.255.0Default gateway: 10.5.5.3Management VLAN: 12950#show interface vlan 1Vlan1 is up, line protocol is upHardware is Cat5k Virtual Ethernet, address is 0010.f6a9.9800 (bia0010.f6a9.9800)Internet address is 172.16.80.79/24Broadcast address is 255.255.255.255设置双工选项1900(config)#interface e0/11900(config-if)#duplex {auto | full |full-flow-control | half}2950(config)#interface fe0/12950(config-if)#duplex {auto | full | half}设置端口速度:switch(config-if)# speed {10|100|auto}查勘双工选项Switch#show interfaces fastethernet0/3查看MAC地址表1900/2950#show mac-address-table配置永久MAC地址1900(config)#mac-address-table permanent {mac-address type module/port} 1900(config)#mac-address-table permanent 2222.2222.2222 ethernet 0/3 1900#show mac-address-table2950(config)#mac-address-table static mac_addr {vlan vlan_id} [interface int1 [int2 ... int15]]配置受限静态MAC地址1900(config)#mac-address-table restricted static {mac-address type module/port src-if-list}1900(config)#mac-address-table restricted static 1111.1111.1111 e0/4 e0/11900#show mac-address-table2950(config)#mac-address-table secure mac-addr interface [vlan vlan-id]2950(config)#mac-address-table secure 0003.3333.3333 fa 0/1 vlan 12950#show mac-address-table配置端口安全性1900(config-if)#port secure max-mac-count count1900(config)#interface e0/41900(config-if)#port secure1900(config-if)#port secure max-mac-count 11900(config)#address-violation {suspend | disable | ignore1900# show mac-address-table security2950(config-if)#port security max-mac-count count2950(config)#interface fa0/12950(config-if)#port security2950(config-if)#port security max-mac-count 102950(config-if)#port security action {shutdown | trap}2950#show mac-address-table secure2950#show port-security管理配置文件1900#copy nvram tftp://host/dst_file1900#copy tftp://host/src_file nvram1950#copy nvram tftp://10.1.1.1/wgswd.cfg2950#copy startup-config tftp://host/dst_file清除NVRAM1900#delete nvram2950#erase startup-configvlan配置1900 VLAN建立1900下,使用vlan [vlan#] name [name] [vlan#]命令, 如下: >en#config t(config)#hostname 19001900(config)#vlan 2 name sales1900(config)#vlan 3 name marketing1900(config)#vlan 4 name mis1900(config)#exit端口分配1900(config)#int e0/21900(config-if)#vlan-membership static 21900(config)#int e0/41900(config-if)#vlan-membership static 31900(config)#int e0/51900(config-if)#vlan-membership static 41900(config-if)#exit1900(config)#exitVLAN验证1900#sh vlan2900 VLAN建立在2950下创建VLAN,在特权模式下使用vlan database命令2950#vlan database2950(vlan)#vlan 2 name MarketingVLAN 2 modified:Name: Marketing2950(vlan)#vlan 3 name AccountingVLAN 3 added:Name: Accounting2950(vlan)#applyAPPLY complete2950(vlan)#Ctrl+C2950#端口分配2950下的端口配置,使用switchport access vlan [vlan#]命令, 2950(config-if)#int f0/22950(config-if)#switchport access vlan 22950(config-if)#int f0/32950(config-if)#switchport access vlan 32950(config-if)#int f0/42950(config-if)#switchport access vlan 42950(config-if)#exit2950(config)#exit验证配置信息,如下:2950#sh vlan或2950#sh vlan brieftrunk配置1900trunk配置1900(config)#int f0/261900(config-if)#trunk on2950下在接口配置模式,使用switchport命令,如下:2950(config)#int f0/122950(config-if)#switchport mode trunk2950(config-if)# switchport trunk encapsulation {isl|dot1q} 2950(config-if)#^Z将某VLAN从中继中删除2950(config-if)# switchport trunk allowed vlan remove vlan-list添加某个VLAN到中继线路2950(config-if)# switchport trunk allowed vlan add vlan-list Configuring Inter-VLAN Routing给连接1900的trunk端口配置,使用encapsulation isl [vlan#]命令,如下: 2600Router(config)#int f0/0.12600Router(config-subif)#encapsulation isl [vlan#]2600Router(config-subif)#ip add ip add submask给连接2950的这样配置,如下:2600Router(config)#int f0/0.12600Router(config-subif)#encapsulation dot1q [vlan#]2600Router(config-subif)#ip add ip add submaskVTP配置1900(config)#vtp server1900(config)#vtp domain noco1900(config)#vtp password noko在特权模式下使用show vtp命令验证,如下:1900#sh vtpVTP version: 1Configuration revision: 0Maximum VLANs supported locally: 1005Number of existing VLANs: 5VTP domain name: nocoVTP password: nokoVTP operating mode: Server2950如下:2950(config)#vtp mode server2950(config)#vtp domain noco验证信息,如下:2950#sh vtp ?counters VTP statisticsstatus VTP domain status2950#sh vtp statusNAT配置配置静态转换Router(config)#ip nat inside source static local-ip global-ipRouter(config-if)#ip nat insideRouter(config-if)#ip nat outside配置动态地址转换Router(config)#ip nat pool name start-ip end-ip {netmask netmask | prefix-length prefix-length}Router(config)#access-list access-list-number permit source [source-wildcard]Router(config)#ip nat inside source listaccess-list-number pool name配置OverloadingRouter(config)#access-list access-list-number permitsource source-wildcardRouter(config)#ip nat inside source listaccess-list-number interface interface overload清除NAT Translation TableRouter#clear ip nat translation * 清除所有的动态地址转换条目Router#clear ip nat translation inside global-iplocal-ip [outside local-ip global-ip] 清除一个简单的动态地址转换条目(内、外)Router#clear ip nat translation outsidelocal-ip global-ip清除一个简单的动态地址转换(外)Router#clear ip nat translation protocol inside global-ipglobal-port local-ip local-port [outside local-iplocal-port global-ip global-port] 清除一个扩展动态地址转换条目Show命令输出信息Router#show ip nat translations1.在基于IOS的交换机上设置主机名/系统名:switch(config)# hostname hostname在基于CLI的交换机上设置主机名/系统名:switch(enable) set system name name-string2.在基于IOS的交换机上设置登录口令:switch(config)# enable password level 1 password在基于CLI的交换机上设置登录口令:switch(enable) set passwordswitch(enable) set enalbepass3.在基于IOS的交换机上设置远程访问:switch(config)# interface vlan 1switch(config-if)# ip address ip-address netmaskswitch(config-if)# ip default-gateway ip-address在基于CLI的交换机上设置远程访问:switch(enable) set interface sc0 ip-address netmask broadcast-address switch(enable) set interface sc0 vlanswitch(enable) set ip route default gateway4.在基于IOS的交换机上启用和浏览CDP信息:switch(config-if)# cdp enableswitch(config-if)# no cdp enable为了查看Cisco邻接设备的CDP通告信息:switch# show cdp interface [type modle/port]switch# show cdp neighbors [type module/port] [detail]在基于CLI的交换机上启用和浏览CDP信息:switch(enable) set cdp {enable|disable} module/port为了查看Cisco邻接设备的CDP通告信息:switch(enable) show cdp neighbors[module/port][vlan|duplex|capabilities|detail]5.基于IOS的交换机的端口描述:switch(config-if)# de脚本ion de脚本ion-string基于CLI的交换机的端口描述:switch(enable)set port name module/number de脚本ion-string6.在基于IOS的交换机上设置端口速度:switch(config-if)# speed{10|100|auto}在基于CLI的交换机上设置端口速度:switch(enable) set port speed moudle/number {10|100|auto} switch(enable) set port speed moudle/number {4|16|auto}7.在基于IOS的交换机上设置以太网的链路模式:switch(config-if)# duplex {auto|full|half}在基于CLI的交换机上设置以太网的链路模式:switch(enable) set port duplex module/number {full|half}8.在基于IOS的交换机上配置静态VLAN:switch# vlan databaseswitch(vlan)# vlan vlan-num name vlaswitch(vlan)# exitswitch# configure teriminalswitch(config)# interface interface module/numberswitch(config-if)# switchport mode accessswitch(config-if)# switchport access vlan vlan-numswitch(config-if)# end在基于CLI的交换机上配置静态VLAN:switch(enable) set vlan vlan-num [name name]switch(enable) set vlan vlan-num mod-num/port-list9. 在基于IOS的交换机上配置VLAN中继线:switch(config)# interface interface mod/portswitch(config-if)# switchport mode trunkswitch(config-if)# switchport trunk encapsulation {isl|dotlq}switch(config-if)# switchport trunk allowed vlan remove vlan-listswitch(config-if)# switchport trunk allowed vlan add vlan-list在基于CLI的交换机上配置VLAN中继线:switch(enable) set trunk module/port [on|off|desirable|auto|nonegotiate]Vlan-range [isl|dotlq|dotl0|lane|negotiate]10.在基于IOS的交换机上配置VTP管理域:switch# vlan databaseswitch(vlan)# vtp domain domain-name在基于CLI的交换机上配置VTP管理域:switch(enable) set vtp [domain domain-name]11.在基于IOS的交换机上配置VTP 模式:switch# vlan databaseswitch(vlan)# vtp domain domain-nameswitch(vlan)# vtp {sever|cilent|transparent}switch(vlan)# vtp password password在基于CLI的交换机上配置VTP 模式:switch(enable) set vtp [domain domain-name] [mode{ sever|cilent|transparent }][password password]12. 在基于IOS的交换机上配置VTP版本:switch# vlan databaseswitch(vlan)# vtp v2-mode在基于CLI的交换机上配置VTP版本:switch(enable) set vtp v2 enable13. 在基于IOS的交换机上启动VTP剪裁:switch# vlan databaseswitch(vlan)# vtp pruning在基于CL I 的交换机上启动VTP剪裁:switch(enable) set vtp pruning enable14.在基于IOS的交换机上配置以太信道:switch(config-if)# port group group-number [distribution{source|destination}]在基于CLI的交换机上配置以太信道:switch(enable) set port channel moudle/port-rangemode{on|off|desirable|auto}15.在基于IOS的交换机上调整根路径成本:switch(config-if)# spanning-tree [vlan vlan-list] cost cost在基于CLI的交换机上调整根路径成本:switch(enable) set spantree portcost moudle/port costswitch(enable) set spantree portvlancost moudle/port [cost cost][vlan-list]16.在基于IOS的交换机上调整端口ID:switch(config-if)# spanning-tree[vlan vlan-list]port-priority port-priority 在基于CLI的交换机上调整端口ID:switch(enable) set spantree portpri {mldule/port}priorityswitch(enable) set spantree portvlanpri {module/port}priority [vlans] 17. 在基于IOS的交换机上修改STP时钟:switch(config)# spanning-tree [vlan vlan-list] hello-time secondsswitch(config)# spanning-tree [vlan vlan-list] forward-time seconds switch(config)# spanning-tree [vlan vlan-list] max-age seconds在基于CLI的交换机上修改STP时钟:switch(enable) set spantree hello interval[vlan]switch(enable) set spantree fwddelay delay [vlan]switch(enable) set spantree maxage agingtiame[vlan]18. 在基于IOS的交换机端口上启用或禁用Port Fast 特征:switch(config-if)#spanning-tree portfast在基于CLI的交换机端口上启用或禁用Port Fast 特征:switch(enable) set spantree portfast {module/port}{enable|disable}19. 在基于IOS的交换机端口上启用或禁用UplinkFast 特征:switch(config)# spanning-tree uplinkfast [max-update-ratepkts-per-second]在基于CLI的交换机端口上启用或禁用UplinkFast 特征:switch(enable) set spantree uplinkfast {enable|disable}[rate update-rate] [all-protocols off|on]20. 为了将交换机配置成一个集群的命令交换机,首先要给管理接口分配一个IP地址,然后使用下列命令: switch(config)# cluster enable cluster-name cv21. 为了从一条中继链路上删除VLAN,可使用下列命令:switch(enable) clear trunk module/port vlan-range22. 用show vtp domain 显示管理域的VTP参数.23. 用show vtp statistics显示管理域的VTP参数.24. 在Catalyst交换机上定义TrBRF的命令如下:switch(enable) set vlan vlan-name [name name] type trbrf bridgebridge-num[stp {ieee|ibm}]25. 在Catalyst交换机上定义TrCRF的命令如下:switch (enable) set vlan vlan-num [name name] type trcrf{ring hex-ring-num|decring decimal-ring-num} parent vlan-num26. 在创建好TrBRF VLAN之后,就可以给它分配交换机端口.对于以太网交换,可以采用如下命令给VLAN分配端口:switch(enable) set vlan vlan-num mod-num/port-num27. 命令show spantree显示一个交换机端口的STP状态.28. 配置一个ELAN的LES和BUS,可以使用下列命令:ATM (config)# interface atm number.subint multiointATM(config-subif)# lane serber-bus ethernet elan-name29. 配置LECS:ATM(config)# lane database database-nameATM(lane-config-databade)# name elan1-name server-atm-address les1-nsap-addressATM(lane-config-databade)# name elan2-name server-atm-address les2-nsap-addressATM(lane-config-databade)# name …30. 创建完数据库后,必须在主接口上启动LECS.命令如下:ATM(config)# interface atm numberATM(config-if)# lane config database database-nameATM(config-if)# lane config auto-config-atm-address31. 将每个LEC配置到一个不同的ATM子接口上.命令如下:ATM(config)# interface atm number.subint multipointATM(config)# lane client ethernet vlan-num elan-num32. 用show lane server 显示LES的状态.33. 用show lane bus显示bus的状态.34. 用show lane database显示LECS数据库可内容.35. 用show lane client显示LEC的状态.36. 用show module显示已安装的模块列表.37. 用物理接口建立与VLAN的连接:router# configure terminalrouter(config)# interface media module/portrouter(config-if)# de脚本ion de脚本ion-stringrouter(config-if)# ip address ip-addr subnet-maskrouter(config-if)# no shutdown38. 用中继链路来建立与VLAN的连接:router(config)# interface module/port.subinterfacerouter(config-ig)# encapsulation[isl|dotlq] vlan-numberrouter(config-if)# ip address ip-address subnet-mask39. 用LANE 来建立与VLAN的连接:router(config)# interface atm module/portrouter(config-if)# no ip addressrouter(config-if)# atm pvc 1 0 5 qsaalrouter(config-if)# atm pvc 2 0 16 ilnirouter(config-if)# interface atm module/port.subinterface multipoint router(config-if)# ip address ip-address subnet-maskrouter(config-if)# lane client ethernet elan-numrouter(config-if)# interface atm module/port.subinterface multipointrouter(config-if)# ip address ip-address subnet-namerouter(config-if)# lane client ethernet elan-namerouter(config-if)# …40. 为了在路由处理器上进行动态路由配置,可以用下列IOS命令来进行:router(config)# ip routingrouter(config)# router ip-routing-protocolrouter(config-router)# network ip-network-numberrouter(config-router)# network ip-network-number ()41. 配置默认路由:switch(enable) set ip route default gateway42. 为一个路由处理器分配VLANID,可在接口模式下使用下列命令:router(config)# interface interface numberrouter(config-if)# mls rp vlan-id vlan-id-num43. 在路由处理器启用MLSP:router(config)# mls rp ip44. 为了把一个外置的路由处理器接口和交换机安置在同一个VTP域中:router(config)# interface interface numberrouter(config-if)# mls rp vtp-domain domain-name45. 查看指定的VTP域的信息:router# show mls rp vtp-domain vtp domain name46. 要确定RSM或路由器上的管理接口,可以在接口模式下输入下列命令:router(config-if)#mls rp management-interface47. 要检验MLS-RP的配置情况:router# show mls rp48. 检验特定接口上的MLS配置:router# show mls rp interface interface number49. 为了在MLS-SE上设置流掩码而又不想在任一个路由处理器接口上设置访问列表:set mls flow [destination|destination-source|full]50. 为使MLS和输入访问列表可以兼容,可以在全局模式下使用下列命令:router(config)# mls rp ip input-acl51. 当某个交换机的第3层交换失效时,可在交换机的特权模式下输入下列命令:switch(enable) set mls enable52. 若想改变老化时间的值,可在特权模式下输入以下命令:switch(enable) set mls agingtime agingtime53. 设置快速老化:switch(enable) set mls agingtime fast fastagingtime pkt_threshold54. 确定那些MLS-RP和MLS-SE参与了MLS,可先显示交换机引用列表中的内容再确定:switch(enable) show mls include55. 显示MLS高速缓存记录:switch(enable) show mls entry56. 用命令show in arp显示ARP高速缓存区的内容。
思科交换机命令
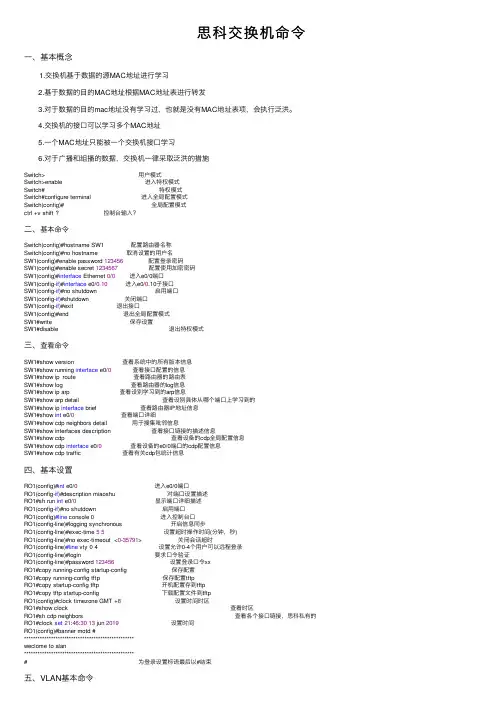
思科交换机命令⼀、基本概念 1.交换机基于数据的源MAC地址进⾏学习 2.基于数据的⽬的MAC地址根据MAC地址表进⾏转发 3.对于数据的⽬的mac地址没有学习过,也就是没有MAC地址表项,会执⾏泛洪。
4.交换机的接⼝可以学习多个MAC地址 5.⼀个MAC地址只能被⼀个交换机接⼝学习 6.对于⼴播和组播的数据,交换机⼀律采取泛洪的措施Switch> ⽤户模式Switch>enable 进⼊特权模式Switch# 特权模式 Switch#configure terminal 进⼊全局配置模式Switch(config)# 全局配置模式ctrl +v shift ? 控制台输⼊?⼆、基本命令Switch(config)#hostname SW1 配置路由器名称Switch(config)#no hostname 取消设置的⽤户名SW1(config)#enable password 123456 配置登录密码SW1(config)#enable secret 1234567 配置使⽤加密密码SW1(config)#interface Ethernet 0/0进⼊e0/0端⼝SW1(config-if)#interface e0/0.10进⼊e0/0.10⼦接⼝SW1(config-if)#no shutdown 启⽤端⼝SW1(config-if)#shutdown 关闭端⼝SW1(config-if)#exit 退出接⼝SW1(config)#end 退出全局配置模式SW1#write 保存设置 SW1#disable 退出特权模式三、查看命令SW1#show version 查看系统中的所有版本信息SW1#show running interface e0/0查看接⼝配置的信息SW1#show ip route 查看路由器的路由表SW1#show log 查看路由器的log信息SW1#show ip arp 查看设别学习到的arp信息SW1#show arp detail 查看设别具体从哪个端⼝上学习到的SW1#show ip interface brief 查看路由器IP地址信息SW1#show int e0/0查看端⼝详细SW1#show cdp neighbors detail ⽤于搜集吡邻信息SW1#show interfaces description 查看接⼝链接的描述信息SW1#show cdp 查看设备的cdp全局配置信息SW1#show cdp interface e0/0查看设备的e0/0端⼝的cdp配置信息SW1#show cdp traffic 查看有关cdp包统计信息四、基本设置RO1(config)#int e0/0进⼊e0/0端⼝RO1(config-if)#description miaoshu 对端⼝设置描述RO1#sh run int e0/0显⽰端⼝详细描述RO1(config-if)#no shutdown 启⽤端⼝RO1(config)#line console 0 进⼊控制台⼝RO1(config-line)#logging synchronous 开启信息同步RO1(config-line)#exec-time 55设置超时操作时间(分钟,秒)RO1(config-line)#no exec-timeout <0-35791> 关闭会话超时RO1(config-line)#line vty 0 4 设置允许0-4个⽤户可以远程登录RO1(config-line)#login 要求⼝令验证RO1(config-line)#password 123456设置登录⼝令xxRO1#copy running-config startup-config 保存配置RO1#copy running-config tftp 保存配置tftpRO1#copy startup-config tftp 开机配置存到tftpRO1#copy tftp startup-config 下载配置⽂件到tftpRO1(config)#clock timezone GMT +8设置时间时区RO1#show clock 查看时区RO1#sh cdp neighbors 查看各个接⼝链接,思科私有的RO1#clock set21:46:3013 jun 2019设置时间RO1(config)#banner motd #*************************************************weclome to alan*************************************************# 为登录设置标语最后以#结束五、VLAN基本命令 1.概念:虚拟的局域⽹络,⼯作于OSI参考模型的第⼆层。
cisco各类设备查看信息命令归纳

1、查看ARP缓存表 Router #show ip arp2、查看路由表 Router #show ip route3、查看接口状态 Router #show interface f0/04、查看基本配置 Router #show running-config5、查看版本信息 Router #show version6、查看路由器当前时间 Router #show clock7、查看路由协议配置 Router #show ip protocol8、打开RIP协议调试命令 Router #debug ip rip9、检测PPP连接状态和协商过程 Router #debug ppp packet10、查OSPF邻居列表 Router #show ip ospf neighbor (detail)详细11、查链路状态数据库 Router #show ip ospf database12、查OSPF的配置 Router #show ip ospf13、查OSPF的接口数据结构 Router #show ip ospf interface 接口14、查一条网络LSA通告信息 Router #show ip ospf database network15、显示链路状态数据库中的网络汇总LSA信息 Router #show ip ospf database summary16、查看数据库中列出的所有路由的LSA通告 Router #show ip ospf database router17、查看ASBR汇总LSA的信息 Router #show ip ospf database asbr-summary18、查看AS外部LSA的信息 Router #show ip ospf database external19、查NSSA外部LSA通告的信息 Router #show ip ospf database nssa-external20、查用来表示到达ABR和ASBR路由哭的路由 Router #show ip ospf border-routers21、查看OSPF协议配置信息 Router #show ip protocol22、查看路由器“邻接”的整个过程 Router #debug ip ospf adj23、查看每个OSPF数据包的信息 Router #debug ip ospf packet24、清空路由表 Router #clear ip route *25、查一条虚链路的状态 Router #show ip ospf virtual-link26、查看HSRP配置27、查看HSRP的状态 Router #show standby 1(组号) brief28、启用调试功能HSRP Router #debug standby29、查看串行链路的状态 Router #show controllers s0/030、显示路由器内存的大小,包括空闲内存的大小 Router #Show memory31、显示路由器的进程 Router #Show processes32、显示缓存器统计信息 Router #how buffers33、显示CDP表中所列相邻设备的信息 Router #Show cdp entry34、显示闪存的布局和内容信息 Router #Show flash35、显示关于本地管理接口(LMI)的统计信息 Router #Show frame-relay lmi36、显示关于连接的当前映射入口和信息 Router #Show frame-relay map37、显示关于帧中继接口的永久虚电路(pvc)的统计信息 Router #Show frame-relay pvc38、显示所有连接到路由器的用户 Router #show users39、显示当前存在的转换 Router#show ip nat translations40、查看NAT的统计信息 Router#show ip nat statistics41、查看IKE策略 Router# show crypto isakmp policy42、查看IPsce策略 Router# show crypto ipsec transform-set43、查看SA信息 Router# show crypto ipsec sa44、查看加密映射 Router# show crypto map。
思科交换机查看配置及日常维护命令
思科交换机查看配置及日常维护命令1.用户模式管理员通过超级终端或者telnet方式登陆交换机后,首先会进入XXX>模式,这里的尖括号代表用户模式,此模式下只能使用一些简单的查看命令,无法对设备进行配置。
2.特权模式管理员在用户模式下输入enable回车,经过密码验证后进入XXX#模式,这里的#代表特权模式,思科设备默认没有enable密码,此模式下可以使用show命令查看交换机的详细运行状态等信息。
3.全局配置模式管理员在如果需要对设备进行配置,例如增加vlan、修改网关、划分端口等操作时,必须先进入全局配置模式,在特权模式下输入configure terminal,会进入XXX(config)#模式,这里出现(config)#代表当前处于全局配置模式,全局配置模式退到特权模式输入命令exit。
大部分配制都需要在全局配置模式下输入。
4.查看思科设备当前运行配置特权模式下输入show running-config显示如下:由于配置一页显示不完,可以通过回车键逐行显示,也可以通过空格键逐页显示。
5.查看设备软件版本信息特权模式下输入show version显示如下:此命令用于显示设备型号、序列号、系统版本和在线时间等等信息。
6.查看系统时钟特权模式下输入show clock用于显示当前系统时钟,可以用于查看LOG日志后对应时钟分析异常LOG的发起时间。
7.查看LOG日志特权模式下输入show log用于显示系统突发状况,例如端口异常关闭,链路的通断,主备机切换等等许多信息,可以帮助管理员分析故障原因。
8.查看端口详细状态特权模式下输入show interface显示如下:此命令用于显示端口的详细信息,例如IP地址、MAC地址、带宽负载及输入输出速率等。
9.快速查看端口UP or DOWN特权模式下输入show interface description和show interface status第一条命令查看端口的连接状态与描述,第二条命令查看端口的链接状态、所属vlan以及速率双工。
(完整word版)思科交换机配置命令大全
(完整word版)思科交换机配置命令大全思科交换机配置命令大全switch> 用户模式1:进入特权模式enableswitch> enableswitch#2:进入全局配置模式configure terminalswitch> enableswitch#configure terminalswitch(conf)#3:交换机命名hostname aptech2950 以aptech2950为例switch> enableswitch#configure terminalswitch(conf)#hostname aptch-2950aptech2950(conf)#4:配置使能口令enable password cisco 以cisco为例switch> enableswitch#configure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# enable password cisco5:配置使能密码enable secret ciscolab 以cicsolab为例switch> enableswitch#configure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# enable secret ciscolab6:设置虚拟局域网vlan 1 interface vlan 1switch> enableswitch#configure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# interface vlan 1aptech2950(conf-if)#ip address 192.168.1.1 255.255.255.0 配置交换机端口ip和子网掩码aptech2950(conf-if)#no shut 是配置处于运行中aptech2950(conf-if)#exitaptech2950(conf)#ip default-gateway 192.168.254 设置网关地址7:进入交换机某一端口interface fastehernet 0/17 以17端口为例switch> enableswitch#configure terminalswitch(conf)#hostname aptch2950aptech2950(conf)# interface fastehernet 0/17aptech2950(conf-if)#8:查看命令showswitch> enableswitch# show version 察看系统中的所有版本信息show interface vlan 1 查看交换机有关ip 协议的配置信息show running-configure 查看交换机当前起作用的配置信息show interface fastethernet 0/1 察看交换机1接口具体配置和统计信息show mac-address-table 查看mac地址表show mac-address-table aging-time 查看mac地址表自动老化时间9:交换机恢复出厂默认恢复命令switch> enableswitch# erase startup-configureswitch# reload10:双工模式设置switch> enableswitch#c onfigure terminalswitch2950(conf)#hostname aptch-2950aptech2950(conf)# interface fastehernet 0/17 以17端口为例aptech2950(conf-if)#duplex full/half/auto 有full , half, auto 三个可选项11:cdp相关命令switch> enableswitch# show cdp 查看设备的cdp全局配置信息show cdp interface fastethernet 0/17 查看17端口的cdp配置信息show cdp traffic 查看有关cdp包的统计信息show cdp nerghbors 列出与设备相连的cisco设备12:csico2950的密码恢复拔下交换机电源线。
思科交换机的基本配置命令
思科交换机的基本配置命令网络技术知识其实也是弱电里面的一个难点,这个一般是在大学课程里面才能详细的学习,今天小编带来的是交换机的基本配置命令。
一、基本配置命令switch>用户模式1:进入特权模式enableswitch>enableswitch#2:进入全局配置模式configureterminalswitch>enableswitch#configureterminalswitch(conf)#3:交换机命名hostnameaptech2950以aptech2950为例switch>enableswitch#configureterminalswitch(conf)#hostnameaptch-2950aptech2950(conf)#4:配置使能口令enablepasswordcisco以cisco为例switch>enableswitch#configureterminalswitch(conf)#hostnameaptch2950aptech2950(conf)#enablepasswordcisco5:配置使能密码enablesecretciscolab以cicsolab为例switch>enableswitch#configureterminalswitch(conf)#hostnameaptch2950aptech2950(conf)#enablesecretciscolab6:设置虚拟局域网vlan1interfacevlan1switch>enableswitch#configureterminalswitch(conf)#hostnameaptch2950aptech2950(conf)#interfacevlan1aptech2950(conf-if)#ipaddress192.168.1.1255.255.255.0配置交换机端口ip和子网掩码aptech2950(conf-if)#noshut是配置处于运行中aptech2950(conf-if)#exitaptech2950(conf)#ipdefault-gateway192.168.254设置网关地址7:进入交换机某一端口interfacefasteher0/17以17端口为例switch>enableswitch#configureterminalswitch(conf)#hostnameaptch2950aptech2950(conf)#interfacefasteher0/17aptech2950(conf-if)#8:查看命令showswitch>enableswitch#showversion察看系统中的所有版本信息showinterfacevlan1查看交换机有关ip协议的配置信息showrunning-configure查看交换机当前起作用的配置信息showinterfacefastether0/1察看交换机1接口具体配置和统计信息showmac-address-table查看mac地址表showmac-address-tableaging-time查看mac地址表自动老化时间9:交换机恢复出厂默认恢复命令switch>enableswitch#erasestartup-configureswitch#reload10:双工模式设置switch>enableswitch#configureterminalswitch2950(conf)#hostnameaptch-2950aptech2950(conf)#interfacefasteher0/17以17端口为例aptech2950(conf-if)#duplexfull/half/auto有full,half,auto三个可选项11:cdp相关命令switch>enableswitch#showcdp查看设备的cdp全局配置信息showcdpinterfacefastether0/17查看17端口的cdp配置信息showcdptraffic查看有关cdp包的统计信息showcdpnerghbors列出与设备相连的cisco设备12:csico2950的密码恢复拔下交换机电源线。
思科光交常用命令汇总
思科光纤交换机基本指令show interface fc x/x transceiver details/link?url=zQ1lfBIy40JkgAxS9ONkbwVlLlsAq_3umIWd6O5mbObcQfcM3Ly 88PhZNq9fBUOq7FJy92eRp0oMmJc58Md8hNePQ0ZVXKpSAwPua6Cvlk_1、配置VSANVSAN的作用是隔离每一个交换机端口:switch2# conf tswitch2(config)# vsan databaseswitch2(config-vsan-db)# vsan 4000 name sw2switch2(config-vsan-db)# vsan 4000 interface fc1/1Traffic on fc1/1 may be impacted. Do you want to continue? (y/n) yswitch2(config-vsan-db)# vsan 4000 interface fc1/2Traffic on fc1/2 may be impacted. Do you want to continue? (y/n) yswitch2(config-vsan-db)# vsan 4000 interface fc1/72、创建ZONE并且添加ZONE成员。
witch2# conf tEnter configuration commands, one per line. End with CNTL/Z.switch2(config)# zone name db2_3652_1 vsan 4000switch2(config-zone)# member interface fc1/1switch2(config-zone)# member interface fc1/2switch2(config-zone)# zone name db2_3652_2 vsan 4000switch2(config-zone)# member interface fc1/7switch2(config-zone)# member interface fc1/83、配置ZONESET包含2个ZONEswitch2(config-zone)# zoneset name db2_3652 vsan 4000switch2(config-zoneset)# member db2_3652_1switch2(config-zoneset)# member db2_3652_24、察看ZONE成员switch2# show zonezone name db2_3652_1 vsan 4000interface fc1/1 swwn 20:00:00:0d:ec:be:0d:40interface fc1/2 swwn 20:00:00:0d:ec:be:0d:40zone name db2_3652_2 vsan 4000interface fc1/7 swwn 20:00:00:0d:ec:be:0d:40interface fc1/8 swwn 20:00:00:0d:ec:be:0d:405、察看ZONESET成员switch2# show zonesetzoneset name db2_3652 vsan 4000zone name db2_3652_1 vsan 4000interface fc1/1 swwn 20:00:00:0d:ec:be:0d:40interface fc1/2 swwn 20:00:00:0d:ec:be:0d:40zone name db2_3652_2 vsan 4000interface fc1/7 swwn 20:00:00:0d:ec:be:0d:40interface fc1/8 swwn 20:00:00:0d:ec:be:0d:406、激活ZONESETswitch2# conf tEnter configuration commands, one per line. End with CNTL/Z.switch2(config)# zoneset activate name db2_3652 vsan 4000Zoneset activation initiated. check zone status7、察看激活ZONE的switch2# show zone activezone name db2_3652_1 vsan 4000* fcid 0x810000 [interface fc1/1 swwn 20:00:00:0d:ec:be:0d:40]* fcid 0x810100 [interface fc1/2 swwn 20:00:00:0d:ec:be:0d:40]zone name db2_3652_2 vsan 4000* fcid 0x810200 [interface fc1/7 swwn 20:00:00:0d:ec:be:0d:40]* fcid 0x810300 [interface fc1/8 swwn 20:00:00:0d:ec:be:0d:40]conf t 进入conf模式show zone act 显示活跃的zone,注意记录zoneset名称和vsan名称zone name zone_name vsan xxx 新建zonemem interface fc x/x,fc x/x,fc x/x 加入端口exitzoneset name zoneset_name vsan xxx 编辑zonesetmem zone_name 加入zoneexitzoneset activate name zoneset_name vsan xxx 使zoneset生效copy running-config startup-config 保存配置。