
OSPF的明文和密文认证
R1
Router>en
Router#conf t
Router(config)#int loo 0
Router(config-if)#ip add 1.1.1.1 255.255.255.0 Router(config-if)#exi
Router(config)#int f 0/0
Router(config-if)#ip add 192.168.1.1 255.255.255.0 Router(config-if)#no shu
Router(config-if)#exi
Router(config)#router ospf 1
Router(config-router)#net 1.1.1.0 0.0.0.255 area 0 Router(config-router)#net 192.168.1.0 0.0.0.255 area 0 Router(config)#int f 0/0
Router(config-if)#ip ospf authentication
Router(config-if)#ip ospf authentication-key cisco
Router(config-if)#exi
R2
Router>
Router>en
Router#conf t
Router(config)#int loo 0
Router(config-if)#ip add 2.2.2.2 255.255.255.0 Router(config-if)#exi
Router(config)#int f1/0
Router(config-if)#ip add 192.168.2.1 255.255.255.0 Router(config-if)#no shu
Router(config-if)#exi
Router(config)#int f0/0
Router(config-if)#ip add 192.168.1.2 255.255.255.0 Router(config-if)#no shu
Router(config-if)#exi
Router(config)#router ospf 1
Router(config-router)#net 2.2.2.0 0.0.0.255 area 0 Router(config-router)#net 192.168.1.0 0.0.0.255 area 0 Router(config-router)#net 192.168.2.0 0.0.0.255 area 0 Router(config-router)#exi
Router(config)#int f 0/0
Router(config-if)#ip ospf authentication
Router(config-if)#ip ospf authentication-key cisco Router(config-if)#exi
Router(config)#int f1/0
Router(config-if)#ip ospf auth me
Router(config-if)#ip ospf message-digest-key 1 md5 ff Router(config-if)#exi
Router(config)#exi
R3
Router>en
Router#conf t
Router(config)#int loo 0
Router(config-if)#ip add 2.2.2.2 255.255.255.0 Router(config-if)#exi
Router(config)#int f 0/0
Router(config-if)#ip add 192.168.2.2 255.255.255.0 Router(config-if)#no shu
Router(config-if)#exi
Router(config)#router ospf 1
Router(config-router)#net 2.2.2.0 0.0.0.255 area 0 Router(config-router)#net 192.168.2.0 0.0.0.255 area 0 Router(config)#int f 0/0
Router(config-if)#ip ospf auth me
Router(config-if)#ip ospf message-digest-key 1 md5 ff Router(config-if)#exi。
ospf

ospf:收集链路状态信息完全了解网络拓扑,使用spf算法自主的计算路径。
ospf特性:open 无类手动汇总层次化结构收敛快速触发更新等价负载均衡邻居表(邻接关系数据库):领居建立过程:init state:一方组播hello包two-way state:双方收到hello包形成邻居关系exstart state:交换bdb包选举dr/bdrexchange state:交换bdb包交换lsdb摘要。
loading state:交换lsufull state:完全邻接拓朴表(lsdb,链路状态数据库):同一区域内每个路由器的lsdb一致lsa:包含接口ip前缀、开销、优先级,包含于LSU中,遵循水平分割原则。
lsa序列号:lsa的生存周期为60分钟,30分钟定期刷新,没有被刷新lsa将会在60分钟后被丢弃ospf的五种包:hello、dbd、lsr、lsu、lsackdbd、lsr、lsu需lsack确认路由表区域:CISCO建议每个区域的路由器不应超过50台。
双层结构:中转区域:又称骨干区域或核心区域(area 0),用于流量的中转没有终端用户。
常规区域:连接终端用户用于数据的收发。
常规区域必须与骨干区域直连,常规区域间不能有直连链路。
常规区域包括标准区域、末节区域、绝对末节区域、次末节区域。
区域的设计:凭经验公司:核心层做area 0,汇聚和接入做常规区域整个ospf网络在同一个AS中ospf中的路由器指的是:接口骨干路由器:位于area 0abr:abr连接的区域数不应超过3个,abr也可以是asbrasbr:重分发配置ospf:r1(conftig)# router ospf 1r1(config)# network …………area 0(等同于ip ospf 1 area 0)验证OSPF:sh ip protocolssh ip router ospfsh ip ospf interfacesh ip ospfsh ip ospf neighbor detaildebug ip ospf eventsdebug ip ospf adjospf的网络类型(dead time=4*hello time)点到点(PPP、HDLC串口):直接邻接,hello-time 10s2、广播(LAN):选dr/bdr,hello-time 10sdrother与dr/bdr:邻接;drother之间:领居dr组播224.0.0.5;drother组播224.0.0.6dr的轮选:数值最大接口优先级(默认值1)ip ospf priority ?2、rid:环回地址、物理接口ip地址router-id ip address(次于优先级,ip地址可以为存在或不存在,不能指定其他路由器已有IP)dr稳定性,先到先得clear ip ospf process(清除ospf进程让dr重选;清除ospf进程邻居关系重新形成)3、ospf在nbma网络运行的公有模式:1、nbma:默认模式hello time 30s在hub-spoke拓朴,选dr/bdr,同一子网,中心路由器为dr/bdr边缘路由器(spoke)相互之间要做dlci的映射(dlci复用)中心路由器手动指定领居(如:nei 192.168.1.2 priority 0把spoke优先级设为0)2、p2m:hello time 30s同一子网,不选dr/bdr,多点fr子接口无需修改网络类型,邻接关系可以正常建立,但路由就没法学到,因此建议在多点fr子接口修改网络类型。
等级测评师初级技术试题

2、口令复杂度应有要求,所以复杂的口令可以不用修改。( X )
3、为特权用户设置口令时,应当使用enablepassword命令,该命令用于
设定具有管理权限的口令。( X )
4、在SSL握手信息中,采用了RSA、MD5等加密技术来实现机密性和
A. MorrisonB. Wm. $*F2m5@C. 27776394 D. wangjing1977
5、息安全领域内最关键和最薄弱的环节是______。
A.技术B.策略C.管理制度D.人
6、对于提高人员安全意识和安全操作技能来说,以下所列的安全管理最有效的是______。
A.安全检查B教育和培训C.责任追究 D.制度约束
A.30天60天B. 60天90天
C. 70天90天D. 50天70天
8.Windows操作系统中,本地登录权限对用户组不开放。( D )
A.Guest B.Administartors ersD.Everyone
12、为了数据传输时不发生数据截获和信息泄密,采取了加密机制。这种做法体现了信息安全的属性。( A )
A.广播所有相连的设备 B.丢弃 C.修改源地址转发
8、功能测试不能实现以下哪个功能( D )
A.漏洞 B.补丁 C.口令策略 D.全网访问控制策略
9、linux查看目录权限的命令( B )
A. ls -a B.ls -l C. dir -a D. dir -l
10、三级系统网络安全的设备防护有( C )个检查项。
A.保密性 B.完整性 C.可靠性 D.可用性
1、向有限的空间输入超长的字符串是哪一种攻击手段? (A)
A、缓冲区溢出 B、网络监听 C、拒绝服务 D、IP欺骗
OSPF 认证

实验名称:OSPF 认证实验设备:路由器3700二台(模拟器GNS3)实验拓补:基本配置:Router>enableRouter#configure terminalRouter(config)#hostname R1R1(config)#interface serial 1/0R1(config-if)#ip address 192.168.100.1 255.255.255.252R1(config-if)#no shutdownR1(config)#interface loopback 10R1(config-if)#ip address 192.168.1.1 255.255.255.0R1(config)#router ospf 10R1(config-router)#network 192.168.1.0 0.0.0.255 area 0R1(config-router)#network 192.168.100.0 0.0.0.3 area 0 Router>enableRouter#configure terminalRouter(config)#hostname R2R2(config)#interface loopback 10R2(config-if)#ip address 192.168.2.1 255.255.255.0R2(config)#interface serial 1/0R2(config-if)#ip address 192.168.100.2 255.255.255.252R2(config-if)#clock rate 64000R2(config-if)#no shutdownR2(config)#router ospf 20R2(config-router)#network 192.168.2.0 0.0.0.255 area 0R2(config-router)#network 192.168.100.0 0.0.0.3 area 0认证方式:一、明文认证R1 配置R1(config)#interface serial 1/0R1(config-if)#ip ospf authentication /**在所有参与OSPF进程的接口启用明文验证R1(config-if)#ip ospf authentication-key cisco /**设置明文口令R1(config)#interface loopback 10R1(config-if)#ip ospf authenticationR1(config-if)#ip ospf authentication-key ciscoR1(config)#router ospf 10R1(config-router)#area 0 authentication /**声明在Area 0 使用明文验证R2配置R2(config)#interface serial 1/0R2(config-if)#ip ospf authenticationR2(config-if)#ip ospf authentication-key ciscoR2(config)#interface loopback 10R2(config-if)#ip ospf authenticationR2(config-if)#ip ospf authentication-key ciscoR2(config)#router ospf 20R2(config-router)#area 0 authentication二、MD5认证R1 配置R1(config)#interface serial 1/0R1(config-if)#no ip ospf authentication-key /**取消以前的明文密码R1(config-if)#ip ospf authentication message-digest /**启用MD5的密文验证R1(config-if)#ip ospf message-digest-key 1 md5 cisco /**设置密文验证的口令R1(config)#interface loopback 10R1(config-if)#no ip ospf authentication-keyR1(config-if)#ip ospf authentication message-digestR1(config-if)#ip ospf message-digest-key 1 md5 ciscoR1(config)#router ospf 10R1(config-router)#area 0 authentication message-digest /**声明Area 0 使用密文验证R2 配置R2(config)#interface serial 1/0R2(config-if)#no ip ospf authentication-keyR2(config-if)#ip ospf authentication message-digestR2(config-if)#ip ospf message-digest-key 1 md5 ciscoR2(config)#interface loopback 10R2(config-if)#no ip ospf authentication-keyR2(config-if)#ip ospf authentication message-digestR2(config-if)#ip ospf message-digest-key 1 md5 ciscoR2(config)#router ospf 20R2(config-router)#area 0 authentication message-digestR2#show ip ospf interface serial 1/0 /** 查看配置的验证。
OSPF的验证机制
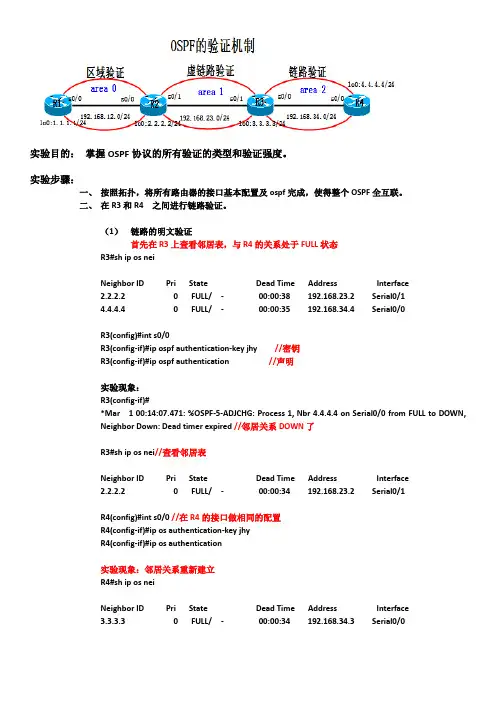
实验目的:掌握OSPF协议的所有验证的类型和验证强度。
实验步骤:一、按照拓扑,将所有路由器的接口基本配置及ospf完成,使得整个OSPF全互联。
二、在R3和R4 之间进行链路验证。
(1)链路的明文验证首先在R3上查看邻居表,与R4的关系处于FULL状态R3#sh ip os neiNeighbor ID Pri State Dead Time Address Interface2.2.2.2 0 FULL/ - 00:00:38 192.168.23.2 Serial0/14.4.4.4 0 FULL/ - 00:00:35 192.168.34.4 Serial0/0R3(config)#int s0/0R3(config-if)#ip ospf authentication-key jhy //密钥R3(config-if)#ip ospf authentication //声明实验现象:R3(config-if)#*Mar 1 00:14:07.471: %OSPF-5-ADJCHG: Process 1, Nbr 4.4.4.4 on Serial0/0 from FULL to DOWN,Neighbor Down: Dead timer expired //邻居关系DOWN了R3#sh ip os nei//查看邻居表Neighbor ID Pri State Dead Time Address Interface2.2.2.2 0 FULL/ - 00:00:34 192.168.23.2 Serial0/1R4(config)#int s0/0 //在R4的接口做相同的配置R4(config-if)#ip os authentication-key jhyR4(config-if)#ip os authentication实验现象:邻居关系重新建立R4#sh ip os neiNeighbor ID Pri State Dead Time Address Interface3.3.3.3 0 FULL/ - 00:00:34 192.168.34.3 Serial0/0(2)链路的密文验证R3(config-if)#ip os message-digest-key 1 md5 jhy//密钥R3(config-if)#ip os authentication message-digest //声明R4(config-if)#ip os message-digest-key 1 md5 jhyR4(config-if)#ip os authentication message-digest三、Area 0 的区域验证。
OSPF的基本工作原理
Hello报文
用于发现和建立邻居关系,通 过定期发送Hello报文来维护 邻居关系。
路由表报文
用于在OSPF区域内传递路由 信息,实现路由表的同步。
链路状态请求报文
用于请求其他路由器发送缺失 的链路状态记录,以完成链路 状态数据库的同步。
03 OSPF路由计算
OSPF路由表的生成
01
生成OSPF路由表
OSPF路由的优选原则
最短路径
01
OSPF路由器在选择最佳路径时,会优先选择路径长度最短的路
径。
稳定性
02
OSPF路由器还会考虑路径的稳定性,通常会选择经过的路由器
数量最少、网络带宽最高、负载最轻的路径。
可靠性
03
在选择路径时,OSPF路由器还会考虑路径的可靠性,优先选择
经过的路由器和链路状态更好的路径。
路由更新
当网络拓扑发生变化时,OSPF路由器会发送链路状态更 新报文,通知其他路由器网络变化情况,其他路由器会更 新自己的链路状态数据库和路由表。
OSPF协议的消息类型和交换方式
链路状态更新报文
用于同步链路状态信息,当网 络发生变化时,发送链路状态 更新报文通知其他路由器。
数据库描述报文
用于描述链路状态数据库的内 容,帮助其他路由器快速同步 链路状态数据库。
02
数据库同步
OSPF路由器通过收集网络中的链路 状 Nhomakorabea信息,构建一个链路状态数据库 ,并根据该数据库生成OSPF路由表 。
当网络发生变化时,OSPF路由器会 通过数据库同步机制,将链路状态信 息更新到其他OSPF路由器中,确保 所有路由器的链路状态数据库保持一 致。
03
路由计算
OSPF路由器根据链路状态数据库中 的信息,按照一定的算法计算出到达 各个目的网络的最佳路径,并将这些 路径添加到OSPF路由表中。
OSPF Authentication配置详解
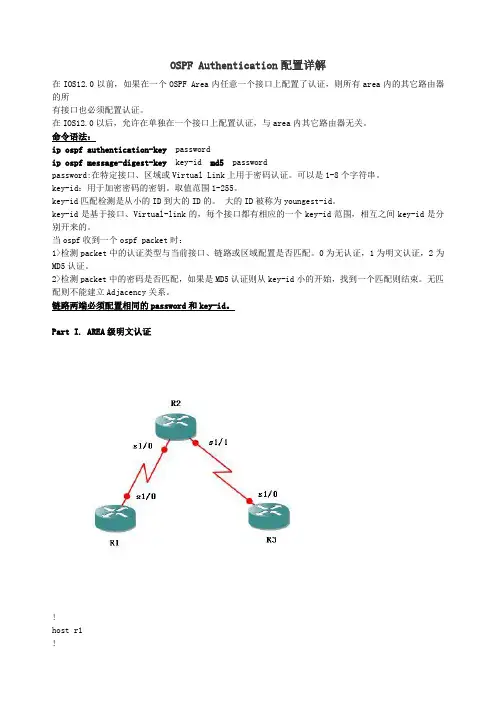
OSPF Authentication配置详解在IOS12.0以前,如果在一个OSPF Area内任意一个接口上配置了认证,则所有area内的其它路由器的所有接口也必须配置认证。
在IOS12.0以后,允许在单独在一个接口上配置认证,与area内其它路由器无关。
命令语法:ip ospf authentication-key passwordip ospf message-digest-key key-id md5 passwordpassword:在特定接口、区域或Virtual Link上用于密码认证。
可以是1-8个字符串。
key-id:用于加密密码的密钥。
取值范围1-255。
key-id匹配检测是从小的ID到大的ID的。
大的ID被称为youngest-id。
key-id是基于接口、Virtual-link的,每个接口都有相应的一个key-id范围,相互之间key-id是分别开来的。
当ospf收到一个ospf packet时:1>检测packet中的认证类型与当前接口、链路或区域配置是否匹配。
0为无认证,1为明文认证,2为MD5认证。
2>检测packet中的密码是否匹配,如果是MD5认证则从key-id小的开始,找到一个匹配则结束。
无匹配则不能建立Adjacency关系。
链路两端必须配置相同的password和key-id。
Part I. AREA级明文认证!host r1description conn_to_r2ip add 192.168.1.1 255.255.255.0ip ospf authentication-key cisco!router ospf 100router-id 10.0.0.1net 192.168.1.0 0.0.0.255 area 0area 0 authentication!-------------------------------------------- !host r2!int s1/0description conn_to_r1ip add 192.168.1.2 255.255.255.0ip ospf authentication-key cisco!router ospf 100router-id 10.0.0.2net 192.168.1.0 0.0.0.255 area 0area 0 authentication!++++++++++++++++++++++++++++++service password-encryptionshow ip ospf neighbordebug ip ospf events++++++++++++++++++++++++++++++Part II. AREA级md5认证!host r1!int s1/0description conn_to_r2ip add 192.168.1.1 255.255.255.0ip ospf message-digest-key 1 md5 cisco!router ospf 100router-id 10.0.0.1net 192.168.1.0 0.0.0.255 area 0area 0 authentication message-digest!---------------------------------------------!int s1/0description conn_to_r1ip add 192.168.1.2 255.255.255.0ip ospf message-digest-key 1 md5 cisco!router ospf 100router-id 10.0.0.2net 192.168.1.0 0.0.0.255 area 0area 0 authentication message-digest!Part III. AREA级md5认证切换因为md5认证在收到时是从认证密码池中依次匹配密码的(密码ID从小到大),所以它可以同时配置多个密码,进而可以实现在多个密码中平滑的过度。
OSPF网络类型,DR和BDR理解
DR和BDR选举要先看优先级,再看Router-ID。如果DR失效,BDR会立即生效(BDR变成DR),不会重新选举DR,就算路由器中有优先高的,也不会立即选举。BDR变成DR后,在选举一个新的BDR,这时不会影响路由的计算。路由器接口的优先级:Router(config-if)#ip ospf priority {0 - 255}
3.OSPF的LSA类型:分为12种类型,主要学1、2、3、4、5、7等六个LSA类型。
LSA1 -- Router LSA(路由LSA)
LSA2 -- Network LSA(网络LSA)
LSA3 -- Network summary(网络汇总LSA)
LSA4 -- ASBR summary
2. 在NBMA和广播网络上需要选举DR与BDR,而在点到多点网络中没有DR与BDR。
NBMA用单播发送报文,需要手工配置邻居。点到多点采用多播方式发送报文。
OSPF,对于点对点与点对多点来说,没有必要选取DR与BDR。这时候采用组播地址224.0.0.5.
OSPF,对于NBMA与广播型网络来说,有必要选取DR与BDR。(会产生不必要的LSA通告,全网互通下产生N*(N-1)/2条),这时候DR采用组播地址224.0.0.5,接受地址224.0.0.6 BDR采用组播地址224.0.0.6,接受地址224.0.0.5 DRother之间不exchangeLSA信息,信息由DR发出。
密文认证:
r2(config)#router ospf 100
r2(config-router)#area 0 authentication message-digest
r2(config-if)#ip ospf authentication message-digest
OSPF 的四种认证方式总结
OSPF 的四种认证方式OSPF的四种认证,基于区域的认证两种:简单口令认证,MD5。
基于链路的认证有两种:简单口令认证,MD5。
简单介绍一下:基于区域的简单口令认证:在R2上的配置如下:Router(config)#router ospf 100Router(config-router)#area 0 authenticationRouter(config)#int s1/3Router(config-if)#ip ospf authentication-key tyt在R3上的配置也是一样的,当你配置完一方时,邻居关系会断掉,另一方配置完后,邻居关系会重启,再者两边的密码一定要一样,不然不行。
基于区域的MD5认证:在R2上的配置如下:Router(config)#router ospf 100Router(config-router)#area 0 authentication message-digestRouter(config)#int s1/3Router(config-if)#ip ospf message-digest-key 1 md5 tyt在R3上的配置也是一样的,当你配置完一方时,邻居关系会断掉,另一方配置完后,邻居关系会重启,再者两边的密码一定要一样,不然不行。
基于链路的简单口令认证:在R2上的配置如下:Router(config)#int s1/3Router(config-if)#ip ospf authenticationRouter(config-if)#ip ospf authentication-key tyt这个很简单,在R3上的配置也是这样的基于链路的MD5认证的配置:在R2上的配置如下:Router(config)#int s1/3Router(config-if)#ip ospf authentication message-digestRouter(config-if)#ip ospf message-digest-key 1 md5 tyt其实在认证配置方面很简单!因为文档太小的话,文库会不认上传,所以在后面加些无关紧要的东西,可以删掉!实验 1-2:在NAT中使用Access List 和Route Maps【实验目的】:在本次实验中,你需要使用网络地址转换(NAT)去允许内网路由器(PxR3 和 PxR4)从TFTP服务器下载配置文件为了完成本次实验,你需要完成下列任务:∙建立在NAT中需要使用的访问控制列表∙在NAT中使用ROUTE-MAPS执行分开的并发地址转换。
OSPF 的四种认证方式总结
OSPF 的四种认证方式OSPF的四种认证,基于区域的认证两种:简单口令认证,MD5。
基于链路的认证有两种:简单口令认证,MD5。
简单介绍一下:基于区域的简单口令认证:在R2上的配置如下:Router(config)#router ospf 100Router(config-router)#area 0 authenticationRouter(config)#int s1/3Router(config-if)#ip ospf authentication-key tyt在R3上的配置也是一样的,当你配置完一方时,邻居关系会断掉,另一方配置完后,邻居关系会重启,再者两边的密码一定要一样,不然不行。
基于区域的MD5认证:在R2上的配置如下:Router(config)#router ospf 100Router(config-router)#area 0 authentication message-digestRouter(config)#int s1/3Router(config-if)#ip ospf message-digest-key 1 md5 tyt在R3上的配置也是一样的,当你配置完一方时,邻居关系会断掉,另一方配置完后,邻居关系会重启,再者两边的密码一定要一样,不然不行。
基于链路的简单口令认证:在R2上的配置如下:Router(config)#int s1/3Router(config-if)#ip ospf authenticationRouter(config-if)#ip ospf authentication-key tyt这个很简单,在R3上的配置也是这样的基于链路的MD5认证的配置:在R2上的配置如下:Router(config)#int s1/3Router(config-if)#ip ospf authentication message-digestRouter(config-if)#ip ospf message-digest-key 1 md5 tyt其实在认证配置方面很简单!因为文档太小的话,文库会不认上传,所以在后面加些无关紧要的东西,可以删掉!实验 1-2:在NAT中使用Access List 和Route Maps【实验目的】:在本次实验中,你需要使用网络地址转换(NAT)去允许内网路由器(PxR3 和 PxR4)从TFTP服务器下载配置文件为了完成本次实验,你需要完成下列任务:•建立在NAT中需要使用的访问控制列表•在NAT中使用ROUTE-MAPS执行分开的并发地址转换。
「陪我一起练」—华为数通eNSP模拟实验17:ospf认证
「陪我一起练」—华为数通eNSP模拟实验17:ospf认证刚刚通过了头条的科技领域创作者,很是开心,本来以为这样的兴趣认证可以加V的,原来只是在后面加了一行字而已,看来我还是太年轻了!~继续继续,没有认证的网络是不安全的,ospf协议也一样,今天我们就一起来看看如何进行ospf认证吧。
一、拓扑结构与上节拓扑一样,其实可以不用这么复杂,我只是懒得改而已!进行ospf认证,骨干区域采用区域认证,常规区域采取接口认证方式。
二、业务配置上节的配置保持不变,下面只帖出新增加(高亮)的认证命令。
R1路由器ospf区域(area0)认证认证方式md5,cipher为密文显示,密码为fight。
R2路由器ospf区域(area0)认证认证方式与R1路由器相同。
R2路由器ospf接口(area1)认证认证方式simple(明文),密码为addoil。
R3路由器ospf接口(area1)认证与R2路由器认证方式及密码相同。
请注意虚链路相当于是骨干区域area 0的延伸,那么骨干区域做了认证,延伸部分的虚链路也需要参与认证,R3作为虚链路的端点,同样配置区域认证。
虚链路area 0区域认证与R1和R2路由器认证方式及密码相同。
Area 2区域不做认证,R4路由器不需要配置。
以上命令即实现了ospf的认证功能。
三、配置验证配置验证也是比较简单检查相同区域内是否均配置了认证、邻居关系知否建立、是否学习到路由等。
还可以使用dis ospf brief命令,查看加密方式。
四、实验结论Ospf认证主要有两种区域认证和接口认证。
Ospf认证方式不建议采用simple(明文)方式,此方式认证密码会以明文的方式包含于ospf报文中,很不安全,推荐使用md5方式。
上图是我配置好之后做的抓包,在报文中明显能够看到认证密码为“addoil”。
而md5加密方式的密码是无法破解的。
请区分认证方式和密码显示方式是不同的概念。
一旦骨干区域(area 0)开启了区域认证,虚链路的端点设备也同样要开启area 0的区域认证,否则虚链路无法建立。