
华为交换机路由器常用命令
华为交换、路由器常见命令华为交换、路由器常见命令交换机命令~~~~~~~~~~[Quidway]discur;显示当前配置[Quidway]displaycurrent-configuration ;显示当前配置[Quidway]displayinterfaces ;显示接口信息[Quidway]display vlanall ;显示路由信息[Quidway]displayversion;显示版本信息[Quidway]superpassword;修改特权用户密码[Quidway]sysname;交换机命名[Quidway]interface ethernet0/1 ;进入接口视图[Quidway]interface vlanx ;进入接口视图[Quidway-Vlan-interfacex]ip address 10.65.1.1 255.255.0.0 ;配置VLAN的IP地址[Quidway]ip route-static 0.0.0.0 0.0.0.010.65.1.2 ;静态路由=网关[Quidway]rip;三层交换支持[Quidway]local-user ftp[Quidway]user-interface vty 04 ;进入虚拟终端[S3026-ui-vty0-4]authentication-modepassword ;设置口令模式[S3026-ui-vty0-4]set authentication-mode password simple 222 ;设置口令[S3026-ui-vty0-4]user privilege level3 ;用户级别[Quidway]interface ethernet0/1 ;进入端口模式[Quidway]inte0/1;进入端口模式[Quidway-Ethernet0/1]duplex{half|full|auto} ;配置端口工作状态[Quidway-Ethernet0/1]speed{10|100|auto} ;配置端口工作速率[Quidway-Ethernet0/1]flow-control;配置端口流控[Quidway-Ethernet0/1]mdi{across|auto|normal} ;配置端口平接扭接[Quidway-Ethernet0/1]port link-type {trunk|access|hybrid} ;设置端口工作模式[Quidway-Ethernet0/1]port access vlan3 ;当前端口加入到VLAN[Quidway-Ethernet0/2]port trunk permit vlan {ID|All} ;设trunk允许的VLAN[Quidway-Ethernet0/3]port trunk pvid vlan 3 ;设置trunk端口的PVID[Quidway-Ethernet0/1]undoshutdown ;激活端口[Quidway-Ethernet0/1]shutdown;关闭端口[Quidway-Ethernet0/1]quit;返回[Quidway]vlan3;创建VLAN[Quidway-vlan3]port ethernet 0/1 ;在VLAN中增加端口[Quidway-vlan3]porte0/1 ;简写方式[Quidway-vlan3]port ethernet 0/1 to ethernet 0/4 ;在VLAN中增加端口[Quidway-vlan3]port e0/1 toe0/4 ;简写方式[Quidway]monitor-port <interface_type interface_num> ;指定镜像端口[Quidway]port mirror <interface_type interface_num> ;指定被镜像端口[Quidway]port mirror int_list observing-port int_type int_num ;指定镜像和被镜像[Quidway]descriptionstring ;指定VLAN描述字符[Quidway]description;删除VLAN描述字符[Quidway]display vlan[vlan_id];查看VLAN设置[Quidway]stp{enable|disable};设置生成树,默认关闭[Quidway]stp priority4096 ;设置交换机的优先级[Quidway]stp root{primary|secondary} ;设置为根或根的备份[Quidway-Ethernet0/1]stp cost200 ;设置交换机端口的花费[Quidway]link-aggregation e0/1 to e0/4ingress|both ; 端口的聚合[Quidway]undo link-aggregatione0/1|all ; 始端口为通道号[SwitchA-vlanx]isolate-user-vlanenable ;设置主vlan[SwitchA]isolate-user-vlan <x> secondary <list> ;设置主vlan包括的子vlan[Quidway-Ethernet0/2]port hybrid pvid vlan <id> ;设置vlan的pvid[Quidway-Ethernet0/2]port hybridpvid ;删除vlan的pvid [Quidway-Ethernet0/2]port hybrid vlan vlan_id_list untagged ;设置无标识的vlan如果包的vlan id与PVId一致,则去掉vlan信息. 默认PVID=1。
所以设置PVID为所属vlan id, 设置可以互通的vlan为untagged.----------------------------------------路由器命令~~~~~~~~~~[Quidway]displayversion;显示版本信息[Quidway]displaycurrent-configuration ;显示当前配置[Quidway]displayinterfaces ;显示接口信息[Quidway]display iproute ;显示路由信息[Quidway]sysnameaabbcc;更改主机名[Quidway]super passwrod123456 ;设置口令[Quidway]interfaceserial0 ;进入接口[Quidway-serial0]ip address <ip> <mask|mask_len> ;配置端口IP地址[Quidway-serial0]undoshutdown ;激活端口[Quidway]link-protocolhdlc ;绑定hdlc协议[Quidway]user-interface vty 0 4[Quidway-ui-vty0-4]authentication-mode password[Quidway-ui-vty0-4]set authentication-mode password simple 222 [Quidway-ui-vty0-4]user privilege level 3[Quidway-ui-vty0-4]quit[Quidway]debugging hdlc allserial0 ;显示所有信息[Quidway]debugging hdlc eventserial0 ;调试事件信息[Quidway]debugging hdlc packetserial0 ;显示包的信息静态路由:[Quidway]ip route-static <ip><mask>{interfacenumber|nexthop}[value][reject|blackhole]例如:[Quidway]ip route-static 129.1.0.0 16 10.0.0.2[Quidway]ip route-static 129.1.0.0 255.255.0.0 10.0.0.2[Quidway]ip route-static 129.1.0.0 16 Serial 2[Quidway]ip route-static 0.0.0.0 0.0.0.0 10.0.0.2动态路由:[Quidway]rip;设置动态路由[Quidway]ripwork;设置工作允许[Quidway]ripinput;设置入口允许[Quidway]ripoutput;设置出口允许[Quidway-rip]network1.0.0.0 ;设置交换路由网络[Quidway-rip]networkall;设置与所有网络交换[Quidway-rip]peerip-address;[Quidway-rip]summary;路由聚合[Quidway]rip version1;设置工作在版本1[Quidway]rip version 2multicast ;设版本2,多播方式[Quidway-Ethernet0]ripsplit-horizon ;水平分隔[Quidway]router idA.B.C.D;配置路由器的ID[Quidway]ospfenable;启动OSPF协议[Quidway-ospf]import-routedirect ;引入直联路由[Quidway-Serial0]ospf enable area<area_id> ;配置OSPF区域标准访问列表命令格式如下:acl <acl-number> [match-orderconfig|auto] ;默认前者顺序匹配。
rule [normal|special]{permit|deny} [source source-addrsource-wildcard|any]例:[Quidway]acl 10[Quidway-acl-10]rule normal permit source 10.0.0.0 0.0.0.255 [Quidway-acl-10]rule normal deny source any扩展访问控制列表配置命令配置TCP/UDP协议的扩展访问列表:rule {normal|special}{permit|deny}{tcp|udp}source {<ipwild>|any}destination <ip wild>|any}[operate]配置ICMP协议的扩展访问列表:rule {normal|special}{permit|deny}icmp source {<ipwild>|any]destination {<ip wild>|any][icmp-code] [logging]扩展访问控制列表操作符的含义equalportnumber;等于greater-thanportnumber;大于less-thanportnumber;小于not-equalportnumber;不等range portnumber1portnumber2;区间扩展访问控制列表举例[Quidway]acl 101[Quidway-acl-101]rule deny souce any destination any[Quidway-acl-101]rule permit icmp source any destination any icmp-type echo[Quidway-acl-101]rule permit icmp source any destination any icmp-typeecho-reply[Quidway]acl 102[Quidway-acl-102]rule permit ip source 10.0.0.1 0.0.0.0 destination 202.0.0.1 0.0.0.0[Quidway-acl-102]rule deny ip source any destination any [Quidway]acl 103[Quidway-acl-103]rule permit tcp source any destination 10.0.0.1 0.0.0.0 destination-port equal ftp[Quidway-acl-103]rule permit tcp source any destination 10.0.0.2 0.0.0.0 destination-port equal www[Quidway]firewall enable[Quidway]firewall default permit|deny[Quidway]int e0[Quidway-Ethernet0]firewall packet-filter 101 inbound|outbound地址转换配置举例[Quidway]firewall enable[Quidway]firewall default permit[Quidway]acl101 ;内部指定主机可以进入e0[Quidway-acl-101]rule deny ip source any destination any[Quidway-acl-101]rule permit ip source 129.38.1.1 0 destination any [Quidway-acl-101]rule permit ip source 129.38.1.2 0 destination any [Quidway-acl-101]rule permit ip source 129.38.1.3 0 destination any [Quidway-acl-101]rule permit ip source 129.38.1.4 0 destination any [Quidway-acl-101]quit[Quidway]int e0[Quidway-Ethernet0]firewall packet-filter 101 inbound[Quidway]acl102 ;外部特定主机和大于1024端口的数据包允许进入S0[Quidway-acl-102]rule deny ip source any destination any[Quidway-acl-102]rule permit tcp source 202.39.2.3 0 destination 202.38.160.1 0[Quidway-acl-102]rule permit tcp source any destination 202.38.160.1 0 destination-port great-than1024[Quidway-acl-102]quit[Quidway]int s0[Quidway-Serial0]firewall packet-filter 102 inbound ;设202.38.160.1是路由器出口IP。
鸿鹄论坛华为交换机路由器常见命令

华为交换机、路由器常见命令路由器基本配置命令举例Quidwaysysname router_name 命名路由器或交换机Quidwaydelete 删除Flash ROM中的配置Quidwaysave 将配置写入Flash ROMQuidwayinterface serial 0 进入接口配置模式Quidwayquit 退出接口模式到系统视图Quidwayshutdown/undo shutdown 关闭/重启接口Quidwayip address ip_address subnet_mask 为接口配置IP地址和子网掩码Quidwaydisplay version 显示VRP版本号Quidwaydisplay current-configuration 显示系统运行配置信息Quidwaydisplay interfaces 显示接口配置信息Quidwaydisplay ip routing 显示路由表Quidwayping ip_address 测试网络连通性Quidwaytracert ip_address 测试数据包从主机到目的地所经过的网关Quidwaydebug all 打开所有调试信息Quidwayundo debug all 关闭所有调试信息Quidwayinfo-center enable 开启调试信息输出功能Quidwayinfo-center console dubugging 将调试信息输出到PCQuidwayinfo-center monitor dubugging 将调试信息输出到Telnet终端或哑终端交换机配置命令举例大括号{}中的选项为单选项,斜体字部分为参数值Quidwaysuper password password 修改特权模式口令Quidwaysysname switch_name 命名交换机或路Quidwayinterface ethernet 0/1 进入接口视图Quidwayquit 退出系统视图Quidway-Ethernet0/1duplex {half|full|auto} 配置接口双工工Quidway-Ethernet0/1speed {10|100|auto} 配置接口速率Quidway-Ethernet0/1flow-control 开启流控制Quidway-Ethernet0/1mdi {across|normal|auto} 配置MDI/MDIXQuidway-Ethernet0/1shutdown/undo shutdown 关闭/重启端口VLAN基本配置命令以Quidway S3026为例Quidwayvlan 3 创建并进入VLAN配置模式,缺省时系统将所有端口加入VLAN 1,这个端口既不能被创建也不能被删除;Quidwayundo vlan 3 删除一个VLANQuidway-vlan3port ethernet 0/1 to ethernet 0/4 给VLAN增加/删除以太网接口Quidway-Ethernet0/2port access vlan 3 将本接口加入到指定VLAN idQuidway-Ethernet0/2port link-type {access|trunk|hybrid} 设置端口工作方式,access缺省不支持帧的传送,而trunk支持用于Switch间互连,hybrid和trunk的区别在于trunk只允许缺省VLAN的报文发送时不打标签,而hybrid允许多个VLAN报文发送时不打标签;端口聚合配置命令Quidwaylink-aggregation ethernet 0/7 to ethernet 0/10 {ingress|both} 配置端口聚合Port_num1为端口聚合组的起始端口号,Port_num2为终止端口号ingress为接口入负荷分担方式,both为接口出负荷分担方式;STP基本配置命令Quidwaystp {enable|disable} 开启/关闭STP 功能,默认关闭,开启后所有端口都参与STP 计算;Quidway-Ethernet0/3stp disable 关闭指定接口上的STP功能,如某些网络不存在环路可以关闭STP;PPP配置命令Quidway-Serial0link-protocol ppp 封装PPP协议Quidway-Serial0ppp authentication-mode {pap|chap} 设置验证类型Quidwaylocal-user username password {simple|cipher} password 配置用户列表- PAP验证配置:主验证方Quidwaylocal-user username password {simple|cipher} password 配置用户列表Quidway-Serial0ppp authentication-mode pap被验证方Quidway-Serial0ppp pap local-user username password {simple|cipher} password- CHAP验证配置:主验证方Quidwaylocal-user username password {simple|cipher} password 配置被验证方用户列表Quidway-Serial0ppp chap host hostname 配置本地名称Quidway-Serial0ppp authentication-mode chap被验证方Quidwaylocal-user username password {simple|cipher} password 配置主验证方用户列表Quidway-Serial0ppp chap user username 配置本地名称MP配置命令Quidway-Serial0ppp mp 封装MP协议Quidwayppp mp user username bind virtual-template number 建立用户与虚拟模板的对应关系Quidwayinterface virtual-template number 配置虚拟接口模板Quidwayppp mp max-bind number 设置虚拟模板最大绑定数1-100帧中继配置命令Quidway-Serial0link-protocol fr {mfr|ietf|nonstandard} 封装帧中继协议:IETF、Cisco兼容Quidway-Serial0fr interface-type {dte|dce|nni} 配置帧中继接口类型,NNI为帧中继交换机之间的接口;若配为DCE或NNI,则须先使能fr switching;Quidway-Serial0fr lmi type {q933a|ansi|cisco-compatible} 配置LMI协议类型Quidway-Serial0fr dlci dlci_number 配置一条本地虚电路号Quidway-Serial0fr map {ip|ipx} protocol-address dlci dlci_number 建立本地DLCI到对端协议地址的映射Quidway-Serial0fr inarp ip|ipx dlci_number 配置Inverse ARP动态映射Quidwayinterface type 创建并进入子接口配置模式RIP协议配置命令Quidwaydisplay rip 显示RIP配置信息Quidwayrip 启动并进入RIP配置模式Quidway-ripnetwork {network_number|all} 在指定网络上使能RIPQuidway-rippeer ip_address 配置报文的定点传送Quidway-Ethernet0rip version {1|2 bcast|mcast} 指定RIP版本及传送方式Quidway-Serial0rip work 指定接口工作状态同rip input,rip outputQuidway-ripauto-summary 配置RIP-2路由聚合Quidway-Serial0rip authentication simple password 配置RIP-2明文认证密码Quidway-Serial0rip authentication md5 key-string string 配置RIP-2 MD5密文认证密码串Quidway-Serial0rip authentication md5 type {nonstandard-compatible|usual} 指定MD5类型Quidwaydebugging rip packet 打开RIP调试开关Quidwayinfo-center console 将调试信息输出到PC静态路由配置命令Quidwayip route ip_address subnet_mask {interface_name|gateway_address} preference preference_value reject|black_bone命令说明reject:任何去往该目的地的报文均被丢弃,通知源主机不可达;black_bone:任何去往该目的地的报文均被丢弃,不通知源主机;当只有下一跳的接口是PPP或HDLC接口才能写interface_name,如Serial0,否则只能写gateway_address下一跳地址;命令举例Quidwayip route 16 10.0.0.2Quidwayip routeQuidwayip route 16 Serial2Quidwayip route 配置缺省路由;OSPF配置命令Quidwayrouter id ip_address 配置Router IDQuidwayospf enable 启用OSPF协议Quidway-Serial0ospf enable area area_id 配置当前接口所属的OSPF区域。
华为路由器命令

华为华为路由器交换机配置命令大全一、计算机命令PCAlogin:root 使用root用户password:linux 口令是linux#shutdown-hnow 关机#init 0 关机#logout 用户注销#login 用户登录#ifconfig 显示IP地址# ifconfig eth0 <ip address> netmask掩码<netmask> 设置IP地址# ifconfig eht0 <ip address> netmask <netmask> down 禁用IP地址# route add 0.0.0.0 gw <ip> 设置网关# route del 0.0.0.0 gw <ip> 删除网关# route add default gw <ip> 设置网关# route del default gw <ip> 删除网关# route 显示网关# ping <ip> 发ECHO包# telnet <ip> 远程登录二、华为路由器交换机配置命令:交换机命令[Quidway]dis cur;显示当前配置[Quidway]display current-configuration;显示当前配置[Quidway]display interfaces;显示接口信息[Quidway]display vlan;显示vlan信息[Quidway]display version;显示版本信息[Quidway]super password;修改特权用户密码[Quidway]sysname;交换机命名[Quidway]interface ethernet0/1;进入接口视图[Quidway]interface vlan x;进入接口视图[Quidway-Vlan-interfacex]ip address 10.65.1.1 255.255.0.0;配置VLAN的IP地址[Quidway]Ip route-static 0.0.0.0 0.0.0.0 10.65.1.2;静态路由=网关[Quidway]rip;rip协议[Quidway]local-user ftp[Quidway]user-interface vty 0 4;进入虚拟终端[S3026-ui-vty0-4]authentication-mode password;设置口令模式[S3026-ui-vty0-4]set authentication-mode password simple 222;设置口令[S3026-ui-vty0-4]user privilege level 3;用户级别[Quidway]interface ethernet0/1;进入端口模式[Quidway]int e0/1;进入端口模式[Quidway-Ethernet0/1]duplex{half|full|auto};配置端口工作状态[Quidway-Ethernet0/1]speed{10|100|auto};配置端口工作速率[Quidway-Ethernet0/1]flow-control;配置端口流控[Quidway-Ethernet0/1]mdi{across|auto|normal};配置端口平接扭接[Quidway-Ethernet0/1]portlink-type{trunk|access|hybrid};设置端口工作模式[Quidway-Ethernet0/1]port access vlan 3;当前端口加入到VLAN[Quidway-Ethernet0/2]port trunk permit vlan{ID|All};设trunk允许的VLAN [Quidway-Ethernet0/3]port trunk pvid vlan 3;设置trunk端口的PVID[Quidway-Ethernet0/1]undo shutdown;激活端口[Quidway-Ethernet0/1]shutdown;关闭端口[Quidway-Ethernet0/1]quit;返回[Quidway]vlan3;创建VLAN[Quidway-vlan3]port ethernet0/1;在VLAN中增加端口[Quidway-vlan3]port e0/1;简写方式[Quidway-vlan3]port ethernet0/1 to ethernet0/4;在VLAN中增加端口[Quidway-vlan3]port e0/1 to e0/4;简写方式[Quidway]monitor-port;指定镜像端口[Quidway]port mirror;指定被镜像端口[Quidway]port mirror int_list observing-port int_type int_num;指定镜像和被镜像[Quidway]description string;指定VLAN描述字符[Quidway]description;删除VLAN描述字符[Quidway]display vlan[vlan_id];查看VLAN设置[Quidway]stp{enable|disable};设置生成树,默认关闭[Quidway]stp priority 4096;设置交换机的优先级[Quidway]stp root{primary|secondary};设置为根或根的备份[Quidway-Ethernet0/1]stp cost 200;设置交换机端口的花费[Quidway]link-aggregation e0/1 to e0/4 ingress|both;端口的聚合[Quidway]undo link-aggregation e0/1|all;始端口为通道号[SwitchA-vlanx]isolate-user-vlan enable;设置主vlan[SwitchA]isolate-user-vlan secondary;设置主vlan包括的子vlan[Quidway-Ethernet0/2]port hybrid pvid vlan;设置vlan的pvid[Quidway-Ethernet0/2]port hybrid pvid;删除vlan的pvid[Quidway-Ethernet0/2]port hybrid vlan vlan_id_list untagged;设置无标识的vlan 如果包的vlanid与PVId一致,则去掉vlan信息.默认PVID=1。
华为路由器交换机配置命令大全

华为路由器交换机配置命令大全华为路由器交换机配置大全本文提供XXX路由器交换机的配置命令,包括计算机命令和交换机命令。
一、计算机命令以下是一些常用的计算机命令:shutdown-hnow;关机init 0;关机logout;用户注销login;用户登录ifconfig;显示IP地址ifconfig eth0 netmask;设置IP地址ifconfig eht0 netmask down;禁用IP地址route add 0.0.0.0 gw;设置网关route del 0.0.0.0 gw;删除网关route add default gw;设置网关route del default gw;删除网关route;显示网关ping;发ECHO包;远程登录二、XXX路由器交换机配置命令以下是一些常用的XXX路由器交换机配置命令:Quidway]dis cur;显示当前配置Quidway]display n;显示当前配置Quidway]display interfaces;显示接口信息Quidway]display vlan;显示vlan信息Quidway]display n;显示版本信息Quidway]super password;修改特权用户密码Quidway]sysname;交换机命名Quidway]XXX;进入接口视图Quidway]interface vlan x;进入接口视图Quidway-Vlan-interface x]ip address 10.65.1.1 255.255.0.0;配置VLAN的IP地址Quidway]Ip route-static 0.0.0.0 0.0.0.0 10.65.1.2;静态路由=网关Quidway]rip;rip协议Quidway]local-user ftpQuidway]user-interface vty 0 4;进入虚拟终端S3026-ui-vty0-4]n-mode password;设置口令模式首先,这篇文章需要进行重新排版和编辑,以便更清晰地传达信息。
华为路由器交换机常用命令

华为路由器交换机常用命令一、设备管理命令1.登录管理命令- ssh [ip地质] -p [端口号]:通过SSH协议登录设备。
- telnet [ip地质]:通过Telnet协议登录设备。
- logout:退出设备。
2.用户管理命令- display current-configuration:显示当前设备配置信息。
- save:保存当前配置。
- undo save:取消保存的配置。
- super:切换到超级用户模式。
- user-interface console 0:配置控制台终端的参数。
- user-interface vty 0 4:配置远程登录终端的参数。
3.设备操作命令- reboot:重启设备。
- reset saved-configuration:恢复出厂配置。
- display version:显示设备的硬件和软件版本信息。
- display device:显示设备的基本信息。
- display interface[接口名称]:显示指定接口信息。
- display ip routing-table:显示IP路由表信息。
二、网络配置命令1.IP配置命令- interface [接口名称]:进入指定接口。
- ip address [IP地质] [子网掩码]:配置接口IP地质。
- undo ip address:取消接口IP地质配置。
- ip route-static [目标网络] [子网掩码] [下一跳地质]:配置静态路由。
- undo ip route-static [目标网络] [子网掩码] [下一跳地质]:取消静态路由配置。
2.VLAN配置命令- vlan [VLAN ID]:创建指定VLAN。
- quit:退出VLAN配置模式。
- interface vlan [VLAN ID]:进入指定VLAN接口。
- ip address [IP地质] [子网掩码]:为VLAN接口配置IP地质。
华三华为交换机路由器配置常用命令汇总
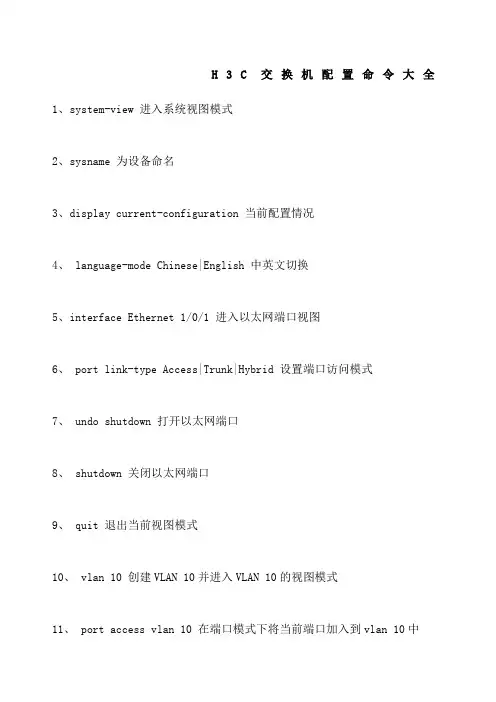
H3C交换机配置命令大全1、system-view 进入系统视图模式2、sysname 为设备命名3、display current-configuration 当前配置情况4、 language-mode Chinese|English 中英文切换5、interface Ethernet 1/0/1 进入以太网端口视图6、 port link-type Access|Trunk|Hybrid 设置端口访问模式7、 undo shutdown 打开以太网端口8、 shutdown 关闭以太网端口9、 quit 退出当前视图模式10、 vlan 10 创建VLAN 10并进入VLAN 10的视图模式11、 port access vlan 10 在端口模式下将当前端口加入到vlan 10中12、port E1/0/2 to E1/0/5 在VLAN模式下将指定端口加入到当前vlan中13、port trunk permit vlan all 允许所有的vlan通过H3C路由器配置命令大全华为交换机常用配置实例H3C交换机路由器telnet和console口登录配置2009年11月09日星期一 10:00级别说明Level 名称命令0参观ping、tracert、telnet1监控display、debugging2配置所有配置命令管理级的命令除外3管理文件系统命令、FTP命令、TFTP命令、XMODEM命令telnet仅用密码登录,管理员权限Routeruser-interface vty 0 4Router-ui-vty0-4user privilege level3Router-ui-vty0-4set authentication password simple abctelnet仅用密码登录,非管理员权限Routersuper password level 3 simplesuperRouteruser-interface vty 0 4Router-ui-vty0-4user privilege level1Router-ui-vty0-4set authentication password simple abctelnet使用路由器上配置的用户名密码登录,管理员权限Routerlocal-user admin passwordsimple adminRouterlocal-user admin service-type telnetRouterlocal-useradmin level 3Routeruser-interface vty 04Router-ui-vty0-4authentication-mode localtelnet使用路由器上配置的用户名密码登录,非管理员权限Routersuper password level 3 simple superRouterlocal-user manage password simple manageRouterlocal-usermanage service-type telnetRouterlocal-user manage level2Routeruser-interface vty 0 4Router-ui-vty0-4authentication-mode local对console口设置密码,登录后使用管理员权限Routeruser-interface con0Router-ui-console0user privilege level 3Router-ui-console0set authentication password simple abc对console口设置密码,登录后使用非管理员权限Routersuper password level 3 simple superRouteruser-interfacecon 0Router-ui-console0user privilege level 1Router-ui-console0set authentication password simple abc对console口设置用户名和密码,登录后使用管理员权限Routerlocal-user admin password simpleadminRouterlocal-user admin service-type terminalRouterlocal-user adminlevel 3Routeruser-interface con 0Router-ui-console0authentication-modelocal对console口设置用户名和密码,登录后使用非管理员权限Routersuper password level 3 simple superRouterlocal-user manage password simple manageRouterlocal-user manage service-type terminalRouterlocal-usermanage level 2Routeruser-interface con0Router-ui-console0authentication-mode localsimple 是明文显示,cipher 是加密显示路由器不设置telnet登录配置时,用户无法通过telnet登录到路由器上Router-ui-vty0-4acl 2000 inbound可以通过acl的规则只允许符合条件的用户远程登录路由器华为路由器ospfnat。
华为路由器和交换机的常用命令
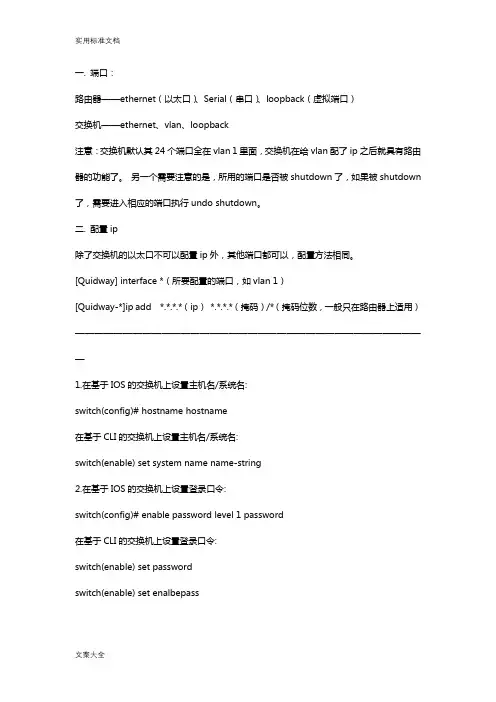
一. 端口:路由器——ethernet(以太口)、Serial(串口)、loopback(虚拟端口)交换机——ethernet、vlan、loopback注意:交换机默认其24个端口全在vlan 1里面,交换机在给vlan配了ip之后就具有路由器的功能了。
另一个需要注意的是,所用的端口是否被shutdown了,如果被shutdown 了,需要进入相应的端口执行undo shutdown。
二. 配置ip除了交换机的以太口不可以配置ip外,其他端口都可以,配置方法相同。
[Quidway] interface *(所要配置的端口,如vlan 1)[Quidway-*]ip add *.*.*.*(ip)*.*.*.*(掩码)/*(掩码位数,一般只在路由器上适用)—————————————————————————————————————1.在基于IOS的交换机上设置主机名/系统名:switch(config)# hostname hostname在基于CLI的交换机上设置主机名/系统名:switch(enable) set system name name-string2.在基于IOS的交换机上设置登录口令:switch(config)# enable password level 1 password在基于CLI的交换机上设置登录口令:switch(enable) set passwordswitch(enable) set enalbepass3.在基于IOS的交换机上设置远程访问:switch(config)# interface vlan 1switch(config-if)# ip address ip-address netmaskswitch(config-if)# ip default-gateway ip-address在基于CLI的交换机上设置远程访问:switch(enable) set interface sc0 ip-address netmask broadcast-addressswitch(enable) set interface sc0 vlanswitch(enable) set ip route default gateway4.在基于IOS的交换机上启用和浏览CDP信息:switch(config-if)# cdp enableswitch(config-if)# no cdp enable为了查看Cisco邻接设备的CDP通告信息:switch# show cdp interface [type modle/port]switch# show cdp neighbors [type module/port] [detail]在基于CLI的交换机上启用和浏览CDP信息:switch(enable) set cdp {enable|disable} module/port为了查看Cisco邻接设备的CDP通告信息:switch(enable) show cdp neighbors[module/port] [vlan|duplex|capabilities|detail]5.基于IOS的交换机的端口描述:switch(config-if)# description description-string基于CLI的交换机的端口描述:switch(enable)set port name module/number description-string6.在基于IOS的交换机上设置端口速度:switch(config-if)# speed{10|100|auto}在基于CLI的交换机上设置端口速度:switch(enable) set port speed moudle/number {10|100|auto} switch(enable) set port speed moudle/number {4|16|auto}7.在基于IOS的交换机上设置以太网的链路模式:switch(config-if)# duplex {auto|full|half}在基于CLI的交换机上设置以太网的链路模式:switch(enable) set port duplex module/number {full|half}8.在基于IOS的交换机上配置静态VLAN:switch# vlan databaseswitch(vlan)# vlan vlan-num name vlaswitch(vlan)# exitswitch# configure teriminalswitch(config)# interface interface module/numberswitch(config-if)# switchport mode accessswitch(config-if)# switchport access vlan vlan-numswitch(config-if)# end在基于CLI的交换机上配置静态VLAN:switch(enable) set vlan vlan-num [name name]switch(enable) set vlan vlan-num mod-num/port-list9. 在基于IOS的交换机上配置VLAN中继线:switch(config)# interface interface mod/portswitch(config-if)# switchport mode trunkswitch(config-if)# switchport trunk encapsulation {isl|dotlq}switch(config-if)# switchport trunk allowed vlan remove vlan-list switch(config-if)# switchport trunk allowed vlan add vlan-list在基于CLI的交换机上配置VLAN中继线:switch(enable) set trunk module/port [on|off|desirable|auto|nonegotiate] Vlan-range [isl|dotlq|dotl0|lane|negotiate]10.在基于IOS的交换机上配置VTP管理域:switch# vlan databaseswitch(vlan)# vtp domain domain-name在基于CLI的交换机上配置VTP管理域:switch(enable) set vtp [domain domain-name]11.在基于IOS的交换机上配置VTP 模式:switch# vlan databaseswitch(vlan)# vtp domain domain-nameswitch(vlan)# vtp {sever|cilent|transparent}switch(vlan)# vtp password password在基于CLI的交换机上配置VTP 模式:switch(enable) set vtp [domain domain-name] [mode{ sever|cilent|transparent }][password password]12. 在基于IOS的交换机上配置VTP版本:switch# vlan databaseswitch(vlan)# vtp v2-mode在基于CLI的交换机上配置VTP版本:switch(enable) set vtp v2 enable13. 在基于IOS的交换机上启动VTP剪裁:switch# vlan databaseswitch(vlan)# vtp pruning在基于CL I 的交换机上启动VTP剪裁:switch(enable) set vtp pruning enable14.在基于IOS的交换机上配置以太信道:switch(config-if)# port group group-number [distribution {source|destination}] 在基于CLI的交换机上配置以太信道:switch(enable) set port channel moudle/port-range mode{on|off|desirable|auto}15.在基于IOS的交换机上调整根路径成本:switch(config-if)# spanning-tree [vlan vlan-list] cost cost在基于CLI的交换机上调整根路径成本:switch(enable) set spantree portcost moudle/port costswitch(enable) set spantree portvlancost moudle/port [cost cost][vlan-list] 16.在基于IOS的交换机上调整端口ID:switch(config-if)# spanning-tree[vlan vlan-list]port-priority port-priority在基于CLI的交换机上调整端口ID:switch(enable) set spantree portpri {mldule/port}priorityswitch(enable) set spantree portvlanpri {module/port}priority [vlans]17. 在基于IOS的交换机上修改STP时钟:switch(config)# spanning-tree [vlan vlan-list] hello-time secondsswitch(config)# spanning-tree [vlan vlan-list] forward-time seconds` switch(config)# spanning-tree [vlan vlan-list] max-age seconds在基于CLI的交换机上修改STP时钟:switch(enable) set spantree hello interval[vlan]switch(enable) set spantree fwddelay delay [vlan]switch(enable) set spantree maxage agingtiame[vlan]18. 在基于IOS的交换机端口上启用或禁用Port Fast 特征:switch(config-if)#spanning-tree portfast在基于CLI的交换机端口上启用或禁用Port Fast 特征:switch(enable) set spantree portfast {module/port}{enable|disable}19. 在基于IOS的交换机端口上启用或禁用UplinkFast 特征:switch(config)# spanning-tree uplinkfast [max-update-rate pkts-per-second]在基于CLI的交换机端口上启用或禁用UplinkFast 特征:switch(enable) set spantree uplinkfast {enable|disable}[rate update-rate] [all-protocols off|on]20. 为了将交换机配置成一个集群的命令交换机,首先要给管理接口分配一个IP地址,然后使用下列命令: switch(config)# cluster enable cluster-name21. 为了从一条中继链路上删除VLAN,可使用下列命令:switch(enable) clear trunk module/port vlan-range22. 用show vtp domain 显示管理域的VTP参数.23. 用show vtp statistics显示管理域的VTP参数.24. 在Catalyst交换机上定义TrBRF的命令如下:switch(enable) set vlan vlan-name [name name] type trbrf bridge bridge-num[stp {ieee|ibm}]25. 在Catalyst交换机上定义TrCRF的命令如下:switch (enable) set vlan vlan-num [name name] type trcrf{ring hex-ring-num|decring decimal-ring-num} parent vlan-num26. 在创建好TrBRF VLAN之后,就可以给它分配交换机端口.对于以太网交换,可以采用如下命令给VLAN分配端口:switch(enable) set vlan vlan-num mod-num/port-num27. 命令show spantree显示一个交换机端口的STP状态.28. 配置一个ELAN的LES和BUS,可以使用下列命令:ATM (config)# interface atm number.subint multiointATM(config-subif)# lane serber-bus ethernet elan-name29. 配置LECS:ATM(config)# lane database database-nameATM(lane-config-databade)# name elan1-name server-atm-address les1-nsap-addressATM(lane-config-databade)# name elan2-name server-atm-address les2-nsap-addressATM(lane-config-databade)# name …30. 创建完数据库后,必须在主接口上启动LECS.命令如下:ATM(config)# interface atm numberATM(config-if)# lane config database database-nameATM(config-if)# lane config auto-config-atm-address31. 将每个LEC配置到一个不同的ATM子接口上.命令如下:ATM(config)# interface atm number.subint multipointATM(config)# lane client ethernet vlan-num elan-num32. 用show lane server 显示LES的状态.33. 用show lane bus显示bus的状态.34. 用show lane database显示LECS数据库可容.35. 用show lane client显示LEC的状态.36. 用show module显示已安装的模块列表.37. 用物理接口建立与VLAN的连接:router# configure terminalrouter(config)# interface media module/portrouter(config-if)# description description-stringrouter(config-if)# ip address ip-addr subnet-maskrouter(config-if)# no shutdown38. 用中继链路来建立与VLAN的连接:router(config)# interface module/port.subinterfacerouter(config-ig)# encapsulation[isl|dotlq] vlan-numberrouter(config-if)# ip address ip-address subnet-mask39. 用LANE 来建立与VLAN的连接:router(config)# interface atm module/portrouter(config-if)# no ip addressrouter(config-if)# atm pvc 1 0 5 qsaalrouter(config-if)# atm pvc 2 0 16 ilnirouter(config-if)# interface atm module/port.subinterface multipoint router(config-if)# ip address ip-address subnet-maskrouter(config-if)# lane client ethernet elan-numrouter(config-if)# interface atm module/port.subinterface multipointrouter(config-if)# ip address ip-address subnet-namerouter(config-if)# lane client ethernet elan-namerouter(config-if)# …40. 为了在路由处理器上进行动态路由配置,可以用下列IOS命令来进行: router(config)# ip routingrouter(config)# router ip-routing-protocolrouter(config-router)# network ip-network-numberrouter(config-router)# network ip-network-number41. 配置默认路由:switch(enable) set ip route default gateway42. 为一个路由处理器分配VLANID,可在接口模式下使用下列命令: router(config)# interface interface numberrouter(config-if)# mls rp vlan-id vlan-id-num43. 在路由处理器启用MLSP:router(config)# mls rp ip44. 为了把一个外置的路由处理器接口和交换机安置在同一个VTP域中: router(config)# interface interface numberrouter(config-if)# mls rp vtp-domain domain-name45. 查看指定的VTP域的信息:router# show mls rp vtp-domain vtp domain name46. 要确定RSM或路由器上的管理接口,可以在接口模式下输入下列命令:router(config-if)#mls rp management-interface47. 要检验MLS-RP的配置情况:router# show mls rp48. 检验特定接口上的MLS配置:router# show mls rp interface interface number49. 为了在MLS-SE上设置流掩码而又不想在任一个路由处理器接口上设置访问列表:set mls flow [destination|destination-source|full]50. 为使MLS和输入访问列表可以兼容,可以在全局模式下使用下列命令:router(config)# mls rp ip input-acl51. 当某个交换机的第3层交换失效时,可在交换机的特权模式下输入下列命令:switch(enable) set mls enable52. 若想改变老化时间的值,可在特权模式下输入以下命令:switch(enable) set mls agingtime agingtime53. 设置快速老化:switch(enable) set mls agingtime fast fastagingtime pkt_threshold54. 确定那些MLS-RP和MLS-SE参与了MLS,可先显示交换机引用列表中的容再确定:switch(enable) show mls include55. 显示MLS高速缓存记录:switch(enable) show mls entry56. 用命令show in arp显示ARP高速缓存区的容。
思科华为全系列交换机路由器常用命令
思科华为全系列交换机路由器常用命令交换机/路由器配置综合复习交换机/路由器常用命令汇总本课内容交换机常用命令2交换机常用命令交换机常用命令31.交换机常用命令·>Enable进入特权模式·#E某it返回上一级操作模式·#End返回到特权模式·#writememory或copyrunning-configtartup-config保存配置文件·#delflah:config.te某t删除配置文件(交换机及1700系列路由器)·#delflah:vlan.dat删除Vlan配置信息(交换机)·(config)#hotnamewitchA配置设备名称4为witchA1.交换机常用命令·(config)#enableecretlevel10tar配置远程登陆密码为tar·(config)#enableecretlevel150tar配置特权密码为tar·Level1为普通用户级别,可选为1~15,15为最高权限级别;0表示密码不加密·(config)#enableerviceweb-erver开启交换机WEB管理功能·Service可选以下:web-erver(WEB管理)、telnet-erver(远程登陆)等51.交换机常用命令查看信息·#howrunning-config查看当前生效的配置信息·#howinterfacefatethernet0/3查看F0/3端口信息·#howinterfaceerial1/2查看S1/2端口信息·#howinterface查看所有端口信息·#howipinterfacebrief以简洁方式汇总查看所有端口信息·#howipinterface查看所有端口信息·#howverion查看版本信息61.交换机常用命令查看信息·#howmac-addre-table查看交换机当前MAC地址表信息·#howrunning-config查看当前生效的配置信息·#howvlan查看所有VLAN信息·#howvlanid10查看某一VLAN(如VLAN10)的信息·#howinterfacefatethernet0/1witchport查看某一端口模式(如F0/1)·#howaggregateport1ummary查看聚合端7口AG1的信息1.交换机常用命令查看信息·#howpanning-tree查看生成树配置信息·#howpanning-treeinterfacefatethernet0/1查看该端口的生成树状态·#howport-ecurity查看交换机的端口安全配置信息·#howport-ecurityaddre查看地址安全绑定配置信息·#howipacce-litlitname查看名为litname的列表的配置信息8·#howacce-lit1.交换机常用命令端口的基本配置·(config)#Interfacefatethernet0/3进入F0/3的端口配置模式·(config)#interfacerangefa0/1-2,0/5,0/7-9进入F0/1、F0/2、F0/5、F0/7、F0/8、F0/9的端口配置模式·(config-if)#peed10配置端口速率为10M,可选10,100,auto91.交换机常用命令端口的基本配置·(config-if)#duple某full配置端口为全双工模式,可选full(全双工),half(半双式),auto(自适应)·(config-if)#nohutdown开启该端口·(config-if)#witchportaccevlan10将该端口划入VLAN10中,用于VLAN·(config-if)#witchportmodetrunk将该端口设为trunk模式,可选模式为acce,trunk·(config-if)#port-group1将该端口划入聚合端口AG1中,用于聚合端口101.交换机常用命令聚合端口的创建·(config)#interfaceaggregateport1创建聚合接口AG1·(config-if)#witchportmodetrunk配置并保证AG1为trunk模式·(config)#intf0/23-24·(config-if-range)#port-group1将端口(端口组)划入聚合端口AG1中111.交换机常用命令生成树·(config)#panning-tree开启生成树协议·(config)#panning-treemodetp指定生成树类型为tp可选模式tp,rtp,mtp·(config)#panning-treepriority4096设置交换机的优先级为4096,优先级值小为高。
华三华为交换机-路由器配置常用命令
H3C交换机配置命令大全1、system-view 进入系统视图模式2、sysname 为设备命名3、display current-configuration 当前配置情况4、 language-mode Chinese|English 中英文切换5、interface Ethernet 1/0/1 进入以太网端口视图6、 port link-type Access|Trunk|Hybrid 设置端口访问模式7、 undo shutdown 打开以太网端口8、 shutdown 关闭以太网端口9、 quit 退出当前视图模式10、 vlan 10 创建VLAN 10并进入VLAN 10的视图模式11、 port access vlan 10 在端口模式下将当前端口加入到vlan 10中12、port E1/0/2 to E1/0/5 在VLAN模式下将指定端口加入到当前vlan中13、port trunk permit vlan all 允许所有的vlan通过H3C路由器配置命令大全1、system-view 进入系统视图模式2、sysname R1 为设备命名为R13、display ip routing-table 显示当前路由表4、 language-mode Chinese|English 中英文切换5、interface Ethernet 0/0 进入以太网端口视图6、 ip address 192.168.1.1 255.255.255.0 配置IP地址和子网掩码7、 undo shutdown 打开以太网端口8、 shutdown 关闭以太网端口9、 quit 退出当前视图模式10、 ip route-static 192.168.2.0 255.255.255.0 192.168.12.2 description To.R2 配置静态路由11、 ip route-static 0.0.0.0 0.0.0.0 192.168.12.2 description To.R2 配置默认的路由H3C S3100 SwitchH3C S3600 SwitchH3C MSR 20-20 Router1、调整超级终端的显示字号;2、捕获超级终端操作命令行,以备日后查对;3、 language-mode Chinese|English 中英文切换;4、复制命令到超级终端命令行,粘贴到主机;5、交换机清除配置 :<H3C>reset save ;<H3C>reboot ;6、路由器、交换机配置时不能掉电,连通测试前一定要检查网络的连通性,不要犯最低级的错误。
华为路由交换设备常用命令
华为路由交换机设备常用命令一.系统基本配置命令display clock命令用来查看系统当前日期和时钟。
display diagnostic-information命令用来查看系统当前诊断信息。
display history-command命令用来查看当前终端上保存的历史命令。
缺省情况下,显示最近10条历史命令。
display this命令用来查看系统当前视图的运行配置。
display version命令用来查看系统版本信息。
header命令用来设置用户登录设备时终端上显示的标题信息。
language-mode命令用来切换命令行接口的语言模式。
缺省情况下,命令行接口的语言模式为英文模式。
quit命令用来从当前视图退回到较低级别视图,如果是用户视图,则退出系统。
return命令用来从除用户视图外的其它视图退回到用户视图。
sysname命令用来设置路由器的主机名。
使用实例# 设置路由器的主机名为HUAWEIA。
<HUAWEI> system-view[HUAWEI] sysname HUAWEIAsystem-view命令用来使用户从用户视图进入系统视图。
user-interface命令用来进入一个用户界面视图或多个用户界面视图。
user-interface maximum-vty命令用来设置登录用户的最大数目。
使用实例# 配置VTY用户界面最大数目为7个。
<HUAWEI> system-view[HUAWEI] user-interface maximum-vty 7authentication-mode命令用来设置登录用户界面的验证方式。
# 使能本地密码验证。
<HUAWEI> system-view[HUAWEI] user-interface vty 0[HUAWEI-ui-vty0] authentication-mode passworddisplay user-interface命令用来查看用户界面信息。
华为路由器交换机配置命令大全
华为路由器交换机配置命令大全华为路由器交换机配置命令大全一、登录与认证命令1.Telnet 登录命令2.SSH 登录命令3.Console 登录命令4.用户认证命令二、设备管理命令1.设备信息查看命令2.设备参数配置命令3.设备重启命令4.设备保存配置命令三、接口配置命令1.查看接口状态命令2.配置接口描述命令3.配置接口IP地质命令4.配置接口MTU命令5.开启/关闭接口命令四、路由配置命令1.配置静态路由命令2.配置默认路由命令3.配置动态路由命令4.查看路由表命令5.清空路由表命令五、VLAN 配置命令1.配置VLAN命令2.配置端口VLAN命令3.配置VLAN接口命令六、交换机功能配置命令1.配置端口镜像命令2.配置链路聚合命令3.配置交换机端口安全命令4.配置交换机QoS命令七、安全配置命令1.配置访问控制列表命令2.配置NAT命令3.配置防火墙命令4.配置SSL VPN命令附录:附件:1.示例配置文件2.常见问题解答法律名词及注释:1.Telnet:一种远程登录协议,用于远程连接路由器或交换机进行管理和配置。
2.SSH:Secure Shell,一种用于远程登录的网络协议,提供安全的数据通信和用户认证方式。
3.Console:一种通过串口连接设备进行本地登录的方式。
4.VLAN:Virtual Local Area Network,虚拟局域网,将不同的物理分组划分到不同的逻辑分组中,实现逻辑分离。
5.MTU:Maximum Transmission Unit,最大传输单元,指数据链路层上一次发送的帧的最大长度。
6.NAT:Network Address Translation,网络地质转换,用于在私有网络和公共网络之间进行通信的转换技术。
7.QoS:Quality of Service,服务质量,用于在网络通信中对不同数据流进行优先级和带宽控制。