
实验三交换机基本配置及交换机端口配置报告
实验三 交换机基本配置及交换机端口配置(3学时)一、 实验目的:1. 熟悉并掌握交换机的命令行视图。
2. 要求熟练掌握交换机的基本配置方法,能完成日常管理网络或配置网络中有关交换机端口的常用配置,并逐步熟悉交换机端口的基本信息。
3. 掌握用console 端口配置交换机的方法。
4. 掌握在交换机端口视图下对交换机的端口的各参数进行配置和管理。
二、 实验设备:1. 交换机2. 计算机、网卡3. 网线4. 串口线三、 实验内容及实验步骤: (一) 交换机的初步认识Quidway S3526 以太网交换机是华为公司推出的盒式L2/L3 层线速以太网交换产品。
图1 Quidway S3526交换机外观图2 S3526 交换机交流机箱后面板示意图图3 S3526 交换机直流机箱后面板示意图表1 S3526 交换机前面板指示灯表2 配置口(Console)属性(二) 交换机的电缆连接(通过Console 口搭建本地配置环境)【备注】:交换机的配置环境可通过Console 口搭建本地配置环境、通过Telnet 搭建配置环境、通过Modem 拨号搭建配置环境(参见S3500操作手册1入门操作.PDF 文档说明,本实验主要通过Console 口搭建本地配置环境)需要连接3根线:①电源线;② 网线;③配置电缆。
如图连接方式:(三) 交换机的启动①电源线连接到插座连接到交换机电源插口1.点击“开始”-“程序”-“附件”-“通讯”-“超级终端”进行交换机的连接与串口参数设置:图5 超级终端连接说明界面图6 超级终端连接使用串口设置图7 串口参数设置2.在出现“Press Ctrl-B to enter Boot Menu...”的5 秒钟之内,键入<Ctrl+B>,系统方能进入BOOT 菜单,否则系统将进入程序解压过程;若程序进入解压过程后再希望进入BOOT 菜单,则需要重新启动交换机。
(四) 交换机的基本配置【备注】:以下各命令的使用请参考S3500操作手册入门、S3500命令手册1入门命令、S3500命令手册2端口命令等PDF文档。
视图介绍(参见S3500操作手册1入门操作.PDF文档说明)图9 命令视图功能特性列表基本配置过程:1、进入命令行用户视图<Quidway>,输入?取得在线帮助<Quidway>?2、删除Flash中的配置信息<Quidway> reset saved-configuration<Quidway> reboot<Quidway>reset saved-configuration交换机的 flash memory 中的配置将被擦除.你确信吗?[Y/N]y开始擦除 flash memory 中的配置.请稍侯......擦除配置成功.<Quidway>reboot确实要重启交换机吗? [Y/N] y%2011/12/29 11:32:50 Quidway DEV/5/DEV_LOG: Switch is rebooted.<Quidway>starting......****************************************** * * * Quidway S3526 BOOTROM, Version 3.5 * * ******************************************Copyright(C) 2000-2002 by HUAWEI TECHNOLOGIES CO.,LTD.Creation date: Jul 15 2002, 11:44:35 CPU type : MPC8240CPU Clock Speed : 200MhzBUS Clock Speed : 33MhzMemory Size : 64MBS3526R001 main board self testing...........................SDRAM fast selftest......................................OK!Please check port leds................Led selftest finished!Flash fast selftest......................................OK!Switch chip selftest.....................................OK!CPLD selftest............................................OK!Port g2/1 has no modulePort g1/1 has no modulePHY selftest.............................................OK!SSRAM fast selftest......................................OK!Press Ctrl-B to enter Boot Menu 0Auto-booting...Decompress Image................................................................................................................................. ................................................................................ ................................................................................ ...............................OK!Starting application now...User interface Aux0/0 is availablePress ENTER to get started.3、设置语言环境<Quidway> language-mode Chinese<Quidway> language-mode ?chinese Chinese environmentenglish English environment<Quidway> language-mode ChineseChange language mode, confirm? [Y/N]y % 改变到中文模式。
<Quidway>?监控视图命令:boot 设置启动选项cd 改变当前路径clock 设置系统时钟cluster 执行集群命令copy 拷贝文件debugging 打开系统调试开关delete 删除文件dir 显示系统中的文件列表display 显示当前系统信息format 格式化设备free 释放用户接口ftp 建立一个FTP连接language-mode 设置语言环境lock 锁住用户终端mkdir 创建新目录more 显示文件的内容move 移动文件ni NI调试信息ntdp 运行NTDP命令ping 检查网络连接或主机是否可达pwd 显示当前路径quit 退出当前的命令视图---- More ----<Quidway> language-mode english4、查看交换机的基本信息,检查运行状态;<Quidway>display current-configurationsysname Quidway#radius scheme systemserver-type huaweiprimary authentication 127.0.0.1 1645primary accounting 127.0.0.1 1646user-name-format without-domaindomain systemradius-scheme systemaccess-limit disablestate activeidle-cut disableself-service-url disablemessenger time disabledomain default enable system#local-server nas-ip 127.0.0.1 key huawei#vlan 1#---- More ----5、进入系统视图[Quidway]<Quidway>system-view6、退出系统视图[Quidway] quit7、保存当前配置<Quidway>save(五) 交换机的端口配置端口配置过程:(参见S3500操作手册2端口操作.PDF文档说明)1、进入以太网端口视图[Quidway-Ethernet0/1][Quidway]interface ethernet 0/1。
<Quidway>system-view进入系统视图, 键入Ctrl+Z退回到用户视图.[Quidway]interface ethernet 0/1[Quidway-Ethernet0/1]命令格式interface { interface_type interface_num | interface_name } 2、打开/关闭以太网端口 (禁止某些用户连接到网络)[Quidway-Ethernet0/1] shutdown#interface Aux0/0#interface Ethernet0/1shutdown#interface Ethernet0/2#interface Ethernet0/3#interface Ethernet0/4#interface Ethernet0/5#interface Ethernet0/6#interface Ethernet0/7#interface Ethernet0/8#interface Ethernet0/9[Quidway-Ethernet0/1] undo shutdown#interface Aux0/0#interface Ethernet0/1#interface Ethernet0/2#interface Ethernet0/3#interface Ethernet0/4#interface Ethernet0/5#interface Ethernet0/6#interface Ethernet0/7#interface Ethernet0/8#interface Ethernet0/9例:进入端口视图,执行shutdown 或undo shutdown,并使用display 命令(显示端口的所有信息)观察打开和关闭以太网端口之前和之后的信息shutdownDisplay interface eth 0/1undo shutdownDisplay interface eth 0/13、对以太网端口进行描述[Quidway-Ethernet0/1] description text[Quidway-Ethernet0/1] undo description设置以太网端口描述字符串 description text删除以太网端口描述字符串 undo description例:使用display 命令观察对以太网端口进行描述之前和之后的变化Display interface eth 0/1description dalixueyuanDisplay interface eth 0/1Undo descriptionDisplay interface eth 0/14、配置端口双工工作状态[Quidway-Ethernet0/1]duplex full设置以太网端口的双工状态 duplex { auto | full | half }恢复以太网端口的双工状态为缺省值 undo duplex例:Duplex autoDuplex fullDuplex halfDisplay interface eth 0/15、配置端口工作速率[Quidway-Ethernet0/1]speed ?[Quidway-Ethernet0/1]speed auto设置百兆以太网端口的速率 speed { 10 | 100 | auto }设置千兆以太网端口的速率 speed { 10 | 100 | 1000 | auto }恢复以太网端口的速率为缺省值 undo speed例:speed 10Speed 100Speed autoDisplay interface eth 0/16、设置以太网端口网线类型[Quidway-Ethernet0/1] mdi auto设置以太网端口连接的网线的类型 mdi { across | auto | normal }恢复以太网端口的网线类型为缺省值 undo mdi例:mdi across //交叉类型mdi auto //自动识别mdi normal //普通类型Display interface eth 0/17、用端口聚合将两台交换机之间两条线路聚合为一条逻辑链路(捆绑端口要先配双工和速度)【背景描述】假设某企业采用两台交换机组成一个局域网,由于很多数据流量是跨过交换机进行转发的,因此需要提高交换机之间的传输带宽,并实现链路冗余备份,为此网络管理员在两台交换机之间采用两根网线互连,并将相应的两个端口聚合为一个逻辑端口,现要在交换机上做适当配置来实现这一目标。
交换机Vlan配置

实验三交换机的VLAN配置一、实验目的1. 理解理解Trunk链路的作用和VLAN的工作原理2. 掌握交换机上创建VLAN、接口分配3.掌握利用三层交换机实现VLAN间的路由的方法。
二、实验环境本实验在实验室环境下进行操作,需要的设备有:配置网卡的PC机若干台,双绞线若干条,CONSOLE线缆若干条,思科交换机cisco 2960两台。
三、实验内容1. 单一交换机的VLAN配置;2. 跨交换机VLAN配置,设置Trunk端口;3. 测试VLAN分配结果;4.在三层交换机上实现VLAN的路由;5.测试VLAN间的连通性四、实验原理1.什么是VLANVLAN是建立在局域网交换机上的,以软件方式实现逻辑工作组的划分与管理,逻辑工作组的站点不受物理位置的限制,当一个站点从一个逻辑工作组移到另一个逻辑工作组时,只需要通过软件设定,而不需要改变它在网络中的物理位置;当一个站点从一个物理位置移动到另一个物理位置时,只要将该计算机连入另一台交换机,通过软件设定后该计算机可成为原工作组的一员。
相同VLAN内的主机可以相互直接通信,不同VLAN中的主机之间不能直接通信,需要借助于路由器或具有路由功能的第三层交换机进行转发。
广播数据包只可以在本VLAN内进行广播,不能传输到其他VLAN中。
2.交换机的端口以太网交换机的每个端口都可以分配给一个VLAN,分配给同一个VLAN的端口共享广播域,即一个站点发送广播信息,同一VLAN中的所有站点都可以接收到。
交换机一般都有三种类型的端口:TRUNK口、ACCESS口、CONSOLE口。
CONSOLE端口:它是专门用于对交换机进行配置和管理的。
通过Console端口连接并配置交换机,是配置和管理交换机必须经过的步骤。
ACCESS口(默认):ACCESS端口只能通过缺省VLAN ID的报文。
TRUNK 口:为了让连接在不同交换机但属于同一VLAN 的计算机之间能够相互通信,必须把两个交换机相级联的那两个端口配置成TRUNK 口工作模式。
以太网交换配置实验报告
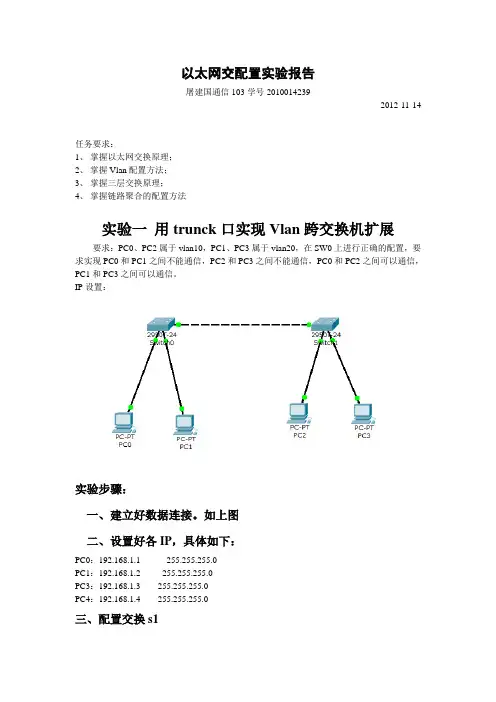
以太网交配置实验报告屠建国通信103学号20100142392012-11-14任务要求:1、掌握以太网交换原理;2、掌握Vlan配置方法;3、掌握三层交换原理;4、掌握链路聚合的配置方法实验一用trunck口实现Vlan跨交换机扩展要求:PC0、PC2属于vlan10,PC1、PC3属于vlan20,在SW0上进行正确的配置,要求实现PC0和PC1之间不能通信,PC2和PC3之间不能通信,PC0和PC2之间可以通信,PC1和PC3之间可以通信。
IP设置:实验步骤:一、建立好数据连接。
如上图二、设置好各IP,具体如下:PC0:192.168.1.1 255.255.255.0PC1:192.168.1.2 255.255.255.0PC3:192.168.1.3 255.255.255.0PC4:192.168.1.4 255.255.255.0三、配置交换s1代码如下:1、在交换机上创建两个vlan,分别是Vlan 10 和Vlan 20Switch>enSwitch#config tEnter configuration commands, one per line. End with CNTL/Z.Switch(config)#vlan 10Switch(config-vlan)#vlan 202、指定两个端口fa0/1 和fa0/2Switch(config)#interface fa0/1Switch(config-if)#switch mode accessSwitch(config-if)#switch access vlan 10Switch(config-if)#interface fa0/2Switch(config-if)#switch mode accessSwitch(config-if)#switch access vlan 203、设置交换机S1与S2连接端口类型,端口fa0/3允许fa0/1和fa0/2通过Switch(config-if)#switch moder trunkSwitch(config-if)#switch trunk allSwitch(config-if)#switch trunk allowed vlan 10,205、查看配置情况,是否成功。
NETGEAR 交换机的基本管理和端口配置
NETGEAR 交换机的基本管理和端口配置1.实验目的本实验将详细描述Netgear系列交换机常用的基本管理特性的操作和端口配置的方法,主要包括以下内容:1.配置交换机的管理IP地址2.配置交换机的固件升级3.配置交换机的基本端口设置通过以上实验操作,实验者可以学会独立安装及交换机基本设置的能力,并能应用于实际网络环境下,另外,如果你不了解交换机基本的设置,那么将无法实现对交换机做全面和深入的配置,尽管这节内容很简单,但也是最基本和必须掌握的内容。
1.1实验条件要完成实验内容,必须具备以下环境.1.NETGEAR 7000系列交换机(以GSM7328S为例,固件版本7.1.1.7)一台2.NETGEAR增强型智能网管交换机(以GS724AT为例,固件版本3.0.61)一台3.NETGEAR基本智能交换机(以FS726T为例,固件版本1.2.4_35)一台4.NETGEAR智能交换机配置向导软件(SmartWizard_2.05.05)5.NETGEAR简单网管交换机(以JFS524E,GS105E为例)两台6.NETGEAR简单网管交换机管理工具(NETGEAR UM+ Utility V1.2B20)7.TFTP Server软件8.NETGEAR7000系列交换机随机9针串口设置电缆一根,网线数条(正线若干根)9.测试用的个人电脑若干注:如果需要获得NETGEAR公司所有产品的最新软件,请平常及时访问,并请注意每个产品升级的注意事项。
2.实验内容2.1配置交换机的管理IP地址2.1.1规划内部网络的IP在配置交换机的管理IP地址之前,我们应该先根据企业使用的实际情况,预先规划及确定企业内部网络的IP地址,依据因特网域名分配组织IANA组织(Internet Assigned Numbers Authority)规划保留了以下三个IP地址块用于私有网络的使用:10.0.0.0 - 10.255.255.255 (10/8比特前缀)172.16.0.0 - 172.31.255.255 (172.16/12比特前缀)192.168.0.0 - 192.168.255.255 (192.168/16比特前缀)NETGEAR系列交换机缺省的设备管理IP局域网地址分为以下几种类型:7000系列交换机:169.254.100.100 / 255.255.0.0;可以通过DHCP服务器动态分配获得IP地址。
交换机基本配置命令
熟悉和掌握交换机配置命令Ⅰ.实验目标:熟悉交换机的编辑命令和帮助命令的使用。
Ⅱ.实验环境:网络实验室,锐捷交换机RG-S2126G,WINDOWS XPⅢ.基本内容:配置交换机的方法(1)(各种窗口菜单的使用)Ⅳ.实验原理:LAN交换技术Ⅴ.实验设备:交换机,主机。
1、网络实验室介绍每小组对应一个实验台,每小组的机柜里有5台设备,从上到下依次为:验设备使用说明⑴RG-RCMS对该组实验台上所有网络设备进行统一的管理和控制,学生作网络实验时,不需要对控制线进行任何的拔插。
⑵登录任一设备的方式为:HTTP://RCMS控制台IP地址:该设备的端口号其中,每小组RCMS控制台的IP地址为:如登录到第一组的第一台交换机的方式为:HTTP:// 172.16.1.1:8080●每台设备的登录密码均为:Star●进入特权方式的命令为:enable 14Ⅵ.实验内容:第一部分:熟悉交换机RG-S2126G(二层交换机)配置命令(1)一、交换机基本操作1.由用户模式进入特权模式Switch>enableSwitch#例如:Switch> enable 14 //进入特权模式Password: starSwitch# config terminal //进入全局配置模式Switch#exitPress RETURN to get started!Switch>二、配置模式:1、全局配置模式:[主机名(config)#]:配置交换机的整体参数2、子模式:⑴线路配置模式:[主机名(config-line)#]:配置交换机的线路参数⑵接口配置模式:[主机名(config-if)#]:配置交换机的接口参数①进入全局配置模式Switch#configure terminalSwitch(config)#exitSwitch#②进入接口配置模式Switch(config)#interface fastEthernet 0/1Switch(config-if)#exitSwitch(config)#③从子模式下直接返回特权模式Switch(config-if)#endSwitch#三、交换机操作帮助特点:1.支持命令简写(按TAB键将命令补充完整)2.在每种操作模式下直接输入“?”显示该模式下所有的命令3.命令空格“?”显示命令参数并对其解释说明4.字符“?”显示以该字符开头的命令5.命令历史缓存:(Ctrl+P)显示上一条命令,(Ctrl+N)显示下一条命令附1:help命令详解要查看帮助系统的一些简要信息,请执行help命令。
交换机的实训报告范文(13篇)
交换机的实训报告范文(13篇)报告范文是一种用来汇报研究、调研、实验等结果的文体,它是对所做工作的归纳和总结,有助于向他人传达自己的观点和结论,让人了解到工作的进展和成果。
看了这么多报告范文,我觉得我们也应该写一篇了。
希望这些报告范文能够帮助大家提高写作水平,为自己的学习和研究提供更多的参考和借鉴。
实训报告1.了解外汇模拟交易系统的构成2.熟悉外汇交易的常见币种、常见的汇率类型。
3.熟悉外汇银行常见的报价方式。
【实验条件】。
1.个人计算机一台,预装windows98操作系统和浏览器。
2.计算机通过局域网形式接入互联网。
【知识准备】。
本实验需要的理论知识是汇率的标价方法以及报价方法。
【实验内容与步骤】。
3.进入世华财讯的国家外汇,了解汇率的类型。
4.进入世华财讯的国家外汇,了解外汇银行对外汇的报价方式。
【实验报告要求】。
实验报告要求写清楚个人的操作步骤。
重点写明如何解决交易中出现的问题。
个人操作的心得体会。
实验二:外汇行情分析。
掌握预测汇率走势的基本分析方法、技术分析方法。
【实验条件】。
1.个人计算机一台,预装windows98操作系统和浏览器。
2.计算机通过局域网形式接入互联网。
【知识准备】。
1.本实验需要的理论知识是汇率的标价方法以及报价方法。
2.影响汇率的基本因素主要有经济、政治、新闻和心理及其他不可预期的因素等。
3.移动平均线、macd、rsi等技术指标。
【实验内容与步骤】。
2.根据这些因素对汇率走势的影响,进而判断这些货币的大致走势。
3.进入世华财讯进行国际外汇的技术指标分析,了解相应货币的技术指标及图形。
4.可重点看看该货币的k线图、移动平均线、macd、kdj、rsi指标等。
【实验报告要求】。
实验报告要求写清楚个人的操作步骤。
重点写明如何解决交易中出现的问题。
个人操作的心得体会。
实验三:外汇实盘交易。
1.学会运用技术分析手段选择货币对进行操作。
2.学会运用国际资本流动影响因素对所选择货币对进行分析。
三层交换机实现VLAN间互通实验报告

Switch(config-if)#switchport access vlan 300
Switch(config-if)#exit
Switch(config)#int vlan 100
Switch(config-if)#
%LINK-5-CHANGED: Interface Vlan100, changed state to up
Switch(config)#vlan 100
Switch(config-vlan)#exit
Switch(config)#vlan 200
Switch(config-vlan)#exit
Switch(config)#vlan 300
Switch(config-vlan)#exit
Switch(config)#int fa0/1
Switch(config-if)#
%LINK-5-CHANGED: Interface Vlan200, changed state to up
%LINEPROTO-5-UPDOWN: Line protocol on Interface Vlan200, changed state to up
Switch(config-if)#ip add 192.168.2.1 255.255.255.0
Switch(config-if)#exit
Switch(config)#int vlan 300
Switch(config-if)#
%LINK-5-CHANGED: Interface Vlan300, changed state to up
%LINEPROTO-5-UPDOWN: Line protocol on Interface Vlan300, changed state to up
串联三层、二层交换机、路由器的配置
实验:串联三层、二层交换机、路由器的配置(二层交换机划分两个VLAN)一、实验介绍:1、实验名称:三层交换机,二层交换机,路由器连通配置2、实验目的:理解二层交换机、三层交换机、路由器串联后,怎样ping通3、实验设备:PC1、PC2、PC3、路由器一个、三层交换机一个、二层交换机一个二、实验拓扑:三、实验步骤1.PC1和路由器的配置:A.PCI配置IP ,:172.16.1.2 掩码:255.255.255.0 网关:172.16.1.1验证:c:\>ipconfigB.路由器F0/0 IP:172.16.1.1 掩码:255.255.255.0F0/1 IP:172.16.2.1 掩码:255.255.255.0>enable 进入特权模式# configure terminal 进入全局模式(config)# interface fastethernet 0/0 进入以太网fa 0/0配置模式(config-if)# ip address 172.16.1.1 255.255.255.0 配置以太网接口0 IP地址、掩码(config-if)# no shutdown 开启端口(config-if)# exit 退回全局模式(config)# interface fastethernet 0/1 进入以太网fa 0/1配置模式(config-if)# ip address 172.16.2.1 255.255.255.0 配置以太网接口1 IP地址、掩码(config-if)# no shutdown 开启端口验证方法:# show running-config 或#show interface serial 2(config-if)# exit 退回全局模式(config)# ip toute 172.16.3.0 255.255.255.0 172.16.2.2 配置3 号网段静态路由(config)# ip toute 172.16.4.0 255.255.255.0 172.16.2.2 配置4 号网段静态路由验证方法:特权模式下打show ip route# write 保存配置2.三层交换机的配置:A.F0/1端口配置IP:172.16.2.2 掩码:255.255.255.0创建VLAN 11 VLAN 22 配置IP:VLAN 11 :172.16.3.1 vlan 22 :172.16.4.1>enable 进入特权模式# configure terminal 进入全局模式(config)# interface fastethernet 0/1 进入以太网fa 0/1配置模式(config-if)# no switchport 端口开启三层交换(config-if)# ip address 172.16.2.2 255.255.255.0 为端口配置IP(config-if)# no shutdown 开启端口(config-if)# exit 退回全局模式(config)# vlan 22 创建vlan 22(config)# vlan 33 创建vlan 33验证:特权模式下打show vlan(config-if)# exit 退回全局模式(config)# interface vlan 22 进入vlan 22 配置模式(config-if)# ip address 172.16.3.1 255.255.255.0 配置vlan 22的IP(config-if)# no shutdown 激活(config)# interface vlan 33 进入vlan 33 配置模式(config-if)# ip address 172.16.4.1 255.255.255.0 配置vlan 33的IP(config-if)# no shutdown 激活(config-if)# exit 退回全局配置模式(config)# ip route 172.16.1.0 255.255.255.0 172.16.2.1 添加1 号网段静态路由(config)# interface fastethernet 0/4 进入以太网fa 0/4配置模式(config-if)# switchport mode trunk 设置为干道# write 保存配置验证:# show running-config 或#show interface serial 2路由验证:show ip route3.二层交换机,PC2,PC3的配置:A.二层交换机划分两个vlanB.P C2 IP:172.16.3.2 掩码:255.255.255.0PC2 IP:172.16.4.2 掩码:255.255.255.0二层交换机配置>enable 进入特权模式# configure terminal 进入全局模式(config)# vlan 22 创建vlan 22(config)# vlan 33 创建vlan 33(config)# interface fastethernet 0/2 进入2端口配置模式(config-if)# switchport access vlan 22 将2 端口加入vlan 22(config-if)# exit 退回全局配置模式(config)# interface fastethernet 0/3 进入3端口配置模式(config-if)# switchport access vlan 33 将3 端口加入vlan 33config-if)# exit 退回全局模式(config)# interface fastethernet 0/4 进入4端口配置模式(config-if)# switchport mode trunk 设置为干道# write 保存配置验证:show vlanPC配置A.PC2 IP:172.16.3.2 掩码:255.255.255.0 网关:172.16.3.1 B.PC2 IP:172.16.4.2 掩码:255.255.255.0 网关:172.16.4.14.测试:PCI ping 172.16.1.1 172.16.2.1 172.16.2.2172.16.3.1172.16.4.1172.16.3.2 172.16.4.2PC2 Ping 172.16.3.1 172.16.4.1 172.16.4.2172.16.2.2172.16.2.1172.16.1.1 172.16.1.2PC3 ping 172.16.4.1 172.16.3.1 172.16.3.2172.16.2.2 172.16.2.1172.16.1.1 172.16.1.2。
交换机、路由器综合实验(三)
交换机、路由器综合实验(三)一、实验目的:掌握较复杂网络的交换机和路由器的配置问题。
二、实验环境:Cisco路由器3台;Catalyst 3550交换机1台;PC机3台。
图1说明:三层交换机将内网分割为三个子网192.168.0.0、192.168.1.0、192.168.2.0;路由器R1负责内网与外网的连接,并实现NAT功能;R1、R2、R3之间通过路由协议识别各个网络,由于内网采用了私有IP地址进行编址,它对外网应该是不可见的,所以启用路由协议时不要启用内部网络。
三、实验工具:Boson Netsim模拟器四、实验内容:(1) 按图1所示连接网络;(2) 配置路由器R1:路由器的名字为R1;F0口的IP地址:192.168.0.1/24,设置F0口为NAT输入端;S0口的IP地址:200.1.1.1/24,设置S0口为NAT输出端;配置NAT池,地址范围为200.1.1.10~200.1.1.20,将内网中格式为192.168.*.* 的IP 地址转换为NAT池中的IP地址;配置静态路由,将目的网络为192.168.1.0 或192.168.2.0 的数据报发往192.168.0.2;配置OSPF路由协议,区域号为10,在它的外网地址上启用协议。
(3) 配置路由器R2:路由器的名字为R2;S0口的IP地址:222.2.2.1/24;S1口的IP地址:200.1.1.2/24;配置OSPF路由协议,区域号为10,在它的所有直连网络上启用协议。
(4) 配置路由器R3:路由器的名字为R3;F0口的IP地址:18.1.1.1/8;S0口的IP地址:222.2.2.2/24;配置OSPF路由协议,区域号为10,在它的所有直连网络上启用协议。
(5) 配置三层交换机:把F0/1口设置为三层路由口,IP地址为192.168.0.2/24;把F0/2口设置为三层路由口,IP地址为192.168.1.1/24;把F0/3口设置为三层路由口,IP地址为192.168.2.1/24;配置默认路由,方向为R1路由器的F0口;启用路由功能。
路由器交换机配置实验三
路由一配置:Router(config)#host R1R1(config-line)#exitR1(config)#in e0/0R1(config-if)#ip add 192.168.1.1 255.255.255.252R1(config-if)#no shutR1(config-if)#in e0/1R1(config-if)#ip add 172.16.128.1 255.255.255.0R1(config-if)#no shutR1(config-if)#in e0/2R1(config-if)#ip add 172.16.130.1 255.255.255.0R1(config-if)#no shutR1(config-if)#in e0/3R1(config-if)#ip add 172.16.138.1 255.255.255.0R1(config-if)#no shutR1(config-if)#router ospf 1R1(config-router)#network 192.168.1.0 0.0.0.3 area 1R1(config-router)#exitR1(config)#router ripR1(config-router)#network 172.16.0.0R1(config-router)#exitR1(config)#do show ip ospf neighbor2192.168.2.251/28 R2上学习到的192.168.3.0的路由只能有一条Neighbor ID Pri State Dead Time Address Interface 192.168.2.251 1 FULL/DR 00:00:36 192.168.1.2 Ethernet0/0 R1(config)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set172.16.0.0/24 is subnetted, 3 subnetsC 172.16.138.0 is directly connected, Ethernet0/3C 172.16.128.0 is directly connected, Ethernet0/1C 172.16.130.0 is directly connected, Ethernet0/2192.168.1.0/30 is subnetted, 1 subnetsC 192.168.1.0 is directly connected, Ethernet0/0192.168.2.0/28 is subnetted, 1 subnetsO IA 192.168.2.240 [110/20] via 192.168.1.2, 00:01:33, Ethernet0/0192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksO IA 192.168.3.0/25 [110/40] via 192.168.1.2, 00:01:09, Ethernet0/0O IA 192.168.3.248/30 [110/30] via 192.168.1.2, 00:01:23, Ethernet0/0R1(config)#router ospf 1R1(config-router)#redistribute rip subnets metric 30 metric-type 1R1(config-router)#exitR1(config)#router ripR1(config-router)#redistribute ospf 1 metric 2R1(config-router)#passive-interface e0/0R1(config-router)#exitR1(config)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set172.16.0.0/24 is subnetted, 3 subnetsC 172.16.138.0 is directly connected, Ethernet0/3C 172.16.128.0 is directly connected, Ethernet0/1C 172.16.130.0 is directly connected, Ethernet0/210.0.0.0/24 is subnetted, 1 subnetsO E1 10.1.1.0 [110/60] via 192.168.1.2, 00:01:38, Ethernet0/0 192.168.1.0/30 is subnetted, 1 subnetsC 192.168.1.0 is directly connected, Ethernet0/0192.168.2.0/28 is subnetted, 1 subnetsO IA 192.168.2.240 [110/20] via 192.168.1.2, 00:03:35, Ethernet0/0 192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksO IA 192.168.3.0/25 [110/40] via 192.168.1.2, 00:03:35, Ethernet0/0O IA 192.168.3.248/30 [110/30] via 192.168.1.2, 00:03:35, Ethernet0/0 R1(config)#do ping 10.1.1.1 source 172.16.130.1Type escape sequence to abort.Sending 5, 100-byte ICMP Echos to 10.1.1.1, timeout is 2 seconds:Packet sent with a source address of 172.16.130.1Success rate is 100 percent (5/5), round-trip min/avg/max = 96/172/300 ms R1(config)#router ospf 1R1(config-router)#area 1 nssaR1(config-router)#summary-address 172.16.128.0 255.255.240.0R1(config-router)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is 192.168.1.2 to network 0.0.0.0172.16.0.0/16 is variably subnetted, 4 subnets, 2 masksC 172.16.138.0/24 is directly connected, Ethernet0/3C 172.16.128.0/24 is directly connected, Ethernet0/1O 172.16.128.0/20 is a summary, 00:01:04, Null0C 172.16.130.0/24 is directly connected, Ethernet0/2192.168.1.0/30 is subnetted, 1 subnetsC 192.168.1.0 is directly connected, Ethernet0/0O*IA 0.0.0.0/0 [110/11] via 192.168.1.2, 00:02:55, Ethernet0/0注:只有在重发布以后才可运行NSSA,NSSA的配置必须是双向的路由二配置:Router(config)#host R2R2(config)#in e0/0R2(config-if)#ip add 192.168.1.2 255.255.255.252R2(config-if)#no shutR2(config-if)#in e0/1R2(config-if)#ip add 192.168.2.251 255.255.255.240R2(config-if)#no shutR2(config-if)#router ospf 1R2(config-router)#network 192.168.2.240 0.0.0.15 area 0R2(config-router)#network 192.168.1.0 0.0.0.3 area 1R2(config-router)#exitR2(config)#do show ip ospf neighborNeighbor ID Pri State Dead Time Address Interface 192.168.3.249 1 FULL/DR 00:00:37 192.168.2.243 Ethernet0/1 192.168.1.1 1 FULL/BDR 00:00:31 192.168.1.1 Ethernet0/0 R2(config)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set192.168.1.0/30 is subnetted, 1 subnetsC 192.168.1.0 is directly connected, Ethernet0/0192.168.2.0/28 is subnetted, 1 subnetsC 192.168.2.240 is directly connected, Ethernet0/1192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksO IA 192.168.3.0/25 [110/30] via 192.168.2.243, 00:01:22, Ethernet0/1O IA 192.168.3.248/30 [110/20] via 192.168.2.243, 00:01:37, Ethernet0/1R2(config)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set172.16.0.0/24 is subnetted, 3 subnetsO E1 172.16.138.0 [110/40] via 192.168.1.1, 00:01:48, Ethernet0/0O E1 172.16.128.0 [110/40] via 192.168.1.1, 00:01:48, Ethernet0/0O E1 172.16.130.0 [110/40] via 192.168.1.1, 00:01:48, Ethernet0/010.0.0.0/24 is subnetted, 1 subnetsO E1 10.1.1.0 [110/50] via 192.168.2.243, 00:01:48, Ethernet0/1 192.168.1.0/30 is subnetted, 1 subnetsC 192.168.1.0 is directly connected, Ethernet0/0192.168.2.0/28 is subnetted, 1 subnetsC 192.168.2.240 is directly connected, Ethernet0/1192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksO IA 192.168.3.0/25 [110/30] via 192.168.2.243, 00:03:45, Ethernet0/1 O IA 192.168.3.248/30 [110/20] via 192.168.2.243, 00:03:45, Ethernet0/1 R2(config)#router ospf 1R2(config-router)#area 1 nssa no-summaryR2(config-router)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set172.16.0.0/20 is subnetted, 1 subnetsO N1 172.16.128.0 [110/40] via 192.168.1.1, 00:01:09, Ethernet0/010.0.0.0/24 is subnetted, 1 subnetsO E1 10.1.1.0 [110/50] via 192.168.2.243, 00:01:09, Ethernet0/1 192.168.1.0/30 is subnetted, 1 subnetsC 192.168.1.0 is directly connected, Ethernet0/0192.168.2.0/28 is subnetted, 1 subnetsC 192.168.2.240 is directly connected, Ethernet0/1O IA 192.168.3.0/24 [110/20] via 192.168.2.243, 00:01:14, Ethernet0/1路由三配置:Router(config)#host R3R3(config)#in e0/1R3(config-if)#ip add 192.168.2.243 255.255.255.240R3(config-if)#no shutR3(config-if)#in e0/2R3(config-if)#ip add 192.168.3.249 255.255.255.252R3(config-if)#no shutR3(config-if)#router ospf 1R3(config-router)#network 192.168.3.248 0.0.0.3 area 2R3(config-router)#network 192.168.2.240 0.0.0.15 area 0R3(config-router)#do show ip ospf neighborNeighbor ID Pri State Dead Time Address Interface 192.168.2.251 1 FULL/DR 00:00:32 192.168.2.251 Ethernet0/1 192.168.3.250 1 FULL/BDR 00:00:36 192.168.3.250 Ethernet0/2 R3(config-router)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set192.168.1.0/30 is subnetted, 1 subnetsO IA 192.168.1.0 [110/20] via 192.168.2.251, 00:01:31, Ethernet0/1192.168.2.0/28 is subnetted, 1 subnetsC 192.168.2.240 is directly connected, Ethernet0/1192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksO 192.168.3.0/25 [110/20] via 192.168.3.250, 00:01:31, Ethernet0/2C 192.168.3.248/30 is directly connected, Ethernet0/2R3(config-router)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set172.16.0.0/24 is subnetted, 3 subnetsO E1 172.16.138.0 [110/50] via 192.168.2.251, 00:02:01, Ethernet0/1O E1 172.16.128.0 [110/50] via 192.168.2.251, 00:02:01, Ethernet0/1O E1 172.16.130.0 [110/50] via 192.168.2.251, 00:02:01, Ethernet0/110.0.0.0/24 is subnetted, 1 subnetsO E1 10.1.1.0 [110/40] via 192.168.3.250, 00:02:01, Ethernet0/2192.168.1.0/30 is subnetted, 1 subnetsO IA 192.168.1.0 [110/20] via 192.168.2.251, 00:02:01, Ethernet0/1 192.168.2.0/28 is subnetted, 1 subnetsC 192.168.2.240 is directly connected, Ethernet0/1192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksO 192.168.3.0/25 [110/20] via 192.168.3.250, 00:02:01, Ethernet0/2 C 192.168.3.248/30 is directly connected, Ethernet0/2R3(config-router)#area 2 nssa no-summaryR3(config-router)#area 2 range 192.168.3.0 255.255.255.0R3(config-router)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set172.16.0.0/20 is subnetted, 1 subnetsO E1 172.16.128.0 [110/50] via 192.168.2.251, 00:03:59, Ethernet0/110.0.0.0/24 is subnetted, 1 subnetsO N1 10.1.1.0 [110/50] via 192.168.3.250, 00:03:59, Ethernet0/2 192.168.1.0/30 is subnetted, 1 subnetsO IA 192.168.1.0 [110/20] via 192.168.2.251, 00:03:59, Ethernet0/1 192.168.2.0/28 is subnetted, 1 subnetsC 192.168.2.240 is directly connected, Ethernet0/1192.168.3.0/24 is variably subnetted, 3 subnets, 3 masksO 192.168.3.0/25 [110/20] via 192.168.3.250, 00:03:59, Ethernet0/2 O 192.168.3.0/24 is a summary, 00:03:59, Null0C 192.168.3.248/30 is directly connected, Ethernet0/2路由四配置:Router(config)#host R4R4(config)#in e0/2R4(config-if)#ip add 192.168.3.250 255.255.255.252R4(config-if)#no shutR4(config-if)#in e0/1R4(config-if)#ip add 192.168.3.1 255.255.255.128R4(config-if)#no shutR4(config-if)#in e0/0R4(config-if)#ip add 10.1.1.1 255.255.255.0R4(config-if)#no shutR4(config-if)#router ospf 1R4(config-router)#network 192.168.3.248 0.0.0.3 area 2R4(config-router)#network 192.168.3.0 0.0.0.127 area 2R4(config-router)#exitR4(config)#router ripR4(config-router)#network 10.0.0.0R4(config-router)#exitR4(config)#do show ip ospf neighborNeighbor ID Pri State Dead Time Address Interface 192.168.3.249 1 FULL/BDR 00:00:36 192.168.3.249 Ethernet0/2 R4(config)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set10.0.0.0/24 is subnetted, 1 subnetsC 10.1.1.0 is directly connected, Ethernet0/0192.168.1.0/30 is subnetted, 1 subnetsO IA 192.168.1.0 [110/30] via 192.168.3.249, 00:01:36, Ethernet0/2192.168.2.0/28 is subnetted, 1 subnetsO IA 192.168.2.240 [110/20] via 192.168.3.249, 00:01:36, Ethernet0/2 192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksC 192.168.3.0/25 is directly connected, Ethernet0/1C 192.168.3.248/30 is directly connected, Ethernet0/2R4(config)#router ospf 1R4(config-router)#redistribute rip subnets metric 30 metric-type 1R4(config-router)#exitR4(config)#router ripR4(config-router)#redistribute ospf 1 metric 2R4(config-router)#passive-interface e0/2R4(config-router)#exitR4(config)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is not set172.16.0.0/24 is subnetted, 3 subnetsO E1 172.16.138.0 [110/60] via 192.168.3.249, 00:01:19, Ethernet0/2O E1 172.16.128.0 [110/60] via 192.168.3.249, 00:01:19, Ethernet0/2O E1 172.16.130.0 [110/60] via 192.168.3.249, 00:01:19, Ethernet0/210.0.0.0/24 is subnetted, 1 subnetsC 10.1.1.0 is directly connected, Ethernet0/0192.168.1.0/30 is subnetted, 1 subnetsO IA 192.168.1.0 [110/30] via 192.168.3.249, 00:01:19, Ethernet0/2 192.168.2.0/28 is subnetted, 1 subnetsO IA 192.168.2.240 [110/20] via 192.168.3.249, 00:01:19, Ethernet0/2 192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksC 192.168.3.0/25 is directly connected, Ethernet0/1C 192.168.3.248/30 is directly connected, Ethernet0/2R4(config)#do ping 172.16.138.1 source 10.1.1.1Type escape sequence to abort.Sending 5, 100-byte ICMP Echos to 172.16.138.1, timeout is 2 seconds: Packet sent with a source address of 10.1.1.1Success rate is 100 percent (5/5), round-trip min/avg/max = 96/168/260 ms R4(config)#router ospf 1R4(config-router)#area 2 nssa no-summaryR4(config-router)#do show ip routeCodes: C - connected, S - static, R - RIP, M - mobile, B - BGPD - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2ia - IS-IS inter area, * - candidate default, U - per-user static routeo - ODR, P - periodic downloaded static routeGateway of last resort is 192.168.3.249 to network 0.0.0.010.0.0.0/24 is subnetted, 1 subnetsC 10.1.1.0 is directly connected, Ethernet0/0192.168.3.0/24 is variably subnetted, 2 subnets, 2 masksC 192.168.3.0/25 is directly connected, Ethernet0/1C 192.168.3.248/30 is directly connected, Ethernet0/2O*IA 0.0.0.0/0 [110/11] via 192.168.3.249, 00:05:56, Ethernet0/2R4(config-router)#do ping 172.16.130.1 source 10.1.1.1Type escape sequence to abort.Sending 5, 100-byte ICMP Echos to 172.16.130.1, timeout is 2 seconds:Packet sent with a source address of 10.1.1.1Success rate is 100 percent (5/5), round-trip min/avg/max = 100/193/312 ms实验步骤总结:R1 1、OSPF ,RIP 2、查看邻接关系3、重发布4、完全NSSA5、地址汇总R2 1、OSPF 2、查看邻接关系3、完全NSSAR3 1、OSPF 2、查看邻接关系3、完全NSSA 4、地址汇总R4 1、OSPF ,RIP 2、查看邻接关系3、重发布4、完全NSSA。
vlan间通信三层交换机路由实验报告
实验报告.实验目的进一步理解三层交换机配置的基本原理; 熟练掌握PacketTracer 软件的安装和配置方法; 掌握三层交换机的基本命令配置。
掌握vlan 之间路由的含义。
•实验环境(软件、硬件及条件) 1台2811路由器; 2台工作站; 2台2960的交换机; 网络连接线路若干(双绞线); 网络拓朴结构如下:6、软件:windows xp 操作系统、PacketTracer 软件。
三、实验规划vlan 10;192.ise.11/24GO/2 vlvi 20:192 168. 2.1/E4 Xtrunk \ Gl/1 irliii 20: s*0 £0/2-2斗\ £0/2 ■"12960-24TT S witch 0GO/1 35 码Multil Aer Strunk /Gl/I 1 r | fO/2/ j「一^29S0-24TTSwitchlPC-PT PCIFC1:1^ 163.1 100/24PC*PT PC2FC2:192.16S 2 100/24实验名称 课程名称Vian 间路由三层交换实验计算机网络实训1、 2、31、 2、 3、间路由-二层交换 1*—二层交换机:SW3560GiO/1trunkGiO/2 trunkvlan 10 192.168. L 1/24 swl fO/2-24vlan 20192.16& 2.1/24sw2 fO/2-24交换机「Swl 2960Gil/ItrunkfO/2->PCl交换机:SwO 2960Gil/1trunkfO/2->PC2IPC1: 192.168.1.100/24]PC2: 192.168. 2.100/241、启动PacketTracer 软件,选择路由器、PC 构成以上拓扑结构,画出拓扑图,vlan 10:192. 169. 1. 1/24 trunk PC-PTPCIPCI :192.16B.1 100/24然后用PacketTracer 软件对此网络进行配置。