
ACL详解
CISCO ACL配置详解什么是ACL?访问控制列表简称为ACL,访问控制列表使用包过滤技术,在路由器上读取第三层及第四层包头中的信息如源地址,目的地址,源端口,目的端口等,根据预先定义好的规则对包进行过滤,从而达到访问控制的目的。
该技术初期仅在路由器上支持,近些年来已经扩展到三层交换机,部分最新的二层交换机也开始提供ACL的支持了。
访问控制列表的原理对路由器接口来说有两个方向出:已经经路由器的处理,正离开路由器接口的数据包入:已经到达路由器接口的数据包,将被路由器处理。
匹配顺序为:“自上而下,依次匹配”。
默认为拒绝访问控制列表的类型标准访问控制列表:一般应用在out出站接口。
建议配置在离目标端最近的路由上扩展访问控制列表:配置在离源端最近的路由上,一般应用在入站in方向命名访问控制列表:允许在标准和扩展访问列表中使用名称代替表号访问控制列表使用原则1、最小特权原则只给受控对象完成任务所必须的最小的权限。
也就是说被控制的总规则是各个规则的交集,只满足部分条件的是不容许通过规则的。
2、最靠近受控对象原则也就是说在检查规则时是采用自上而下在ACL中一条条检测的,只要发现符合条件了就立刻转发,而不继续检测下面的ACL语句。
3、默认丢弃原则在CISCO路由交换设备中默认最后一句为ACL中加入了DENY ANY ANY,也就是丢弃所有不符合条件的数据包。
由于ACL是使用包过滤技术来实现的,过滤的依据又仅仅只是第三层和第四层包头中的部分信息,这种技术具有一些固有的局限性,如无法识别到具体的人,无法识别到应用内部的权限级别等。
因此,要达到端到端的权限控制目的,需要和系统级及应用级的访问权限控制结合使用。
一、标准访问列表访问控制列表ACL分很多种,不同场合应用不同种类的ACL。
其中最简单的就是标准访问控制列表,标准访问控制列表是通过使用IP包中的源IP地址进行过滤,使用访问控制列表号1到99来创建相应的ACL。
它的具体格式:access-list access-list-number [permit | deny ] [sourceaddress][wildca rd-mask]access-list-number 为1-99 或者1300-1999之间的数字,这个是访问列表号。
例如:access-list 10 deny host 192.168.1.1这句命令是将所有来自192.16 8.1.1地址的数据包丢弃。
当然我们也可以用网段来表示,对某个网段进行过滤。
命令如下:access-list 10 deny 192.168.1.0 0.0.0.255通过上面的配置将来自192.168.1.0/24的所有计算机数据包进行过滤丢弃。
为什么后头的子网掩码表示的是0.0.0.255呢?这是因为CISCO规定在ACL中用反向掩玛表示子网掩码,反向掩码为0.0.0.255的代表他的子网掩码为255.255. 255.0。
小提示:对于标准访问控制列表来说,默认的命令是HOST,也就是说access-list 10 deny 192.168.1.1表示的是拒绝192.168.1.1这台主机数据包通讯,可以省去我们输入host命令。
标准访问列表配置实例:R1(config)#access-list 10 deny 192.168.2.0 0.0.0.255R1(config)#access-list 10 permit anyR1(config)#int fa0/0.1R1(config-subif)#ip access-group 10 out上面配置的含义是阻止来自网段192.168.2.0的机器从int fa0/0.1端口出去,访问列表在配置好之后,要把它在端口上应用,否则配置了还是无效的。
注意事项:1、标准访问列表,一般来说配置尽量靠近目的端。
2、配置的第二条命令中的any相当于0.0.0.0 255.255.255.2553、一定要加permit any,使其他的网络可通。
4、访问列表是从上到下一条一条进行匹配的,所以在设置访问列表的时候要注意顺序。
如果从第一条匹配到最后一条还是不知道要怎么做,路由器就会丢弃这个数据包,也就是为什么上面的例子中上一定要加permit any。
5、如果只阻止一个主机,那可以用host 192.168.1.12 或者192.168.1.1 2 0.0.0.0,这两种配置是等价的。
删除已建立的标准ACLR1(config)#no access-list +access-list number对标准的ACL来说,不能删除单个acl语句,只能删除整个ACL总结:标准ACL占用路由器资源很少,是一种最基本最简单的访问控制列表格式。
应用比较广泛,经常在要求控制级别较低的情况下使用。
如果要更加复杂的控制数据包的传输就需要使用扩展访问控制列表了,他可以满足我们到端口级的要求。
二、扩展访问控制列表上面我们提到的标准访问控制列表是基于IP地址进行过滤的,是最简单的ACL。
那么如果我们希望将过滤细到端口怎么办呢?或者希望对数据包的目的地址进行过滤。
这时候就需要使用扩展访问控制列表了。
使用扩展IP访问列表可以有效的容许用户访问物理LAN而并不容许他使用某个特定服务(例如WWW,F TP等)。
扩展访问控制列表使用的ACL号为100到199。
扩展访问控制列表的格式:access-list access-list number {permit/deny} protocol +源地址+反码+目标地址+反码+operator operan(It小于,gt大于,eq等于,neq不等于.具体可?)+端口号1、扩展访问控制列表号的范围是100-199或者2000-2699。
2、因为默认情况下,每个访问控制列表的末尾隐含deny all,所以在每个扩展访问控制列表里面必须有:access-list 110 permit ip any any 。
3、不同的服务要使用不同的协议,比如TFTP使用的是UDP协议。
4、更多注意事项可以参考上面标准访问控制列表部分例如:access-list 101 deny tcp any host 192.168.1.1 eq www //将所有主机访问192.168.1.1这个地址网页服务(WWW)TCP连接的数据包丢弃。
小提示:同样在扩展访问控制列表中也可以定义过滤某个网段,当然和标准访问控制列表一样需要我们使用反向掩码定义IP地址后的子网掩码。
扩展访问控制列表配置实例:R2(config)#access-list 110 deny tcp any host 192.168.1.12 eq wwwR2(config)#access-list 110 deny tcp any host 192.168.1.12 eq ftpR2(config)#int fa0/0R2(config-if)#ip access-group 110 out上面配置的含义是拒绝访问192.168.1.12的www和ftp服务实例二:路由器连接了二个网段,分别为172.16.4.0/24,172.16.3.0/24。
在172.16.4.0/ 24网段中有一台服务器提供WWW服务,IP地址为172.16.4.13。
要求:禁止172.16.3.0的计算机访问172.16.4.0的计算机,包括那台服务器,不过惟独可以访问172.16.4.13上的WWW服务,而其他服务不能访问。
路由器配置命令:access-list 101 permit tcp any 172.16.4.13 0.0.0.0 eq www //设置AC L101,容许源地址为任意IP,目的地址为172.16.4.13主机的80端口即WW W服务。
由于CISCO默认添加DENY ANY的命令,所以ACL只写此一句即可。
进入相应端口ip access-group 101 out //将ACL101应用到端口设置完毕后172.16.3.0的计算机就无法访问172.16.4.0的计算机了,就算是服务器172.16.4.13开启了FTP服务也无法访问,惟独可以访问的就是172.16.4. 13的WWW服务了。
删除已建立的扩展标准ACL删除和标准一样,不能单条删除,只能删除整个acl总结:扩展ACL功能很强大,他可以控制源IP,目的IP,源端口,目的端口等,能实现相当精细的控制,扩展ACL不仅读取IP包头的源地址/目的地址,还要读取第四层包头中的源端口和目的端口的IP。
不过他存在一个缺点,那就是在没有硬件ACL加速的情况下,扩展ACL会消耗大量的路由器CPU资源。
所以当使用中低档路由器时应尽量减少扩展ACL的条目数,将其简化为标准ACL或将多条扩展ACL合一是最有效的方法。
三、命名访问控制列表不管是标准访问控制列表还是扩展访问控制列表都有一个弊端,那就是当设置好ACL的规则后发现其中的某条有问题,希望进行修改或删除的话只能将全部AC L信息都删除。
也就是说修改一条或删除一条都会影响到整个ACL列表。
这一个缺点影响了我们的工作,为我们带来了繁重的负担。
不过我们可以用基于名称的访问控制列表来解决这个问题。
命名访问控制列表格式:ip access-list {standard/extended} access-list-name(可有字母,数字组合的字符串)例如:ip access-list standard softer //建立一个名为softer的标准访问控制列表。
命名访问控制列表使用方法:router(config)#ip access-list standard +自定义名router(config-std-nac1)#11 permit host +ip //默认情况下第一条为10,第二条为20.如果不指定序列号,则新添加的ACL被添加到列表的末尾router(config-std-nac1)#deny any对于命名ACL来说,可以向之前的acl中插入acl,删除也可以删除单条acl,如:router(config)#ip access-list standard benetrouter(config-std-nasl)#no 11使用show access-lists可查看配置的acl信息总结:如果设置ACL的规则比较多的话,应该使用基于名称的访问控制列表进行管理,这样可以减轻很多后期维护的工作,方便我们随时进行调整ACL规则。
四、反向访问控制列表反向访问控制列表属于ACL的一种高级应用。
他可以有效的防范病毒。
通过配置反向ACL可以保证AB两个网段的计算机互相PING,A可以PING通B而B 不能PING通A。
ACL知识点详解

A C L知识点详解-标准化文件发布号:(9556-EUATWK-MWUB-WUNN-INNUL-DDQTY-KII第一节TCP/IP传输层与应用层TCP/IP OSITCP/IP:网络访问层协议1~3章第7 章TCP/IP:互联网络层协议5~6章Internet层的功能10.20.30.2/24172.16.1.2/24172.31.255.2/24●互联网络层给每个网络的每台网络设备和主机配置所属的IP地址,实现逻辑寻址。
●能够建立网络与网络、主机与主机之间的连通性,但不保证数据传输的可靠性。
TCP/IP:传输层协议●传输控制协议(TCP)✓面向连接,每传输一个数据分段,都建立一个连接✓可靠的传输●用户数据报协议(UDP)✓无连接,将数据分段发送出去后不确认对方是否已接收到✓不可靠,需要应用层协议提供可靠性TCP 与UDP 协议●TCP与UDP协议使用端口号来区分主机上同一时间的不同会话。
●TCP端口号范围为:0~65535●UDP端口号范围为:0~65535●传输层提供从源主机到目的主机的传输服务,在网络端点之间建立逻辑连接。
●传输层TCP协议能够实现数据传输的可靠性。
●传输层能够实现数据传输时的流控制。
主机之间的多会话●一台服务器可能提供多种服务,如Web和FTP ,在传输层用端口来区分每个应用服务。
●客户端也需要向多个目的发送不同的数据连接,使用端口区分每个连接。
●服务器使用知名端口号0~1023 提供服务。
●客户端使用高于1023的随机端口号作为源端口对外发起数据连接请求,并为每一个连接分配不TCP/IP:应用层协议●Web服务:HTTP ---TCP 80 号端口●文件传输服务:FTP ---TCP 20、21 号端口TFTP ---UDP 69 号端口●电子邮件服务:SMTP ---TCP 25 号端口POP3 ---TCP 110 号端口IMAP4 ---TCP 143 号端口●域名服务:DNS ---TCP、UDP 53 号端口●远程登录:Telnet ---TCP 23 号端口SSH ---TCP 22 号端口●网络管理:SNMP ---UDP 161 号端口第二节访问控制列表问题1能否实现以下限制:除了老板以外,其他员工只能访问互联网Web、FTP和电子邮件等常用服务,拒绝BT、电驴、在线电影、网络游戏甚至QQ、MSN等与工作无关的数据。
ROUTE-policy路由策略规则详解

ROUTE-POLICY 路由策略规则详解在实际工程中经常用到route-policy的情况,下面对route-policy和ACL的详细匹配规则做以说明:一、标准访问列表:#acl number 2000rule 0 permit source 192.168.1.0 0.0.0.255此类ACL用于route-policy时做前缀匹配,即路由条目和规则条目做AND 运算,结果落在反掩码的包含范围之内的则匹配成功。
对于上述配置:192.168.1.0/24 192.168.1.0 /25 192.168.1.0/30 等均可匹配,但是192.168.1.0/16 等则匹配不成功。
二、扩展访问列表:#acl number 3000rule 0 permit ip source 192.168.1.0 0 destination 255.255.255.0 0acl number 3001rule 0 deny ip source 192.168.1.0 0 destination 255.255.255.0 0此类ACL比较特殊,源和目的的掩码均要为0 。
用于route-policy 是要做严格的匹配,即前缀要和source 匹配,前缀的掩码部分要和destination匹配。
对于上述配置3000来说,则只有192.168.1.0/24可与之匹配。
此类列表和Route-policy 配合可用于严格的匹配一条路由条目。
三、permit+permit的route-policy#route-policy t1 permit node 10if-match acl 3000apply local-preference 1300route-policy t1 permit node 20对于route-policy的permit规则来说,凡是能够匹配ACL permit规则的条目就执行node 10中的apply 规则,并不再继续匹配下面的规则。
Cisco路由器配置ACL详解之扩展访问控制列表
Cisco路由器配置ACL详解之扩展访问控制列表Cisco路由器配置ACL详解之扩展访问控制列表扩展访问控制列表:上⾯我们提到的标准访问控制列表是基于IP地址进⾏过滤的,是最简单的ACL。
那么如果我们希望将过滤细到端⼝怎么办呢?或者希望对数据包的⽬的地址进⾏过滤。
这时候就需要使⽤扩展访问控制列表了。
使⽤扩展IP访问列表可以有效的容许⽤户访问物理LAN⽽并不容许他使⽤某个特定服务(例如WWW,FTP等)。
扩展访问控制列表使⽤的ACL号为100到199。
扩展访问控制列表的格式:扩展访问控制列表是⼀种⾼级的ACL,配置命令的具体格式如下:access-list ACL号 [permit|deny] [协议] [定义过滤源主机范围] [定义过滤源端⼝] [定义过滤⽬的主机访问] [定义过滤⽬的端⼝]例如:access-list 101 deny tcp any host 192.168.1.1 eq www这句命令是将所有主机访问192.168.1.1这个地址⽹页服务(WWW)TCP连接的数据包丢弃。
⼩提⽰:⼩提⽰:同样在扩展访问控制列表中也可以定义过滤某个⽹段,当然和标准访问控制列表⼀样需要我们使⽤反向掩码定义IP地址后的⼦⽹掩码。
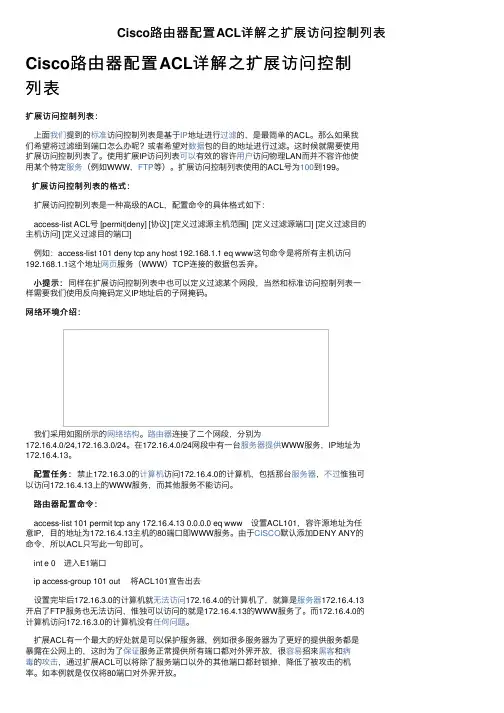
⽹络环境介绍:我们采⽤如图所⽰的⽹络结构。
路由器连接了⼆个⽹段,分别为172.16.4.0/24,172.16.3.0/24。
在172.16.4.0/24⽹段中有⼀台服务器提供WWW服务,IP地址为172.16.4.13。
配置任务:禁⽌172.16.3.0的计算机访问172.16.4.0的计算机,包括那台服务器,不过惟独可配置任务:以访问172.16.4.13上的WWW服务,⽽其他服务不能访问。
路由器配置命令:access-list 101 permit tcp any 172.16.4.13 0.0.0.0 eq www 设置ACL101,容许源地址为任意IP,⽬的地址为172.16.4.13主机的80端⼝即WWW服务。
Linux下ACL详解
ACL 简介用户权限管理始终是Unix 系统管理中最重要的环节。
大家对Linux/Unix 的UGO 权限管理方式一定不陌生,还有最常用的chmod 命令。
为了实现一些比较复杂的权限管理,往往不得不创建很多的组,并加以详细的记录和区分(很多时候就是管理员的噩梦)。
可以针对某一个用户对某一文件指定一个权限,恐怕管理员都期待的功能。
比如对某一个特定的文件,用户A可以读取,用户B所在的组可以修改,惟独用户B不可以……。
于是就有了IEEE POSIX 1003.1e这个ACL的标准。
所谓ACL,就是Access Control List,一个文件/目录的访问控制列表,可以针对任意指定的用户/组分配RWX权限。
现在主流的商业Unix系统都支持ACL。
FreeBSD也提供了对ACL的支持。
Linux在这个方面也不会落后,从2.6版内核开始支持ACL。
准备工作支持ACL需要内核和文件系统的支持。
现在2.6内核配合EXT2/EXT3, JFS, XFS, ReiserFS等文件系统都是可以支持ACL的。
用自己工作用的物理分区体验ACL,总是不明智的行为。
万一误操作导致分区的损坏,造成数据的丢失,损失就大了。
作一个loop设备是个安全的替代方法。
这样不需要一个单独的分区,也不需要很大的硬盘空间,大约有个几百KB就足够进行我们的体验了。
OK,下面我使用Fedora Core 5和Ext3文件开始对Linux的ACL的体验。
首先创建一个512KB的空白文件:[root@FC3-vm opt]# dd if=/dev/zero of=/opt/testptn count=512512+0 records in512+0 records out和一个loop设备联系在一起:[root@FC3-vm opt]# losetup /dev/loop0 /opt/testptn创建一个EXT2的文件系统:[root@FC3-vm opt]# mke2fs /dev/loop0mke2fs 1.35 (28-Feb-2004)max_blocks 262144, rsv_groups = 32, rsv_gdb = 0Filesystem label=OS type: LinuxBlock size=1024 (log=0)Fragment size=1024 (log=0)32 inodes, 256 blocks12 blocks (4.69%) reserved for the super userFirst data block=11 block group8192 blocks per group, 8192 fragments per group32 inodes per groupWriting inode tables: doneWriting superblocks and filesystem accounting information: doneThis filesystem will be automatically checked every 30 mounts or180 days, whichever comes first. Use tune2fs -c or -i to override.挂载新建的文件系统(注意mount选项里的acl标志,我们靠它来通知内核我们需要在这个文件系统中使用ACL):[root@FC3-vm opt]# mount -o rw,acl /dev/loop0 /mnt[root@FC3-vm opt]# cd /mnt[root@FC3-vm mnt]# lslost+found现在我已经得到了一个小型的文件系统。
动态ACL配置详解

IP访问控制列表算是Cisco IOS一个内在的security feature,以下是对常用的动态访问控制列表做了个总结。
Pt.1 Lock-and-Key SecurityLock-and-Key Overviewlock-and-key动态ACL使用IP动态扩展ACL过滤IP流量。
当配置了lock-and-key动态ACL 之后,临时被拒绝掉的IP流量可以获得暂时性的许可。
lock-and-key动态ACL临时修改路由器接口下已经存在的ACL,来允许IP流量到达目标设备。
之后lock-and-key动态ACL把接口状态还原。
通过lock-and-key动态ACL获得访问目标设备权限的用户,首先要开启到路由器的telnet 会话。
接着lock-and-key动态ACL自动对用户进行认证。
如果认证通过,那么用户就获得了临时性的访问权限。
Configuring Lock-and-Key配置lock-and-key动态ACL的步骤如下:1.设置动态ACL:BitsCN(config)#access-list {access-list-number} [dynamic dynamic-name [timeout minutes]] {deny|permit} telnet {source source-wildcard destination destination-wildcard}2.扩展动态ACL的绝对计时器。
可选:BitsCN(config)# access-list dynamic-extend3.定义需要应用ACL的接口:BitsCN(config)#interface {interface}4.应用ACL:BitsCN(config-if)#ip access-group {ACL}5.定义VTY线路:BitsCN(config)#line vty {line-number [ending-line-number]}6.对用户进行认证:BitsCN(config)#username {username} password {password}7.采用TACACS认证或本地认证方式。
使用acllite推理代码详解

ACL2(A Computational Logic for Applicative Common Lisp)是一个用于进行自动化推理的计算机程序。
它结合了逻辑编程和函数式编程的特点,可以应用于软件验证、形式化验证以及其他相关领域。
ACL2的推理能力主要通过ACL2lite语言来实现,本文将详细介绍ACL2lite的推理代码及其使用方法。
一、ACL2lite的基本概念ACL2lite是一个轻量级版本的ACL2,相比于ACL2,ACL2lite更加简单且易于使用。
ACL2lite的基本概念包括以下几点:1. 逻辑推理:ACL2lite允许用户定义一些逻辑公式,并通过推理得出结论。
这些推理通常是基于逻辑规则和推理规则的。
用户可以使用ACL2lite进行基本的逻辑推理操作,如证明、反驳等。
2. 函数式编程:ACL2lite支持函数式编程的特性,用户可以定义函数、进行函数调用、进行数学运算等操作。
3. 符号计算:ACL2lite可以进行符号计算,支持对符号进行求值、化简、代换等操作。
二、ACL2lite的推理代码ACL2lite的推理代码主要包括两部分:逻辑公式和推理规则。
下面将详细介绍这两部分的内容。
2.1 逻辑公式逻辑公式是ACL2lite进行推理的基础。
用户可以通过定义逻辑公式来描述问题的条件和结论,然后使用推理规则来得出结论。
逻辑公式的定义通常包括谓词、变量、逻辑连接词等。
下面是一个简单的逻辑公式的例子:```(defthm list-reverse(equal (reverse (reverse x)) x))```上面的代码定义了一个逻辑公式list-reverse,该公式表明对一个列表进行两次反转后得到的列表与原列表相等。
其中,defthm是ACL2lite中用于定义定理(逻辑公式)的关键字,list-reverse是定理的名字,括号内的表达式是该定理的内容。
2.2 推理规则ACL2lite的推理能力主要通过一些推理规则来实现。
ACL案例及说明
ACL案例及说明技术从来都是一把双刃剑,网络应用与互联网的普及在大幅提高企业的生产经营效率的同时,也带来了诸如数据的安全性,员工利用互联网做与工作不相干事等负面影响。
如何将一个网络有效的管理起来,尽可能的降低网络所带来的负面影响就成了摆在网络管理员面前的一个重要课题。
A公司的某位可怜的网管目前就面临了一堆这样的问题。
A公司建设了一个企业网,并通过一台路由器接入到互联网。
在网络核心使用一台基于IOS的多层交换机,所有的二层交换机也为可管理的基于IOS的交换机,在公司内部使用了VLAN技术,按照功能的不同分为了6个VLAN。
分别是网络设备与网管(VLAN1,10.1.1.0/24)、内部服务器(VLAN2)、Internet连接(VLAN3)、财务部(VLAN4)、市场部(VLAN5)、研发部门(VLAN6),出口路由器上Fa0/0接公司内部网,通过s0/0连接到Internet。
每个网段的三层设备(也就是客户机上的缺省网关)地址都从高位向下分配,所有的其它节点地址均从低位向上分配。
该网络的拓朴如下图所示:自从网络建成后麻烦就一直没断过,一会儿有人试图登录网络设备要捣乱;一会儿领导又在抱怨说互联网开通后,员工成天就知道泡网;一会儿财务的人又说研发部门的员工看了不该看的数据。
这些抱怨都找这位可怜的网管,搞得他头都大了。
那有什么办法能够解决这些问题呢?答案就是使用网络层的访问限制控制技术――访问控制列表(下文简称ACL)。
那么,什么是ACL呢?ACL是种什么样的技术,它能做什么,又存在一些什么样的局限性呢?ACL的基本原理、功能与局限性网络中常说的ACL是Cisco IOS所提供的一种访问控制技术,初期仅在路由器上支持,近些年来已经扩展到三层交换机,部分最新的二层交换机如2950之类也开始提供ACL的支持。
只不过支持的特性不是那么完善而已。
在其它厂商的路由器或多层交换机上也提供类似的技术,不过名称和配置方式都可能有细微的差别。
acl2名称和反向
基于名称的访问控制列表不管是标准访问控制列表还是扩展访问控制列表都有一个弊端,那就是当设置好ACL的规则后发现其中的某条有问题,希望进行修改或删除的话只能将全部ACL信息都删除。
也就是说修改一条或删除一条都会影响到整个ACL列表。
可以用基于名称的访问控制列表来解决这个问题。
一、基于名称的访问控制列表的格式:ip access-list [standard|extended] [ACL名称]例如:ip access-list standard softer就建立了一个名为softer的标准访问控制列表。
二、基于名称的访问控制列表的使用方法:当我们建立了一个基于名称的访问列表后就可以进入到这个ACL中进行配置了。
例如我们添加三条ACL规则permit 1.1.1.1 0.0.0.0permit 2.2.2.2 0.0.0.0permit 3.3.3.3 0.0.0.0如果我们发现第二条命令应该是2.2.2.1而不是2.2.2.2,如果使用不是基于名称的访问控制列表的话,使用no permit 2.2.2.2 0.0.0.0后整个ACL 信息都会被删除掉。
正是因为使用了基于名称的访问控制列表,我们使用no p ermit 2.2.2.2 0.0.0.0后第一条和第三条指令依然存在。
总结:如果设置ACL的规则比较多的话,应该使用基于名称的访问控制列表进行管理,这样可以减轻很多后期维护的工作,方便我们随时进行调整ACL 规则。
Cisco路由器配置ACL详解之反向访问控制列表反向访问控制列表:我们使用访问控制列表除了合理管理网络访问以外还有一个更重要的方面,那就是防范病毒,我们可以将平时常见病毒传播使用的端口进行过滤,将使用这些端口的数据包丢弃。
这样就可以有效的防范病毒的攻击。
不过即使再科学的访问控制列表规则也可能会因为未知病毒的传播而无效,毕竟未知病毒使用的端口是我们无法估计的,而且随着防范病毒数量的增多会造成访问控制列表规则过多,在一定程度上影响了网络访问的速度。
怎么设置NETGEAR的MACACL功能
怎么设置NETGEAR的MAC ACL功能美国网件公司一直致力于网络技术创新,专注于产品的可靠性以及易用性提升,其生产的路由器设备功能强大,那么你知道怎么设置NETGEAR的MAC ACL功能吗?下面是店铺整理的一些关于怎么设置NETGEAR的MAC ACL功能的相关资料,供你参考。
设置NETGEAR的MAC ACL功能的方法:一、网络拓扑图设置环境交换机型号:FS752TPFW:V5.0.2.15实现目的在端口48上阻止PC1(MAC地址为:00:26:f2:b2:76:31)访问其他电脑和网络。
二、MAC ACL设置步骤详解新建MAC ACL进入Security > ACL > Basic > MAC ACL菜单,新建一个MAC ACL如“denymac1”,点击右下角的ADD添加。
添加 MAC ACL 规则进入Security > ACL > Basic > MAC ACL菜单,添加一条MAC 规则,即阻止00:26:f2:b2:76:31访问任何网络。
ID (1 to 10):输入规则编号1Action:操作,可选择Permit(允许)和Deny(禁止),这里选DenyMatch Every:可以选择False和True。
最后一条规则选True,否则选False,由于默认规则为拒绝所有,这里先选False Destination MAC:目的MAC地址,这里填入ff:ff:ff:ff:ff:ff,表示所有电脑Destination MAC Mask:目的通配符掩码,这里填入ff:ff:ff:ff:ff:ffSource MAC:源MAC地址,这里填入一台PC1的MAC地址00:26:f2:b2:76:31Source MAC Mask:通配符掩码,类似于IP ACL的反掩码,填入00:00:00:00:00:00表示指定这一个MAC,类似反掩码的0.0.0.0。
CISCO的ACL文档
Configuring IP Access ListsContentsIntroduction Prerequisites Requirements Components Used Conventions ACL Concepts MasksACL Summarization Process ACLsDefine Ports and Message Types Apply ACLsDefine In, Out, Inbound, Outbound, Source, and Destination Edit ACLs Troubleshoot Types of IP ACLs Network Diagram Standard ACLs Extended ACLsLock and Key (Dynamic ACLs) IP Named ACLs Reflexive ACLsTime-Based ACLs Using Time Ranges Commented IP ACL Entries Context-Based Access Control Authentication Proxy Turbo ACLsDistributed Time-Based ACLs Receive ACLsInfrastructure Protection ACLs Transit ACLsCisco Support Community - Featured Conversations Related InformationIntroductionThis document describes how IP access control lists (ACLs) can filter network traffic. It also contains brief descriptions of the IP ACL types, featureavailability, and an example of use in a network.TAC Notice: What's Changing on TAC WebHelp us help you.Please rate thisdocument.Excellent GoodAverageFair PoorThis document solvedmy problem.YesNoJust browsing Suggestions for improvement:(256 character limit)SendAccess the Software Advisor (registered customers only) tool in order to determine the support of some of the more advanced Cisco IOS® IP ACL features.RFC 1700 contains assigned numbers of well-known ports. RFC 1918 contains address allocation for private Internets, IP addresses which should not normally be seen on the Internet.Note: ACLs might also be used for purposes other than to filter IP traffic, for example, defining traffic to Network Address Translate (NAT) or encrypt, or filtering non-IP protocols such as AppleTalk or IPX.A discussion of these functions is outside the scope of this document.PrerequisitesRequirementsThere are no specific prerequisites for this document. The concepts discussed are present in Cisco IOS® Software Releases 8.3 or later. This is noted under each access list feature.Components UsedThis document discusses various types of ACLs. Some of these are present since Cisco IOS Software Releases 8.3 and others were introduced in later software releases. This is noted in the discussion of each type.The information in this document was created from the devices in a specific lab environment. All of the devices used in this document started with a cleared (default) configuration. If your network is live, make sure that you understand the potential impact of any command.ConventionsRefer to Cisco Technical Tips Conventions for more information on document conventions.ACL ConceptsThis section describes ACL concepts.MasksMasks are used with IP addresses in IP ACLs to specify what should be permitted and denied. Masks in order to configure IP addresses on interfaces start with 255 and have the large values on the left side, for example, IP address 209.165.202.129 with a 255.255.255.224 mask. Masks for IP ACLs are the reverse, for example, mask 0.0.0.255. This is sometimes called an inverse mask or a wildcard mask. When the value of the mask is broken down into binary (0s and 1s), the results determine which address bits are to be considered in processing the traffic. A 0 indicates that the address bits must be considered (exact match); a 1 in the mask is a "don't care". This table further explains the concept.Mask Examplenetwork addressBased on the binary mask, you can see that the first three sets (octets) must match the given binary network address exactly (00001010.00000001.00000001). The last set of numbers are "don'tcares" (.11111111). Therefore, all traffic that begins with 10.1.1. matches since the last octet is "don't care". Therefore, with this mask, network addresses 10.1.1.1 through 10.1.1.255 (10.1.1.x) are processed.Subtract the normal mask from 255.255.255.255 in order to determine the ACL inverse mask. In this example, the inverse mask is determined for network address 172.16.1.0 with a normal mask of 255.255.255.0.●255.255.255.255 - 255.255.255.0 (normal mask) = 0.0.0.255 (inverse mask)Note these ACL equivalents.●The source/source-wildcard of 0.0.0.0/255.255.255.255 means "any". ●The source/wildcard of 10.1.1.2/0.0.0.0 is the same as "host 10.1.1.2".ACL SummarizationNote: Subnet masks can also be represented as a fixed length notation. For example, 192.168.10.0/24 represents 192.168.10.0 255.255.255.0.This list describes how to summarize a range of networks into a single network for ACL optimization. Consider these networks.192.168.32.0/24 192.168.33.0/24 192.168.34.0/24 192.168.35.0/24 192.168.36.0/24 192.168.37.0/24 192.168.38.0/24 192.168.39.0/24The first two octets and the last octet are the same for each network. This table is an explanation of how to summarize these into a single network.The third octet for the previous networks can be written as seen in this table, according to the octet bit position and address value for each bit.(traffic that is tobe processed) 10.1.1.0mask0.0.0.255network address(binary) 00001010.00000001.00000001.00000000mask (binary)00000000.00000000.00000000.11111111Decimal128 64 32 16 8 4 2 132 0 0 1 0 0 0 0 033 0 0 1 0 0 0 0 134 0 0 1 0 0 0 1 035 0 0 1 0 0 0 1 136 0 0 1 0 0 1 0 037 0 0 1 0 0 1 0 138 0 0 1 0 0 1 1 039 0 0 1 0 0 1 1 1M M M M M D D DSince the first five bits match, the previous eight networks can be summarized into one network (192.168.32.0/21 or 192.168.32.0 255.255.248.0). All eight possible combinations of the three low-order bits are relevant for the network ranges in question. This command defines an ACL that permits this network. If you subtract 255.255.248.0 (normal mask) from 255.255.255.255, it yields 0.0.7.255.access-list acl_permit permit ip 192.168.32.0 0.0.7.255Consider this set of networks for further explanation.192.168.146.0/24192.168.147.0/24192.168.148.0/24192.168.149.0/24The first two octets and the last octet are the same for each network. This table is an explanation of how to summarize these.The third octet for the previous networks can be written as seen in this table, according to the octet bit position and address value for each bit.Decimal128 64 32 16 8 4 2 1146 1 0 0 1 0 0 1 0147 1 0 0 1 0 0 1 1148 1 0 0 1 0 1 0 0149 1 0 0 1 0 1 0 1M M M M M ? ? ?Unlike the previous example, you cannot summarize these networks into a single network. If they are summarized to a single network, they become192.168.144.0/21 because there are five bits similar in the third octet. This summarized network 192.168.144.0/21 covers a range of networks from 192.168.144.0 to 192.168.151.0. Among these, 192.168.144.0, 192.168.145.0, 192.168.150.0, and 192.168.151.0 networks are not in the given list of four networks. In order to cover the specific networks in question,you need a minimum of two summarized networks. The given four networks can be summarized into these two networks:●For networks 192.168.146.x and 192.168.147.x, all bits match except for the last one, which is a"don't care." This can be written as 192.168.146.0/23 (or 192.168.146.0 255.255.254.0).●For networks 192.168.148.x and 192.168.149.x, all bits match except for the last one, which is a"don't care." This can be written as 192.168.148.0/23 (or 192.168.148.0 255.255.254.0).This output defines a summarized ACL for the above networks.!--- This command is used to allow access access for devices with IP!--- addresses in the range from 192.168.146.0 to 192.168.147.254.access-list 10 permit 192.168.146.0 0.0.1.255!--- This command is used to allow access access for devices with IP!--- addresses in the range from 192.168.148.0 to 192.168.149.254access-list 10 permit 192.168.148.0 0.0.1.255Process ACLsTraffic that comes into the router is compared to ACL entries based on the order that the entries occur in the router. New statements are added to the end of the list. The router continues to look until it has a match. If no matches are found when the router reaches the end of the list, the traffic is denied. For this reason, you should have the frequently hit entries at the top of the list. There is an implied deny for traffic that is not permitted. A single-entry ACL with only one deny entry has the effect of denying all traffic. You must have at least one permit statement in an ACL or all traffic is blocked. These two ACLs (101 and 102) have the same effect.!--- This command is used to permit IP traffic from 10.1.1.0!--- network to 172.16.1.0 network. All packets with a source!--- address not in this range will be rejected.access-list 101 permit ip 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255!--- This command is used to permit IP traffic from 10.1.1.0!--- network to 172.16.1.0 network. All packets with a source!--- address not in this range will be rejected.access-list 102 permit ip 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255access-list 102 deny ip any anyIn this example, the last entry is sufficient. You do not need the first three entries because TCP includes Telnet, and IP includes TCP, User Datagram Protocol (UDP), and Internet Control Message Protocol (ICMP).!--- This command is used to permit Telnet traffic!--- from machine 10.1.1.2 to machine 172.16.1.1.access-list 101 permit tcp host 10.1.1.2 host 172.16.1.1 eq telnet!--- This command is used to permit tcp traffic from!--- 10.1.1.2 host machine to 172.16.1.1 host machine.access-list 101 permit tcp host 10.1.1.2 host 172.16.1.1!--- This command is used to permit udp traffic from!--- 10.1.1.2 host machine to 172.16.1.1 host machine.access-list 101 permit udp host 10.1.1.2 host 172.16.1.1!--- This command is used to permit ip traffic from!--- 10.1.1.0 network to 172.16.1.10 network.access-list 101 permit ip 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255Define Ports and Message TypesIn addition to defining ACL source and destination, it is possible to define ports, ICMP message types,ICMP and other parameters. A good source of information for well-known ports is RFC 1700 . message types are explained in RFC 792 .The router can display descriptive text on some of the well-known ports. Use a ? for help.access-list 102 permit tcp host 10.1.1.1 host 172.16.1.1 eq ?bgp Border Gateway Protocol (179)chargen Character generator (19)cmd Remote commands (rcmd, 514)During configuration, the router also converts numeric values to more user-friendly values. This is an example where you type the ICMP message type number and it causes the router to convert the number to a name.access-list 102 permit icmp host 10.1.1.1 host 172.16.1.1 14becomesaccess-list 102 permit icmp host 10.1.1.1 host 172.16.1.1 timestamp-reply Apply ACLsYou can define ACLs without applying them. But, the ACLs have no effect until they are applied to the interface of the router. It is a good practice to apply the ACL on the interface closest to the source of the traffic. As shown in this example, when you try to block traffic from source to destination, you can apply an inbound ACL to E0 on router A instead of an outbound list to E1 on router C. An access-list has a deny ip any any implicitly at the end of any access-list. If traffic is related to a DHCP request andif it is not explicity permitted, the traffic is dropped because when you look at DHCP request in IP, the source address is s=0.0.0.0 (Ethernet1/0), d=255.255.255.255, len 604, rcvd 2 UDP src=68, dst=67. Note that the source IP address is 0.0.0.0 and destination address is 255.255.255.255. Source port is 68 and destination 67. Hence, you should permit this kind of traffic in your access-list else the traffic is dropped due to implicit deny at the end of the statement.Note: For UDP traffic to pass through, UDP traffic must also be permited explicitly by the ACL.Define In, Out, Inbound, Outbound, Source, and DestinationThe router uses the terms in, out, source, and destination as references. Traffic on the router can be compared to traffic on the highway. If you were a law enforcement officer in Pennsylvania and wanted to stop a truck going from Maryland to New York, the source of the truck is Maryland and the destination of the truck is New York. The roadblock could be applied at the Pennsylvania–New York border (out) or the Maryland–Pennsylvania border (in).When you refer to a router, these terms have these meanings.●Out—Traffic that has already been through the router and leaves the interface. The source iswhere it has been, on the other side of the router, and the destination is where it goes.●In—Traffic that arrives on the interface and then goes through the router. The source is where ithas been and the destination is where it goes, on the other side of the router.●Inbound —If the access list is inbound, when the router receives a packet, the Cisco IOS softwarechecks the criteria statements of the access list for a match. If the packet is permitted, the software continues to process the packet. If the packet is denied, the software discards the packet.●Outbound—If the access list is outbound, after the software receives and routes a packet to theoutbound interface, the software checks the criteria statements of the access list for a match. If the packet is permitted, the software transmits the packet. If the packet is denied, the softwarediscards the packet.The in ACL has a source on a segment of the interface to which it is applied and a destination off of any other interface. The out ACL has a source on a segment of any interface other than the interface to which it is applied and a destination off of the interface to which it is applied.Edit ACLsWhen you edit an ACL, it requires special attention. For example, if you intend to delete a specific line from a numbered ACL that exists as shown here, the entire ACL is deleted.!--- The access-list 101 denies icmp from any to any network!--- but permits IP traffic from any to any network.router#configure terminalEnter configuration commands, one per line. End with CNTL/Z.router(config)#access-list 101 deny icmp any anyrouter(config)#access-list 101 permit ip any anyrouter(config)#^Zrouter#show access-listExtended IP access list 101deny icmp any anypermit ip any anyrouter#*Mar 9 00:43:12.784: %SYS-5-CONFIG_I: Configured from console by console router#configure terminalEnter configuration commands, one per line. End with CNTL/Z.router(config)#no access-list 101 deny icmp any anyrouter(config)#^Zrouter#show access-listrouter#*Mar 9 00:43:29.832: %SYS-5-CONFIG_I: Configured from console by console Copy the configuration of the router to a TFTP server or a text editor such as Notepad in order to edit numbered ACLs. Then make any changes and copy the configuration back to the router.You can also do this.router#configure terminalEnter configuration commands, one per line.router(config)#ip access-list extended test!--- Permits IP traffic from 2.2.2.2 host machine to 3.3.3.3 host machine.router(config-ext-nacl)#permit ip host 2.2.2.2 host 3.3.3.3!--- Permits www traffic from 1.1.1.1 host machine to 5.5.5.5 host machine.router(config-ext-nacl)#permit tcp host 1.1.1.1 host 5.5.5.5 eq www!--- Permits icmp traffic from any to any network.router(config-ext-nacl)#permit icmp any any!--- Permits dns traffic from 6.6.6.6 host machine to 10.10.10.0 network.router(config-ext-nacl)#permit udp host 6.6.6.6 10.10.10.0 0.0.0.255 eq domai router(config-ext-nacl)#^Z1d00h: %SYS-5-CONFIG_I: Configured from console by consoles-lrouter#show access-listExtended IP access list testpermit ip host 2.2.2.2 host 3.3.3.3permit tcp host 1.1.1.1 host 5.5.5.5 eq wwwpermit icmp any anypermit udp host 6.6.6.6 10.10.10.0 0.0.0.255 eq domainAny deletions are removed from the ACL and any additions are made to the end of the ACL.router#configure terminalEnter configuration commands, one per line. End with CNTL/Z.router(config)#ip access-list extended test!--- ACL entry deleted.router(config-ext-nacl)#no permit icmp any any!--- ACL entry added.router(config-ext-nacl)#permit gre host 4.4.4.4 host 8.8.8.8router(config-ext-nacl)#^Z1d00h: %SYS-5-CONFIG_I: Configured from console by consoles-lrouter#show access-listExtended IP access list testpermit ip host 2.2.2.2 host 3.3.3.3permit tcp host 1.1.1.1 host 5.5.5.5 eq wwwpermit udp host 6.6.6.6 10.10.10.0 0.0.0.255 eq domainpermit gre host 4.4.4.4 host 8.8.8.8You can also add ACL lines to numbered standard or numbered extended ACLs by sequence number in Cisco IOS. This is a sample of the configuration:Configure the extended ACL in this way:Router(config)#access-list 101 permit tcp any anyRouter(config)#access-list 101 permit udp any anyRouter(config)#access-list 101 permit icmp any anyRouter(config)#exitRouter#Issue the show access-list command in order to view the ACL entries. The sequence numbers such as 10, 20, and 30 also appear here.Router#show access-listExtended IP access list 10110 permit tcp any any20 permit udp any any30 permit icmp any anyAdd the entry for the access list 101 with the sequence number 5.Example 1:Router#configure terminalEnter configuration commands, one per line. End with CNTL/Z.Router(config)#ip access-list extended 101Router(config-ext-nacl)#5 deny tcp any any eq telnetRouter(config-ext-nacl)#exitRouter(config)#exitRouter#In the show access-list command output, the sequence number 5 ACL is added as the first entry to the access-list 101.Router#show access-listExtended IP access list 1015 deny tcp any any eq telnet10 permit tcp any any20 permit udp any any30 permit icmp any anyRouter#Example 2:internetrouter#show access-listsExtended IP access list 10110 permit tcp any any15 permit tcp any host 172.162.2.920 permit udp host 172.16.1.21 any30 permit udp host 172.16.1.22 anyinternetrouter#configure terminalEnter configuration commands, one per line. End with CNTL/Z.internetrouter(config)#ip access-list extended 101internetrouter(config-ext-nacl)#18 per tcp any host 172.162.2.11internetrouter(config-ext-nacl)#^Zinternetrouter#show access-listsExtended IP access list 10110 permit tcp any any15 permit tcp any host 172.162.2.918 permit tcp any host 172.162.2.1120 permit udp host 172.16.1.21 any30 permit udp host 172.16.1.22 anyinternetrouter#Similarly, you can configure the standard access list in this way:internetrouter(config)#access-list 2 permit 172.16.1.2internetrouter(config)#access-list 2 permit 172.16.1.10internetrouter(config)#access-list 2 permit 172.16.1.11internetrouter#show access-listsStandard IP access list 230 permit 172.16.1.1120 permit 172.16.1.1010 permit 172.16.1.2internetrouter(config)#ip access-list standard 2internetrouter(config-std-nacl)#25 per 172.16.1.7internetrouter(config-std-nacl)#15 per 172.16.1.16internetrouter#show access-listsStandard IP access list 215 permit 172.16.1.1630 permit 172.16.1.1120 permit 172.16.1.1025 permit 172.16.1.710 permit 172.16.1.2The major difference in a standard access list is that the Cisco IOS adds an entry by descending order of the IP address, not on a sequence number.This example shows the different entries, for example, how to permit an IP address (192.168.100.0) or the networks (10.10.10.0).internetrouter#show access-listsStandard IP access list 1910 permit 192.168.100.015 permit 10.10.10.0, wildcard bits 0.0.0.25519 permit 201.101.110.0, wildcard bits 0.0.0.25525 deny anyAdd the entry in access list 2 in order to permit the IP Address 172.22.1.1:internetrouter(config)#ip access-list standard 2internetrouter(config-std-nacl)#18 permit 172.22.1.1This entry is added in the top of the list in order to give priority to the specific IP address rather than network.internetrouter#show access-listsStandard IP access list 1910 permit 192.168.100.018 permit 172.22.1.115 permit 10.10.10.0, wildcard bits 0.0.0.25519 permit 201.101.110.0, wildcard bits 0.0.0.25525 deny anyNote: The previous ACLs are not supported in Security Appliance such as the ASA/PIX Firewall.Guidelines to change access-lists when they are applied to crypto maps●If you add to an existing access-list configuration, there is no need to remove the crypto map. Ifyou add to them directly without the removal of the crypto map, then that is supported andacceptable.●If you need to modify or delete access-list entry from an existing access-lists, then you mustremove the crypto map from the interface. After you remove crypto map, make all changes to the access-list and re-add the crypto map. If you make changes such as the deletion of the access-list without the removal of the crypto map, this is not supported and can result in unpredictablebehavior.TroubleshootHow do I remove an ACL from an interface?Go into configuration mode and enter no in front of the access-group command, as shown in this example, in order to remove an ACL from an interface.interface <interface>no ip access-group <acl-number> in|outWhat do I do when too much traffic is denied?If too much traffic is denied, study the logic of your list or try to define and apply an additional broader list. The show ip access-lists command provides a packet count that shows which ACL entry is hit.The log keyword at the end of the individual ACL entries shows the ACL number and whether the packet was permitted or denied, in addition to port-specific information.Note: The log-input keyword exists in Cisco IOS Software Release 11.2 and later, and in certain Cisco IOS Software Release 11.1 based software created specifically for the service provider market. Older software does not support this keyword. Use of this keyword includes the input interface and source MAC address where applicable.How do I debug at the packet level that uses a Cisco router?This procedure explains the debug process. Before you begin, be certain that there are no currently applied ACLs, that there is an ACL, and that fast switching is not disabled.Note: Use extreme caution when you debug a system with heavy traffic. Use an ACL in order to debug specific traffic. But, be sure of the process and the traffic flow.e the access-list command in order to capture the desired data.In this example, the data capture is set for the destination address of10.2.6.6 or the source address of 10.2.6.6.access-list 101 permit ip any host 10.2.6.6access-list 101 permit ip host 10.2.6.6 any2.Disable fast switching on the interfaces involved. You only see the first packet if fast switching isnot disabled.config interfaceno ip route-cachee the terminal monitor command in enable mode in order to display debug command outputand system error messages for the current terminal and session.e the debug ip packet 101 or debug ip packet 101 detail command in order to begin thedebug process.5.Execute the no debug all command in enable mode and the interface configuration command inorder to stop the debug process.6.Restart caching.config interfaceip route-cacheTypes of IP ACLsThis section of the document describes ACL types.Network DiagramStandard ACLsStandard ACLs are the oldest type of ACL. They date back to as early as Cisco IOS Software Release 8.3. Standard ACLs control traffic by the comparison of the source address of the IP packets to the addresses configured in the ACL.This is the command syntax format of a standard ACL.access-list access-list-number {permit|deny}{host|source source-wildcard|any}In all software releases, the access-list-number can be anything from 1 to 99. In Cisco IOS Software Release 12.0.1, standard ACLs begin to use additional numbers (1300 to 1999). These additional numbers are referred to as expanded IP ACLs. Cisco IOS Software Release 11.2 added the ability to use list name in standard ACLs.A source/source-wildcard setting of 0.0.0.0/255.255.255.255 can be specified as any. The wildcard can be omitted if it is all zeros. Therefore, host 10.1.1.2 0.0.0.0 is the same as host 10.1.1.2.After the ACL is defined, it must be applied to the interface (inbound or outbound). In early software releases, out was the default when a keyword out or in was not specified. The direction must be specified in later software releases.interface <interface>ip access-group number {in|out}This is an example of the use of a standard ACL in order to block all traffic except that from source 10.1.1.x.interface Ethernet0/0ip address 10.1.1.1 255.255.255.0ip access-group 1 inaccess-list 1 permit 10.1.1.0 0.0.0.255Extended ACLsExtended ACLs were introduced in Cisco IOS Software Release 8.3. Extended ACLs control traffic by the comparison of the source and destination addresses of the IP packets to the addresses configured in the ACL.This is the command syntax format of extended ACLs. Lines are wrapped here for spacing considerations.IPaccess-list access-list-number[dynamic dynamic-name [timeout minutes]]{deny|permit} protocol source source-wildcarddestination destination-wildcard [precedence precedence][tos tos] [log|log-input] [time-range time-range-name]ICMPaccess-list access-list-number[dynamic dynamic-name [timeout minutes]]{deny|permit} icmp source source-wildcarddestination destination-wildcard[icmp-type [icmp-code] |icmp-message][precedence precedence] [tos tos] [log|log-input][time-range time-range-name]TCPaccess-list access-list-number[dynamic dynamic-name [timeout minutes]]{deny|permit} tcp source source-wildcard [operator [port]]destination destination-wildcard [operator [port]][established] [precedence precedence] [tos tos][log|log-input] [time-range time-range-name]UDPaccess-list access-list-number[dynamic dynamic-name [timeout minutes]]{deny|permit} udp source source-wildcard [operator [port]]destination destination-wildcard [operator [port]][precedence precedence] [tos tos] [log|log-input][time-range time-range-name]In all software releases, the access-list-number can be 101 to 199. In Cisco IOS Software Release 12.0.1, extended ACLs begin to use additional numbers (2000 to 2699). These additional numbers are referred to as expanded IP ACLs. Cisco IOS Software Release 11.2 added the ability to use list name in extended ACLs.The value of 0.0.0.0/255.255.255.255 can be specified as any. After the ACL is defined, it must be applied to the interface (inbound or outbound). In early software releases, out was the default when a keyword out or in was not specified. The direction must be specified in later software releases.interface <interface>ip access-group {number|name} {in|out}This extended ACL is used to permit traffic on the 10.1.1.x network (inside) and to receive ping responses from the outside while it prevents unsolicited pings from people outside, permitting all other traffic.interface Ethernet0/1ip address 172.16.1.2 255.255.255.0ip access-group 101 inaccess-list 101 deny icmp any 10.1.1.0 0.0.0.255 echoaccess-list 101 permit ip any 10.1.1.0 0.0.0.255Note: Some applications such as network management require pings for a keepalive function. If this is the case, you might wish to limit blocking inbound pings or be more granular in permitted/denied IPs. Lock and Key (Dynamic ACLs)Lock and key, also known as dynamic ACLs, was introduced in Cisco IOS Software Release 11.1. This feature is dependent on Telnet, authentication (local or remote), and extended ACLs.Lock and key configuration starts with the application of an extended ACL to block traffic through the router. Users that want to traverse the router are blocked by the extended ACL until they Telnet to the router and are authenticated. The Telnet connection then drops and a single-entry dynamic ACL is added to the extended ACL that exists. This permits traffic for a particular time period; idle and absolute timeouts are possible.This is the command syntax format for lock and key configuration with local authentication.username user-name password passwordinterface <interface>ip access-group {number|name} {in|out}The single-entry ACL in this command is dynamically added to the ACL that exists after authentication.access-list access-list-number dynamic name {permit|deny} [protocol]{source source-wildcard|any} {destination destination-wildcard|any}[precedence precedence][tos tos][established] [log|log-input][operator destination-port|destination port]line vty line_rangelogin localThis is a basic example of lock and key.username test password 0 test!--- Ten (minutes) is the idle timeout.username test autocommand access-enable host timeout 10interface Ethernet0/0ip address 10.1.1.1 255.255.255.0ip access-group 101 inaccess-list 101 permit tcp any host 10.1.1.1 eq telnet!--- 15 (minutes) is the absolute timeout.。